A new experiment found that a falling quantum wave behaves just as Einstein’s equivalence principle predicts.
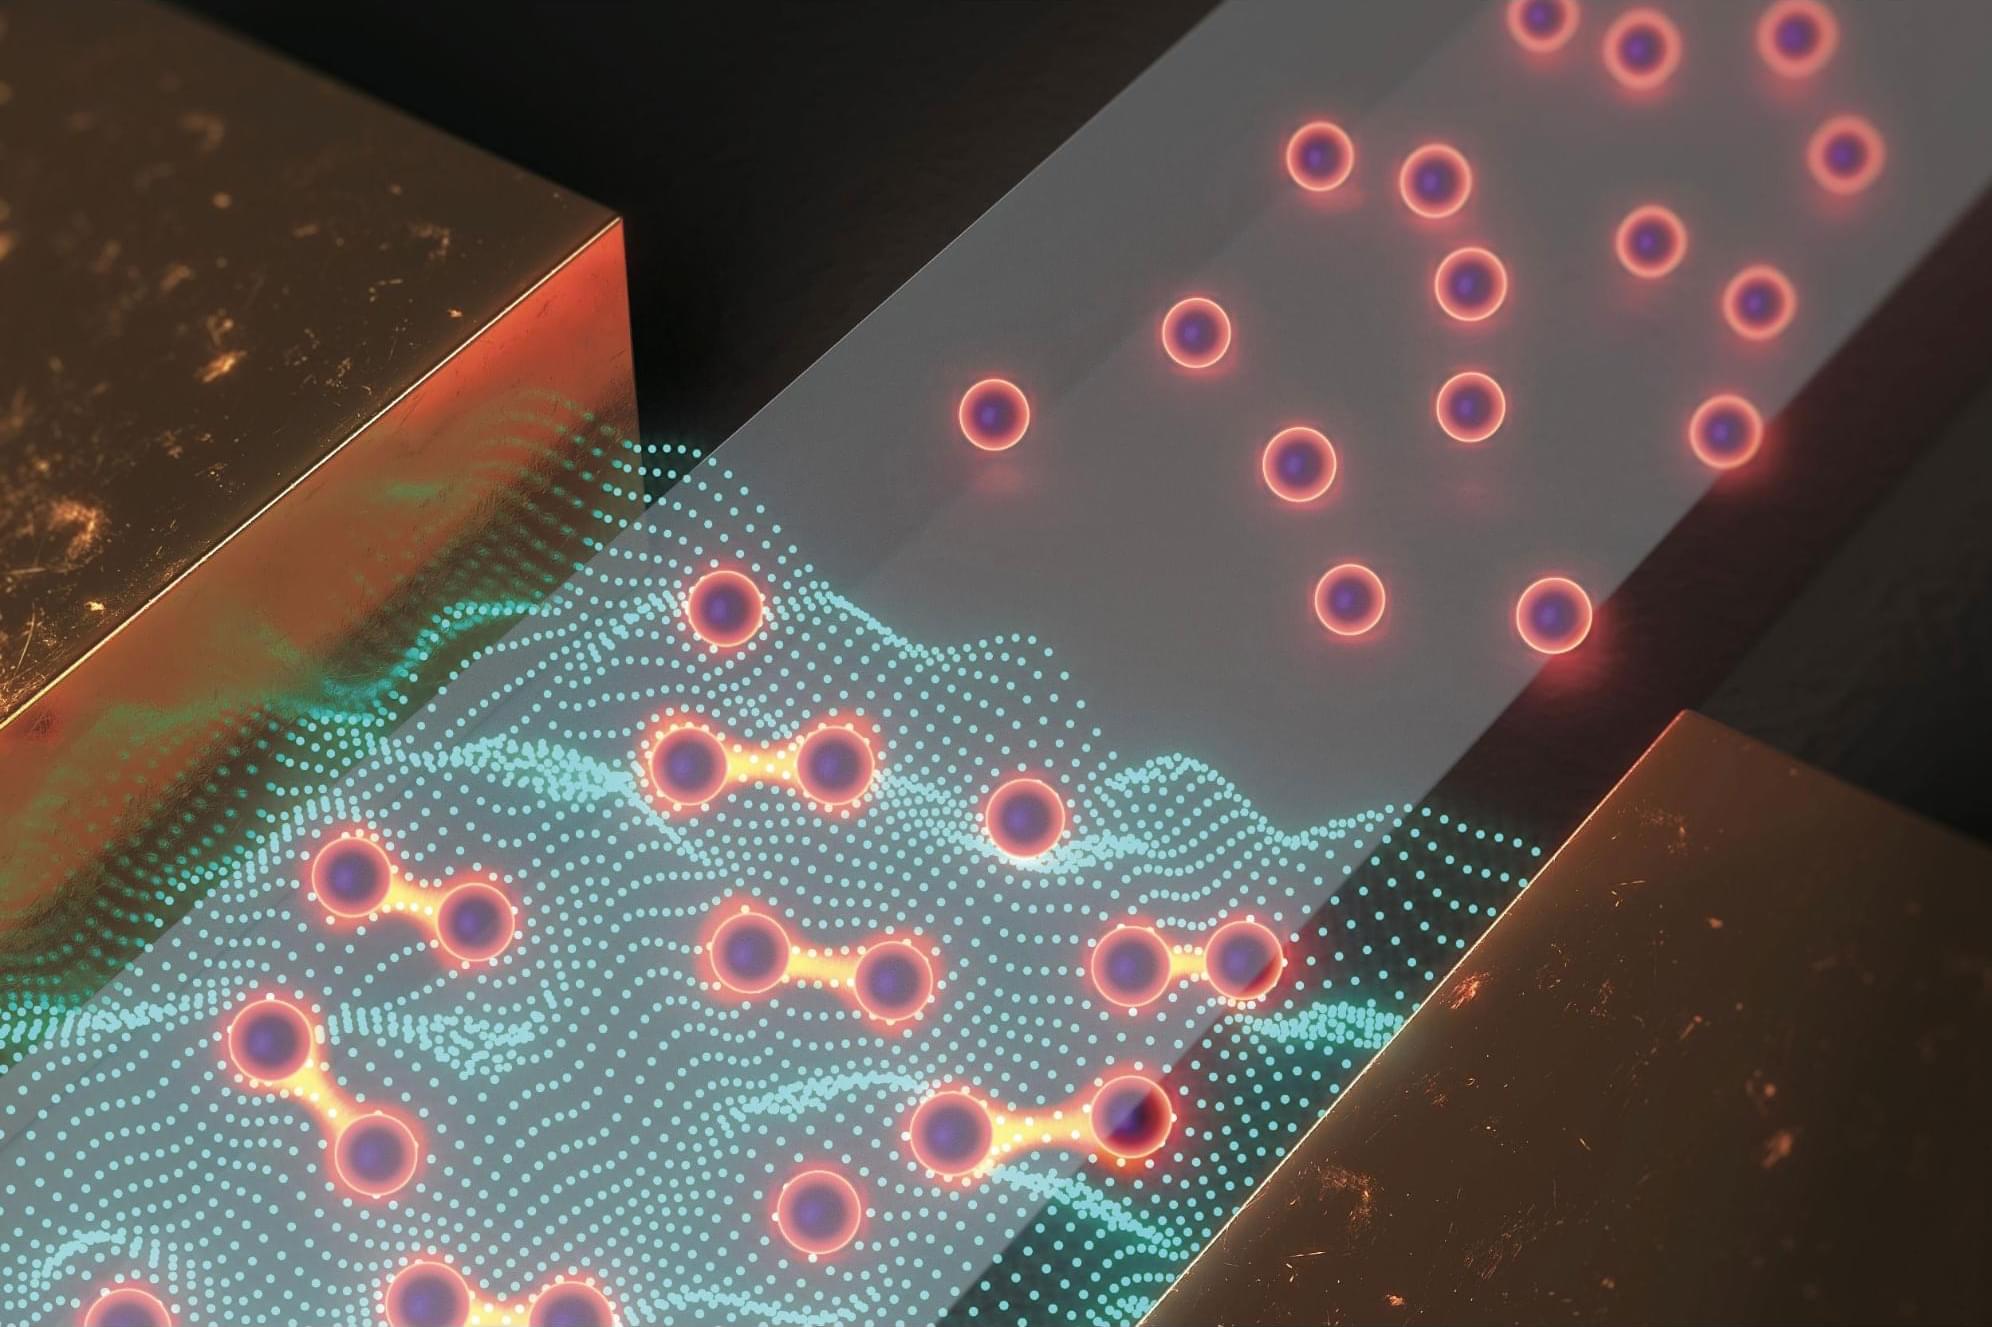
Researchers used a specially designed cavity to strengthen quantum vacuum fluctuations and enhance superconductivity in a thin material.
Empty space is not truly empty. Even a vacuum contains restless quantum fluctuations, and researchers have now shown for the first time that these normally subtle effects can be engineered to strengthen superconductivity.
The work, led by Changgan Zeng and Guanghui Cheng of the University of Science and Technology of China of the Chinese Academy of Sciences, with Qingdong Jiang of Shanghai Jiao Tong University, Frank Wilczek of the Massachusetts Institute of Technology, and other collaborators, was published in Nature.
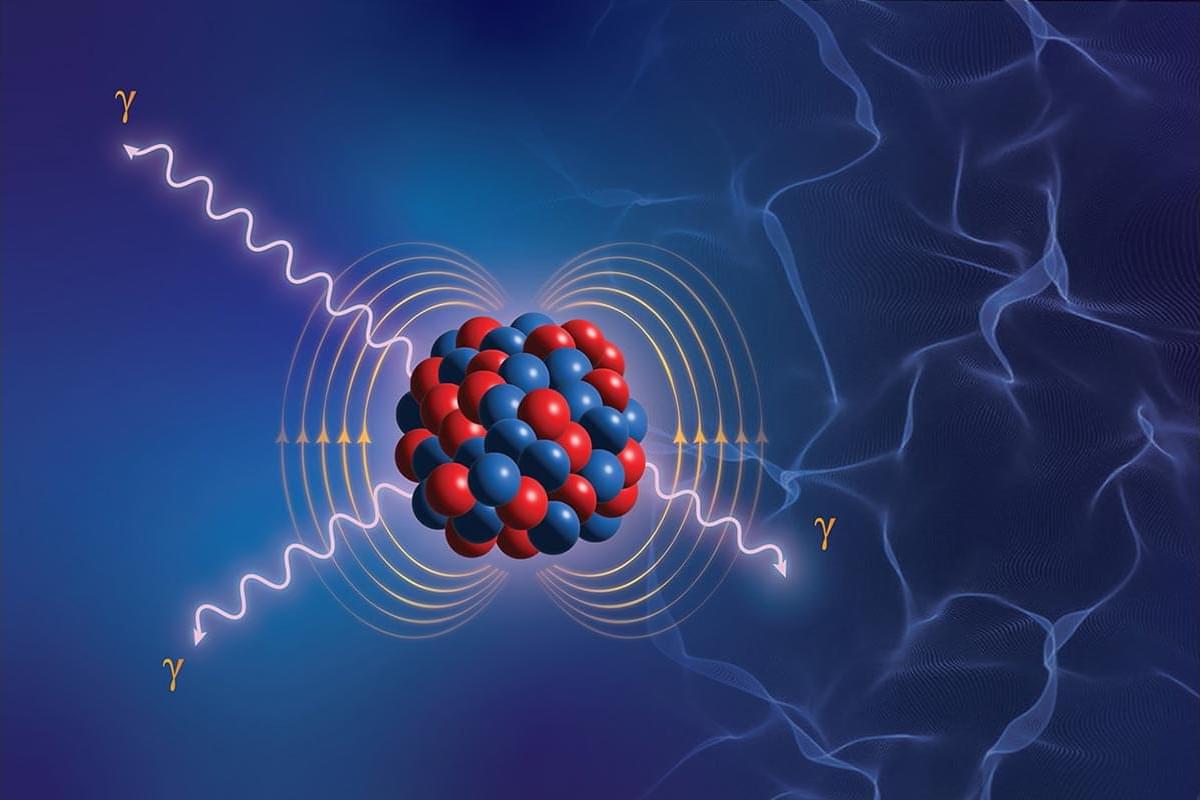
Scientists have traced a decades-old gamma-ray mystery to hidden magnetic transitions inside atomic nuclei.
For decades, nuclear physicists have faced a puzzling question: why do some atomic nuclei release far more low-energy gamma rays than expected?
A new study led by the Facility for Rare Isotope Beams (FRIB), with contributions from scientists at Lawrence Livermore National Laboratory (LLNL), may finally provide the answer. Published in Nature, the research offers new insight into the inner workings of atomic nuclei and could have important implications for astrophysics, nuclear energy, national security, and nuclear forensics.
A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation.
The vulnerability in question is CVE-2026–89026 (CVSS v3.1 score: 9.8/CVSS v4.0 score: 9.3), which can allow an unauthenticated remote attacker to execute arbitrary operating system (OS) commands by taking advantage of a hard-coded JSON Web Token (JWT) signing key.
The Issabel Framework “contains a hard-coded HS256 JWT signing key in the pbxapi index.php file that is identical across every installation, allowing unauthenticated remote attackers to forge valid bearer tokens,” VulnCheck said in an alert.
Researchers showed one browser extension could hijack AI features in five Chromium products; some demos could access files, sensors, and browser data.
Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories.
Before the repository spread, the assistant recommended software that the attacker had poisoned, and the recommendation was accepted. The worm stole repository secrets and source code for the company’s products.
The case appears in Mandiant’s September 2026 report. The public case study does not say when the intrusion happened or how the attacker took over the active coding-assistant session.
Back in June 2026, Google shipped patches for a high-severity flaw in Android’s Framework component (CVE-2025–48595, CVSS score: 8.4) that it said came under active exploitation.
Update
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on September 16, 2026, added CVE-2026–58704 to its Known Exploited Vulnerabilities (KEV) catalog, requiring Federal Civilian Executive Branch (FCEB) agencies to apply the fixes by September 19, 2026.
A banking malware operation active since mid-2025 has been using a toolkit named KREMLIN to install malicious Chrome and Edge extensions that steal credentials, session tokens, and sensitive data.
Researchers at Elastic Security Labs found that the malicious extensions bypass Chromium’s integrity mechanisms and load in browsers as if they had been approved by the user.
The infection chain starts after the target user opens a JavaScript file disguised as a bank receipt, invoice, payment record, or business document.
Microsoft is investigating reports that the Windows 11 KB5124008 security update is breaking domain trust relationships on some enterprise systems, preventing users from logging in with valid domain credentials.
Administrators report on Reddit and Microsoft’s Q&A forums that affected computers lose their secure channel with Active Directory after the Windows 11 update is installed and devices reboot.
Last week, Microsoft confirmed to BleepingComputer that it is aware of the reports and is investigating.