Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Attackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management Interfaces

Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces.

“Active exploitation has been observed targeting the Palo Alto Networks management interface exposed to the internet,” the network security company said in an update to its advisory.

The vulnerabilities, tracked as CVE-2026–109618 and CVE-2026–109619 (CVSS scores: 9.2), allow attackers to achieve unauthenticated remote code execution on systems running affected versions of PHP. The issues were patched upstream by the PHP Foundation on October 21, 2026, in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35.
Discord to let search engines index public server messages

Discord will allow search engines to index discussions in Discoverable Servers and make them accessible on the web to users outside the platform without an account or invitation.

The goal is to surface useful information to the wider internet community instead of keeping it buried in Discord conversations.

“Discussions in Discoverable Servers will soon be easier to find when you search the web, so you can find the answer you’re looking for and step straight into the conversation on Discord,” the messaging platform explains.

Sony ISP subsidiary data breach exposes 2.5 million customer records

Sony Network Communications has confirmed a data breach that compromised approximately 2.5 million records containing current and former customers’ personal information.

A Sony Group Corporation subsidiary, the company provides telecommunications and technology services, acting as an internet service provider (ISP) in Japan.

The breach occurred on October 19 and was detected four days later, when the company shut down the compromised servers and blocked external communication.

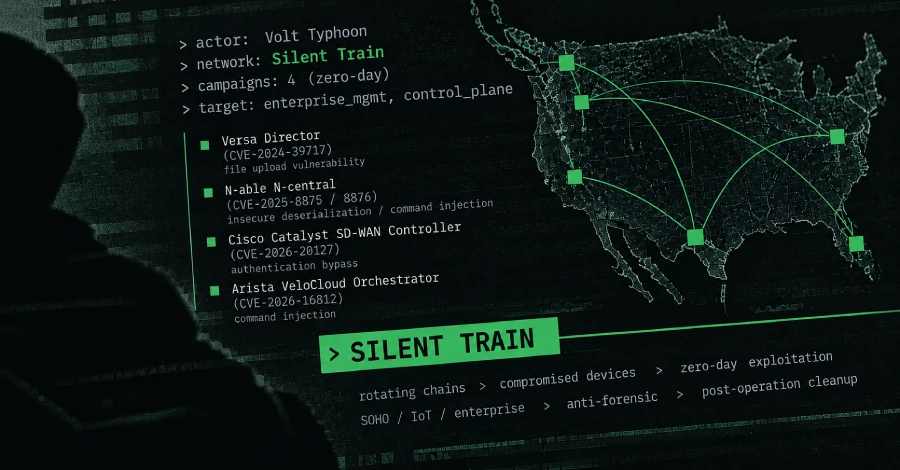
Volt Typhoon hides zero-day attacks using ‘Silent Train’ framework

Chinese state-sponsored hacking group Volt Typhoon has been using a framework that relies on rotating chains of connected devices compromised on demand, including for zero-day attacks targeting high-value systems.

The framework has been dubbed Silent Train because the threat actor uses it against select targets, cleans it up after each operation, and refreshes it continuously.

Researchers at Black Lotus Labs, the threat research division of communications company Lumen, have been tracking Silent Train for three years and confirmed that Volt Typhoon exploited at least four zero-day vulnerabilities in attacks targeting edge and management infrastructure.

Microsoft urges Entra ID admins to migrate users to passkeys

Microsoft again asked Entra ID administrators to migrate users to phishing-resistant methods to avoid sign-in disruptions before it retires SMS and voice authentication in February 2027.

This retirement process applies only to Microsoft Entra ID workforce tenant authentication scenarios and not to Azure AD B2C or Microsoft Entra External ID customer identity scenarios.

Before Microsoft retires SMS and voice authentication, admins should ensure all users in their organizations use a phishing-resistant method, since they will no longer be able to use them to complete multifactor authentication and log in to their accounts.

InfraTrust report warns of exploited flaws in critical network infrastructure

Attackers are actively exploiting vulnerabilities across critical network infrastructure, and PHP flaws known as “PHP2Shell” put the web management interfaces of firewalls, VPNs, application delivery controllers, and other appliances at risk.

The findings come from Eclypsium’s October InfraTrust Pulse, a monthly report tracking security advisories affecting network devices, servers, firmware, chips, and other infrastructure.

Between September 18 and October 14, InfraTrust tracked 133 new security advisories across 18 vendors, covering 2,813 vulnerabilities.