Space Command says satellite tracking must evolve for combat in orbit
As a strategic enabling partner to Edgewing, the consortium will deliver information superiority for the future complex and contested airspace.
A new contract has been awarded to the companies of the GCAP Electronics Evolution (G2E) consortium – the international collaboration between the national defence electronics champions for Italy, Japan and the United Kingdom – to further develop the integrated sensing and communications for the Global Combat Air Programme (GCAP).
The 18-month contract was awarded by Edgewing – the joint venture established by Leonardo S.p. A., Japan Aircraft Industrial Enhancement Co. Ltd. (JAIEC) and BAE Systems plc that is responsible for the design and development of the sixth-generation GCAP fighter aircraft. It follows the signing of a contract between Edgewing and the GCAP Agency, the government entity that manages GCAP on behalf of the three nations.
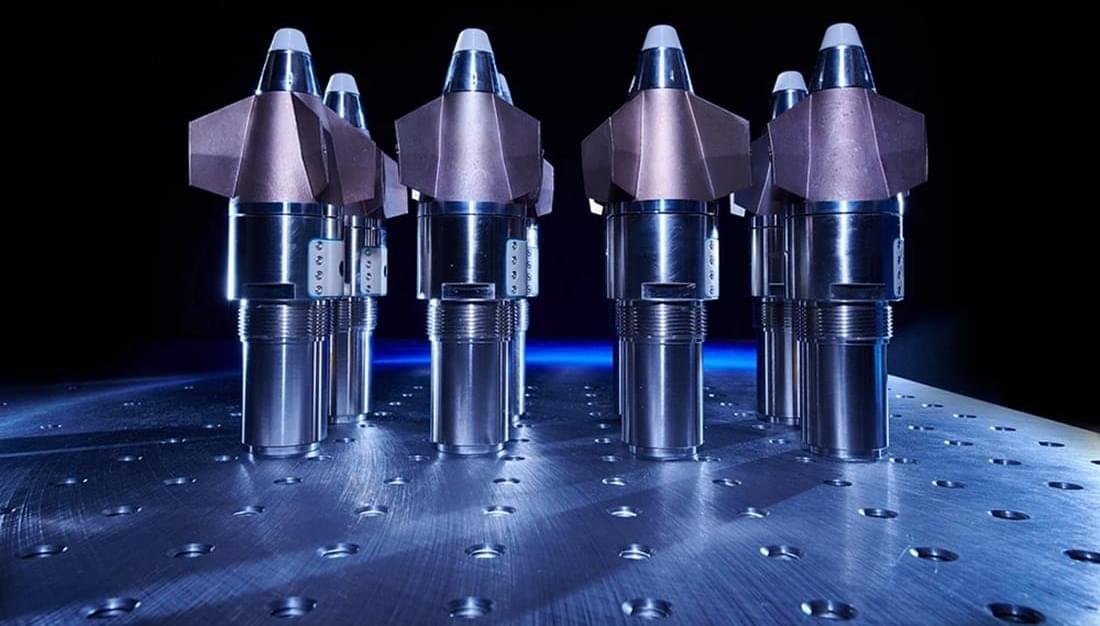
Northrop Grumman Corporation (NYSE: NOC) will produce the PGK E5, a next-generation of the M1156 Precision Guidance Kit (PGK) featuring critical anti-jam capabilities, enabling U.S. Army and allied forces to maintain artillery operations in GPS degraded environments. The PGK E5 transforms existing 155 mm high-explosive projectiles into cost-effective, GPS-guided weapons, delivering precise, reliable indirect fires in current threat environments. Upgraded capabilities of the PGK E5 include advanced anti-jam technology to overcome emerging electronic threats, ensuring accuracy even in contested battlefield environments, while maintaining the same trusted reliability, form factor and user experience as the current PGK. In recent testing conducted in GPS-degraded environments, PGK E5 demonstrated accuracy exceeding both threshold and objective requirements. This precision reduces collateral damage and rounds per engagement, increasing warfighter survivability.
Dave Fine, vice president, armament systems, Northrop Grumman: “Today’s threat environment demands speed and innovation and we’re working closely with the U.S. Army to ensure the PGK E5 keeps maneuver forces ready to win in GPS degraded environments. With decades of proven performance and growing production, PGK continues to deliver reliable, mission-ready technology that warfighters can count on.”
As GPS jamming becomes more prevalent, Northrop Grumman has collaborated with the U.S. Army to innovate and deliver a solution for PGK, all without altering the fit, form or factor to integrate with 155mm artillery. Production is underway at Northrop Grumman’s Plymouth, Minnesota facility with first deliveries expected in early 2028. Compatible with existing 155 mm projectiles and fielded howitzers, the PGK E5 requires minimal retraining or system changes, enabling rapid fielding and deployment.
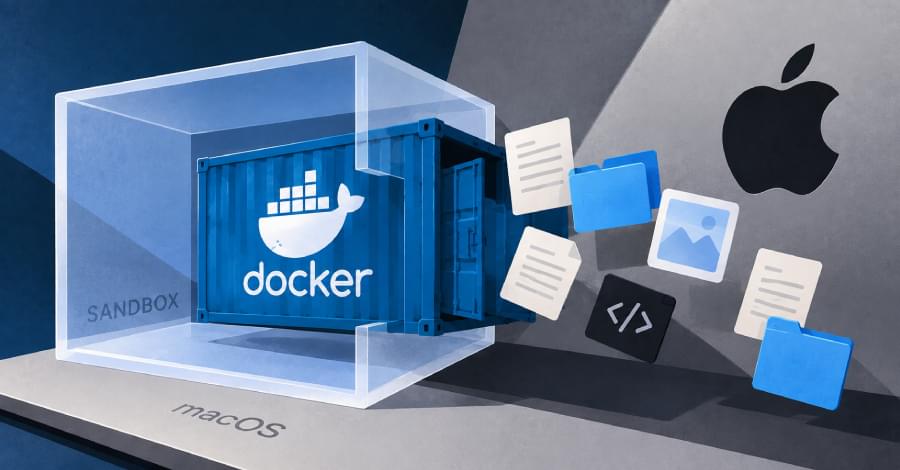
Docker Sandboxes runs each AI coding agent in its own small virtual machine with the project directory shared in. The code that could escape is whatever runs inside that machine, such as a coding agent that has been turned against its user, or anything malicious the agent installs and runs.
Docker has not reported any exploitation. CISA’s added assessment on the CVE record lists exploitation as none, and the flaw is not in CISA’s Known Exploited Vulnerabilities catalog as of the catalog version released on September 16.
The flaw needs malicious code inside the sandbox, and protecting the host from what an agent runs is what the sandbox is for. The agent installs packages and runs commands with sudo inside the virtual machine, and Docker’s isolation documentation says the hypervisor boundary “is the isolation control, not in-VM privilege separation.”
A new Android malware called RatHat has been discovered, targeting users with an AI-powered subsystem that helps operators remotely navigate compromised devices.
Zimperium zLabs researchers analyzed the malware and believe it is linked to threat actors from China after finding it using LLM prompts written in Chinese.
The researchers say the malware is distributed through malvertising, SMS, and phishing sites promoting APK downloads from outside Google Play.
Brevo confirmed that attackers stole a Cloudflare API key and used it to inject malicious ClickFix scripts into its websites and JavaScript files embedded on customer sites to distribute malware.
The customer relationship management and digital marketing company says the attackers used the API key to create a malicious Cloudflare Worker that modified content at the CDN edge for approximately five and a half hours on September 14.
The attack affected pages on brevo.com, sendinblue.com, login/account/my/onboarding.brevo.com, and sibforms.com. The Cloudflare worker also modified the Brevo forms script, Brevo Conversations widget, and the Brevo SDK loader scripts that customers embed on their websites.