Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Aging’s “Zombie Cell” Problem May Have a Solution, Scientists Discover

“Zombie cells” become harder to clear with age, and a new study reveals why the immune system struggles to remove them.

Researchers at Albert Einstein College of Medicine have identified a breakdown in protein recycling that helps explain why senescent cells, often called “zombie cells,” accumulate in aging tissues. In experiments involving older mice, restoring that process reduced senescent-cell buildup, inflammation, and tissue scarring. The findings, published in Nature Aging, suggest a possible way to help the immune system clear these cells more effectively.

Senescent cells remain alive after they stop dividing, but their activity changes. Although they can support tissue repair, their prolonged presence can fuel chronic inflammation and age-related disease. Most of the new experiments involved mice, with human lung samples providing evidence that the biological changes may also occur in people.
Critical 16-Year-Old UEFI Flaw Can Run Code Before Secure Boot on Network-Booting Servers

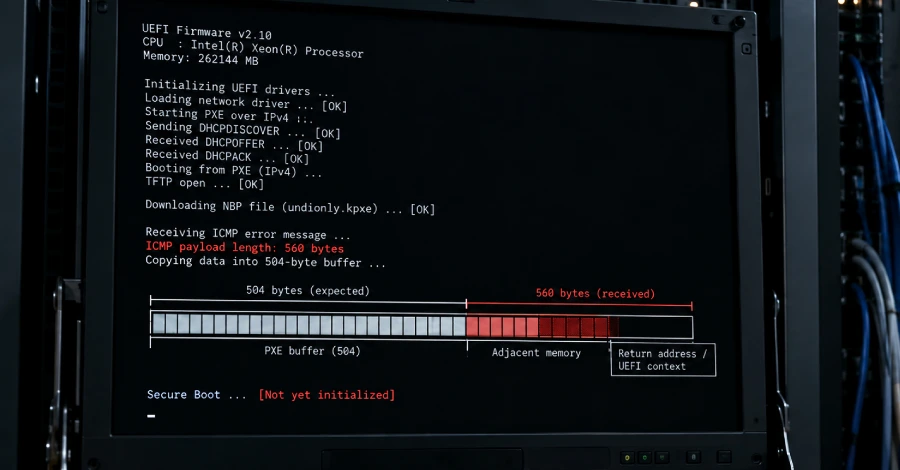
A critical 16-year-old flaw in EDK II, the open-source code that most hardware makers use to build UEFI firmware, can allow an attacker to run code on a machine before its operating system loads, but only while the machine is booting over the network.

UEFI firmware is the software that runs first when a computer is switched on, before the operating system. An attacker who can reach the machine with a crafted network message during such a network boot can hang the boot, or, with work tailored to the exact firmware build, run their own code before Secure Boot and other startup defenses load.

An attacker needs no password and no existing access to the machine, but does need to reach it over the network during the short window when it is booting this way.

Attackers Exploit PHP2Shell Flaws in Internet-Exposed Palo Alto Networks Management Interfaces

Palo Alto Networks on Wednesday warned that threat actors are exploiting the recently patched PHP2Shell vulnerabilities against publicly-accessible management interfaces.

“Active exploitation has been observed targeting the Palo Alto Networks management interface exposed to the internet,” the network security company said in an update to its advisory.

The vulnerabilities, tracked as CVE-2026–109618 and CVE-2026–109619 (CVSS scores: 9.2), allow attackers to achieve unauthenticated remote code execution on systems running affected versions of PHP. The issues were patched upstream by the PHP Foundation on October 21, 2026, in versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35.

Discord to let search engines index public server messages

Discord will allow search engines to index discussions in Discoverable Servers and make them accessible on the web to users outside the platform without an account or invitation.

The goal is to surface useful information to the wider internet community instead of keeping it buried in Discord conversations.

“Discussions in Discoverable Servers will soon be easier to find when you search the web, so you can find the answer you’re looking for and step straight into the conversation on Discord,” the messaging platform explains.

Sony ISP subsidiary data breach exposes 2.5 million customer records

Sony Network Communications has confirmed a data breach that compromised approximately 2.5 million records containing current and former customers’ personal information.

A Sony Group Corporation subsidiary, the company provides telecommunications and technology services, acting as an internet service provider (ISP) in Japan.

The breach occurred on October 19 and was detected four days later, when the company shut down the compromised servers and blocked external communication.

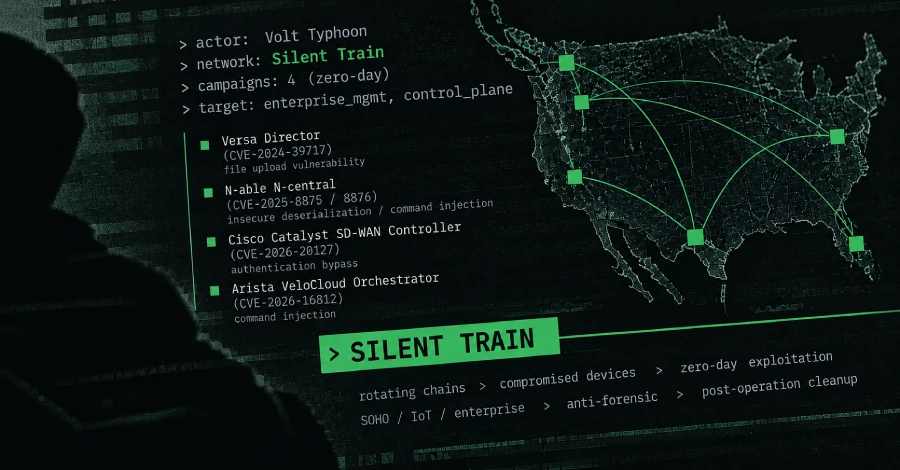
Volt Typhoon hides zero-day attacks using ‘Silent Train’ framework

Chinese state-sponsored hacking group Volt Typhoon has been using a framework that relies on rotating chains of connected devices compromised on demand, including for zero-day attacks targeting high-value systems.

The framework has been dubbed Silent Train because the threat actor uses it against select targets, cleans it up after each operation, and refreshes it continuously.

Researchers at Black Lotus Labs, the threat research division of communications company Lumen, have been tracking Silent Train for three years and confirmed that Volt Typhoon exploited at least four zero-day vulnerabilities in attacks targeting edge and management infrastructure.