A faint hydrogen signal from billions of light-years away could help astronomers build a new 3D map of the Universe.
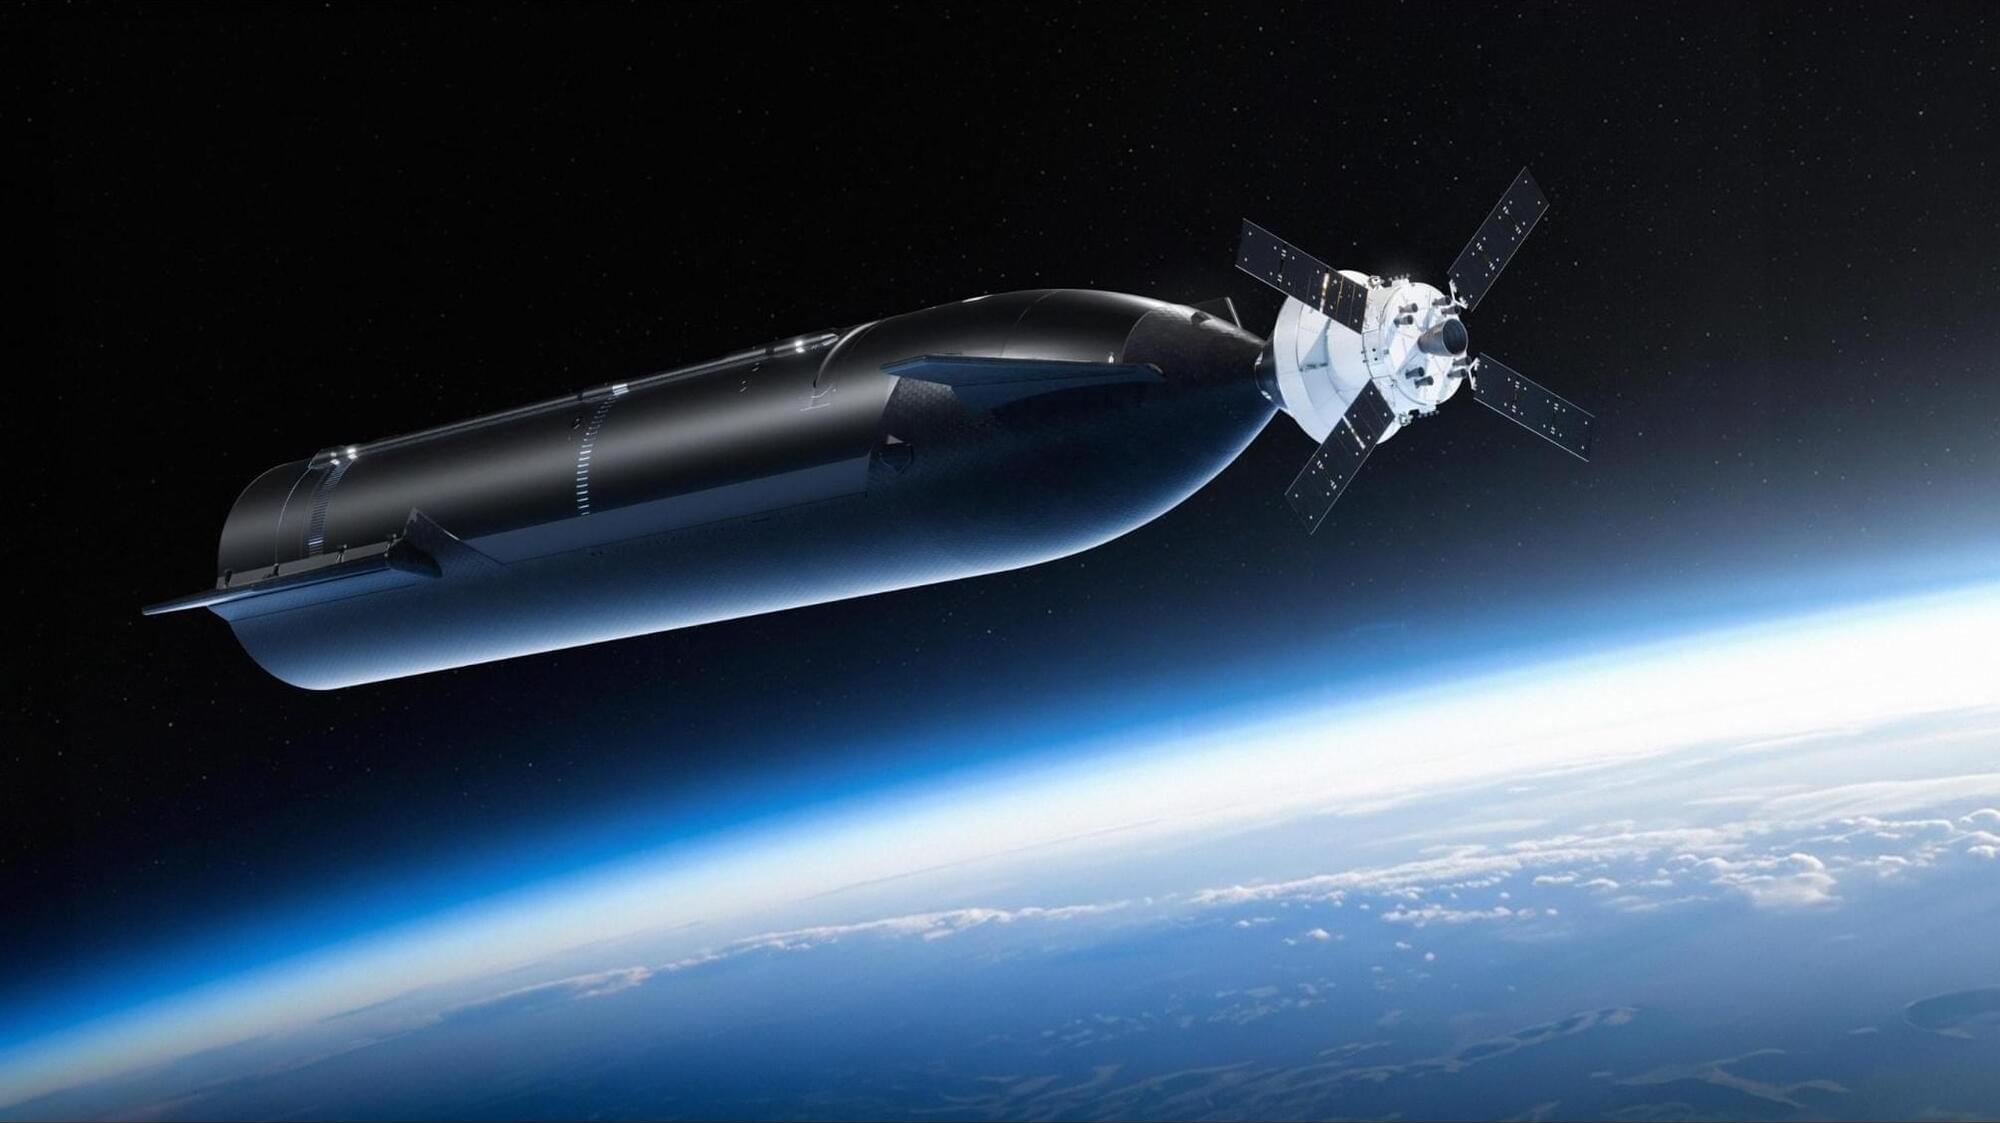
Before astronauts land on the Moon again, NASA will stage an ambitious Artemis III rehearsal involving Orion, SpaceX Starship, Blue Moon, and three major rocket launches.
NASA plans to use Artemis III in 2027 as a major rehearsal for future astronaut landings on the Moon. Before astronauts descend to the lunar surface in 2028, teams on Earth and in space will use the mission to practice rendezvous and docking between Orion and commercial human landing systems. Information gathered during Artemis III, together with data from future uncrewed demonstration missions at the Moon, will help NASA improve astronaut safety and prepare for successful crewed lunar landings.
NASA is working with two U.S. companies to develop the spacecraft that will eventually carry astronauts between lunar orbit and the Moon’s surface. During Artemis III, SpaceX and Blue Origin will each fly test versions, or test articles, of the landers they are developing for future crewed missions. The commercial lander test articles will launch on commercial rockets, while the Artemis III astronauts will travel to low Earth orbit aboard Orion on NASA’s SLS (Space Launch System) rocket.
As a strategic enabling partner to Edgewing, the consortium will deliver information superiority for the future complex and contested airspace.
A new contract has been awarded to the companies of the GCAP Electronics Evolution (G2E) consortium – the international collaboration between the national defence electronics champions for Italy, Japan and the United Kingdom – to further develop the integrated sensing and communications for the Global Combat Air Programme (GCAP).
The 18-month contract was awarded by Edgewing – the joint venture established by Leonardo S.p. A., Japan Aircraft Industrial Enhancement Co. Ltd. (JAIEC) and BAE Systems plc that is responsible for the design and development of the sixth-generation GCAP fighter aircraft. It follows the signing of a contract between Edgewing and the GCAP Agency, the government entity that manages GCAP on behalf of the three nations.
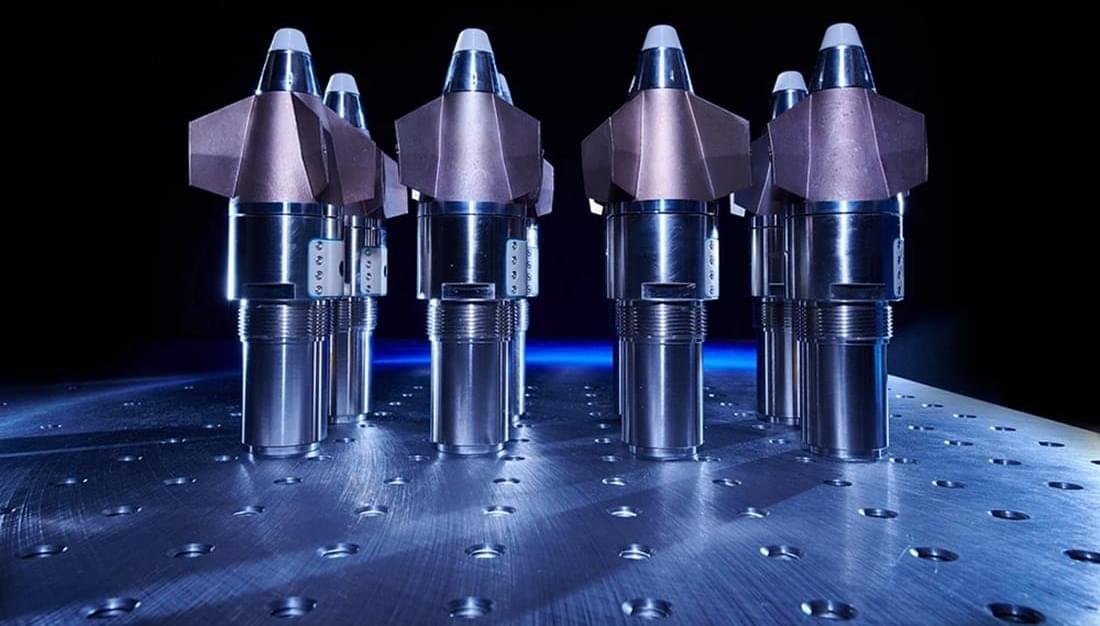
Northrop Grumman Corporation (NYSE: NOC) will produce the PGK E5, a next-generation of the M1156 Precision Guidance Kit (PGK) featuring critical anti-jam capabilities, enabling U.S. Army and allied forces to maintain artillery operations in GPS degraded environments. The PGK E5 transforms existing 155 mm high-explosive projectiles into cost-effective, GPS-guided weapons, delivering precise, reliable indirect fires in current threat environments. Upgraded capabilities of the PGK E5 include advanced anti-jam technology to overcome emerging electronic threats, ensuring accuracy even in contested battlefield environments, while maintaining the same trusted reliability, form factor and user experience as the current PGK. In recent testing conducted in GPS-degraded environments, PGK E5 demonstrated accuracy exceeding both threshold and objective requirements. This precision reduces collateral damage and rounds per engagement, increasing warfighter survivability.
Dave Fine, vice president, armament systems, Northrop Grumman: “Today’s threat environment demands speed and innovation and we’re working closely with the U.S. Army to ensure the PGK E5 keeps maneuver forces ready to win in GPS degraded environments. With decades of proven performance and growing production, PGK continues to deliver reliable, mission-ready technology that warfighters can count on.”
As GPS jamming becomes more prevalent, Northrop Grumman has collaborated with the U.S. Army to innovate and deliver a solution for PGK, all without altering the fit, form or factor to integrate with 155mm artillery. Production is underway at Northrop Grumman’s Plymouth, Minnesota facility with first deliveries expected in early 2028. Compatible with existing 155 mm projectiles and fielded howitzers, the PGK E5 requires minimal retraining or system changes, enabling rapid fielding and deployment.
Docker Sandboxes runs each AI coding agent in its own small virtual machine with the project directory shared in. The code that could escape is whatever runs inside that machine, such as a coding agent that has been turned against its user, or anything malicious the agent installs and runs.
Docker has not reported any exploitation. CISA’s added assessment on the CVE record lists exploitation as none, and the flaw is not in CISA’s Known Exploited Vulnerabilities catalog as of the catalog version released on September 16.
The flaw needs malicious code inside the sandbox, and protecting the host from what an agent runs is what the sandbox is for. The agent installs packages and runs commands with sudo inside the virtual machine, and Docker’s isolation documentation says the hypervisor boundary “is the isolation control, not in-VM privilege separation.”