Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Cobalt Catalyst Delivers 99% Yield Without Expensive Precious Metals

A cobalt catalyst may offer a more sustainable route to valuable chemical transformations when its oxidation state is carefully controlled.

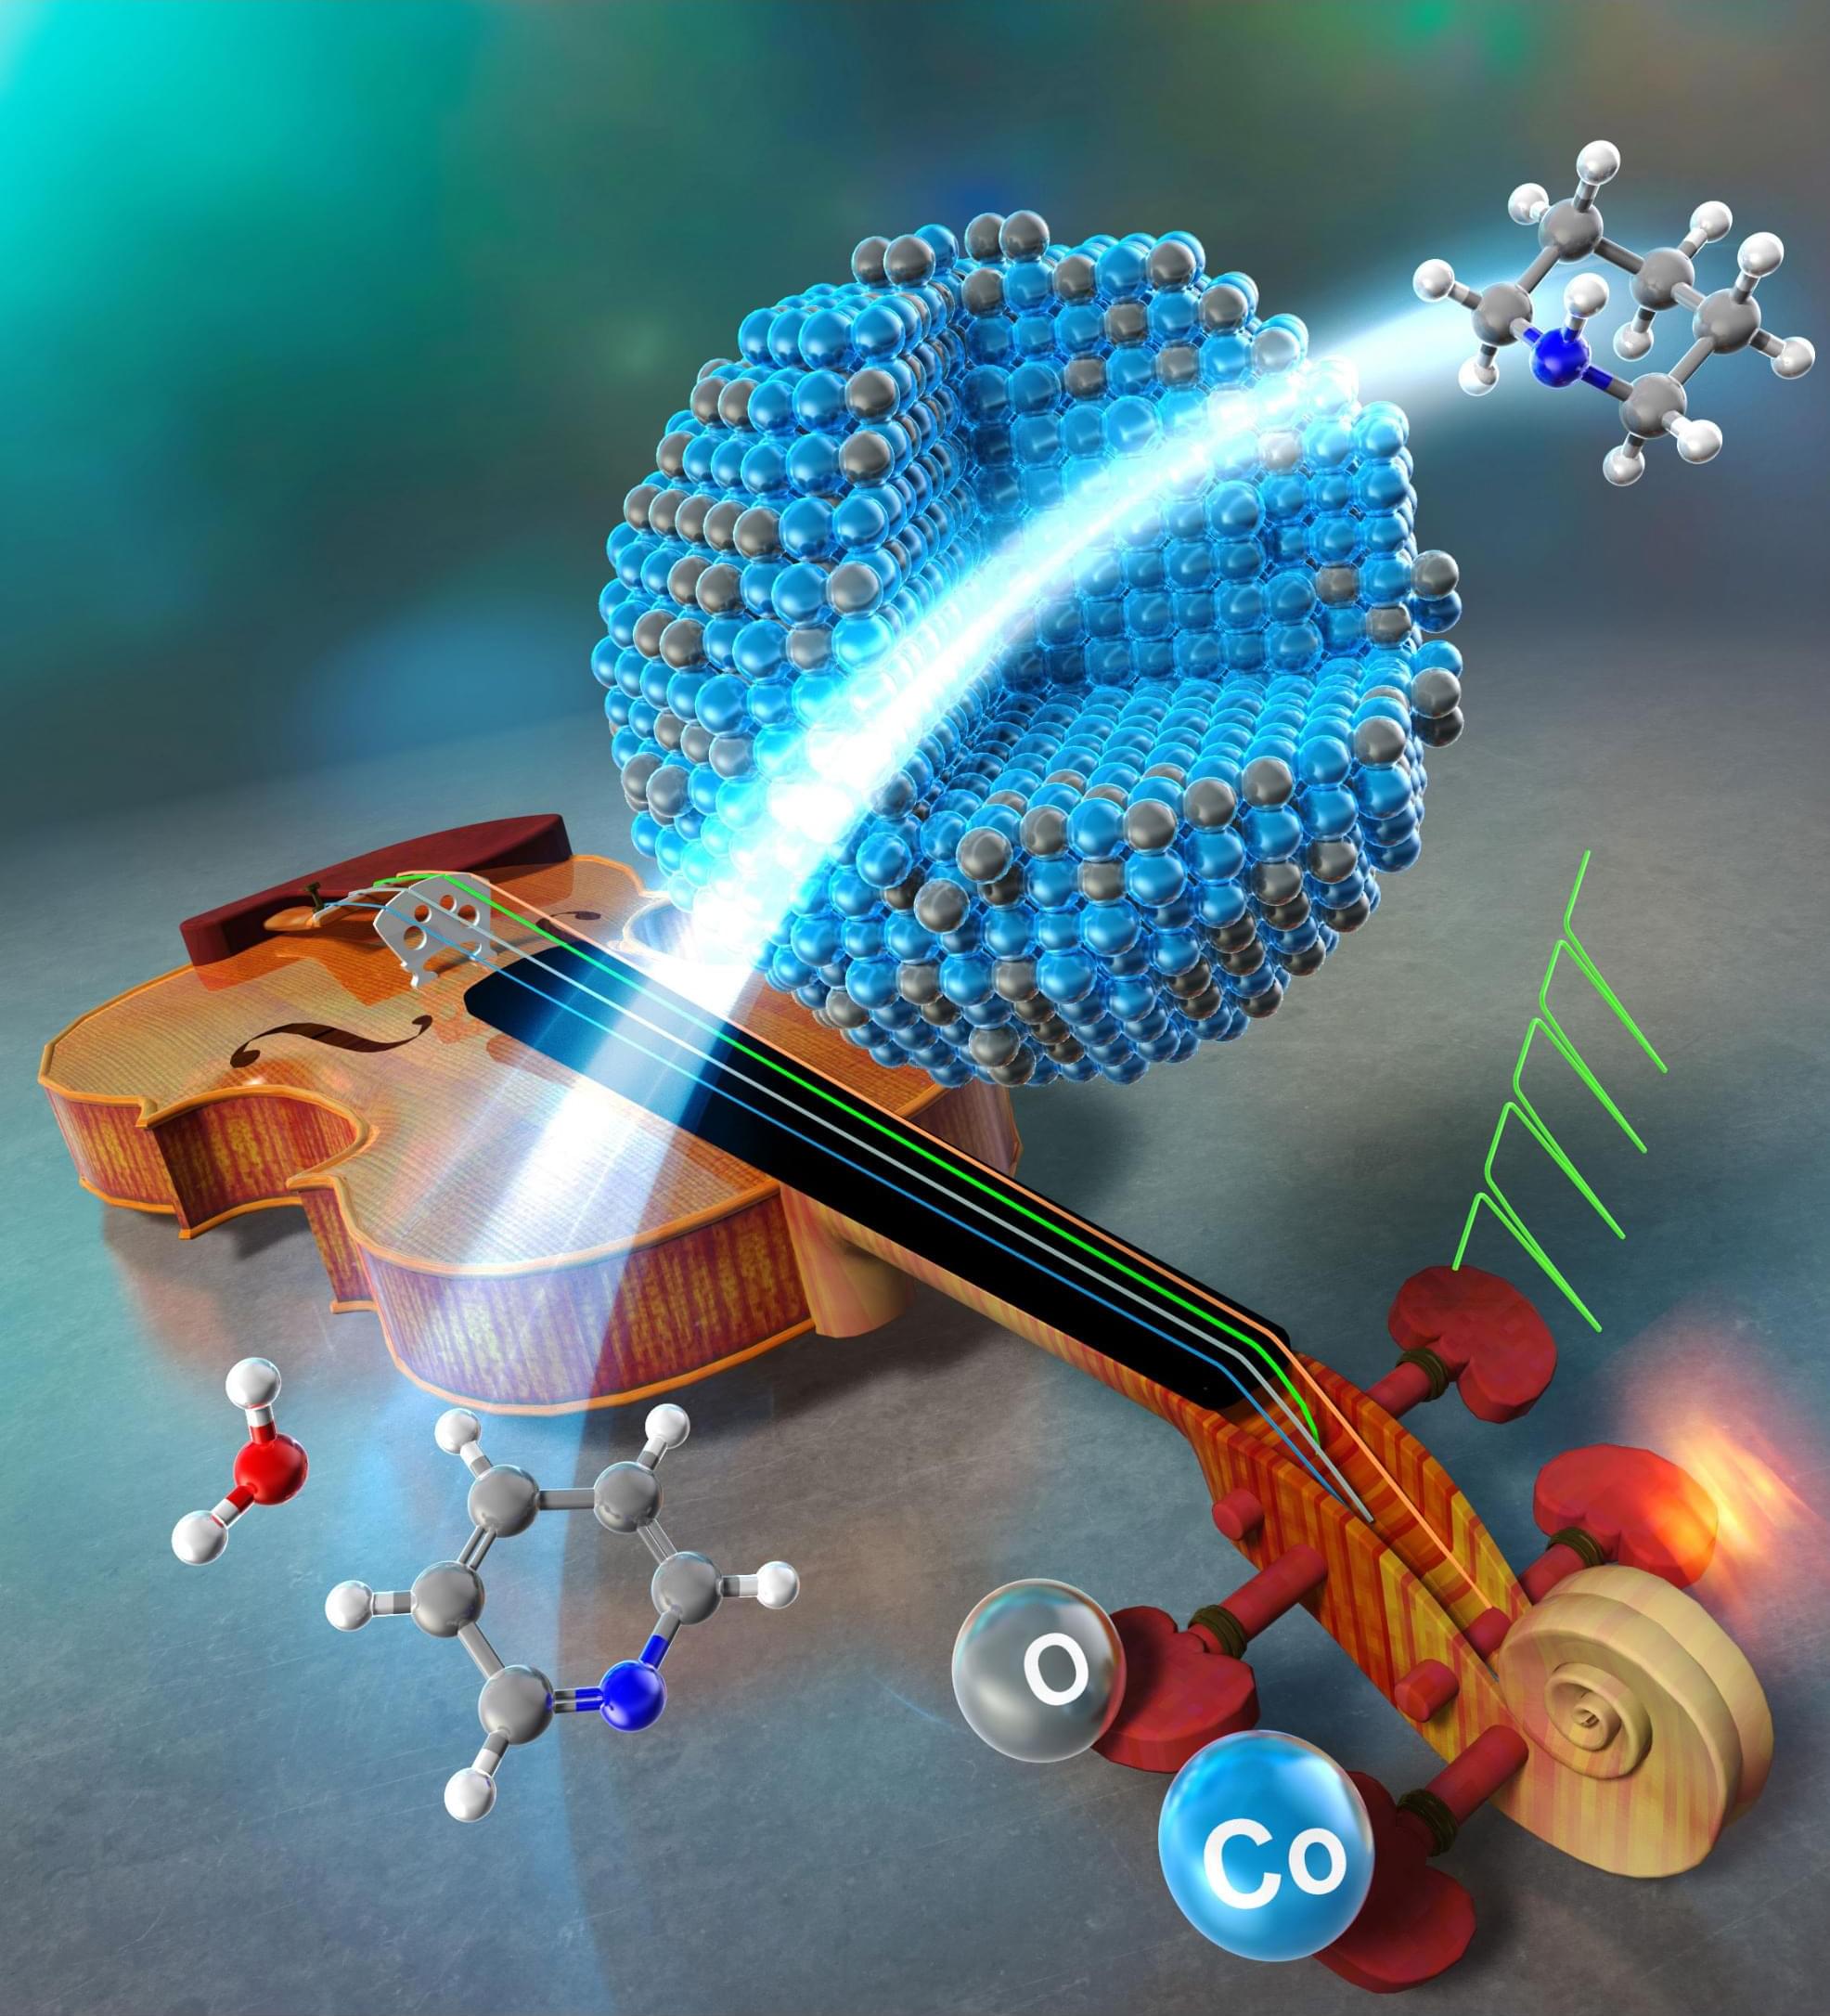
A cobalt catalyst made from an abundant metal converted more than 99% of pyridine into the desired chemical product under ambient electrolysis conditions, according to researchers at Yokohama National University. Its performance depended not just on cobalt itself, but on maintaining the right balance between metallic cobalt and cobalt oxide during the reaction.

The catalyst also selectively hydrogenated several other nitrogen-containing compounds, including quinolines, pyrazines, nitriles and nitroarenes. The approach could help reduce reliance on scarce and expensive platinum group metals.
Scientists Take a Major Step Toward Smaller, Cheaper Free-Electron Lasers

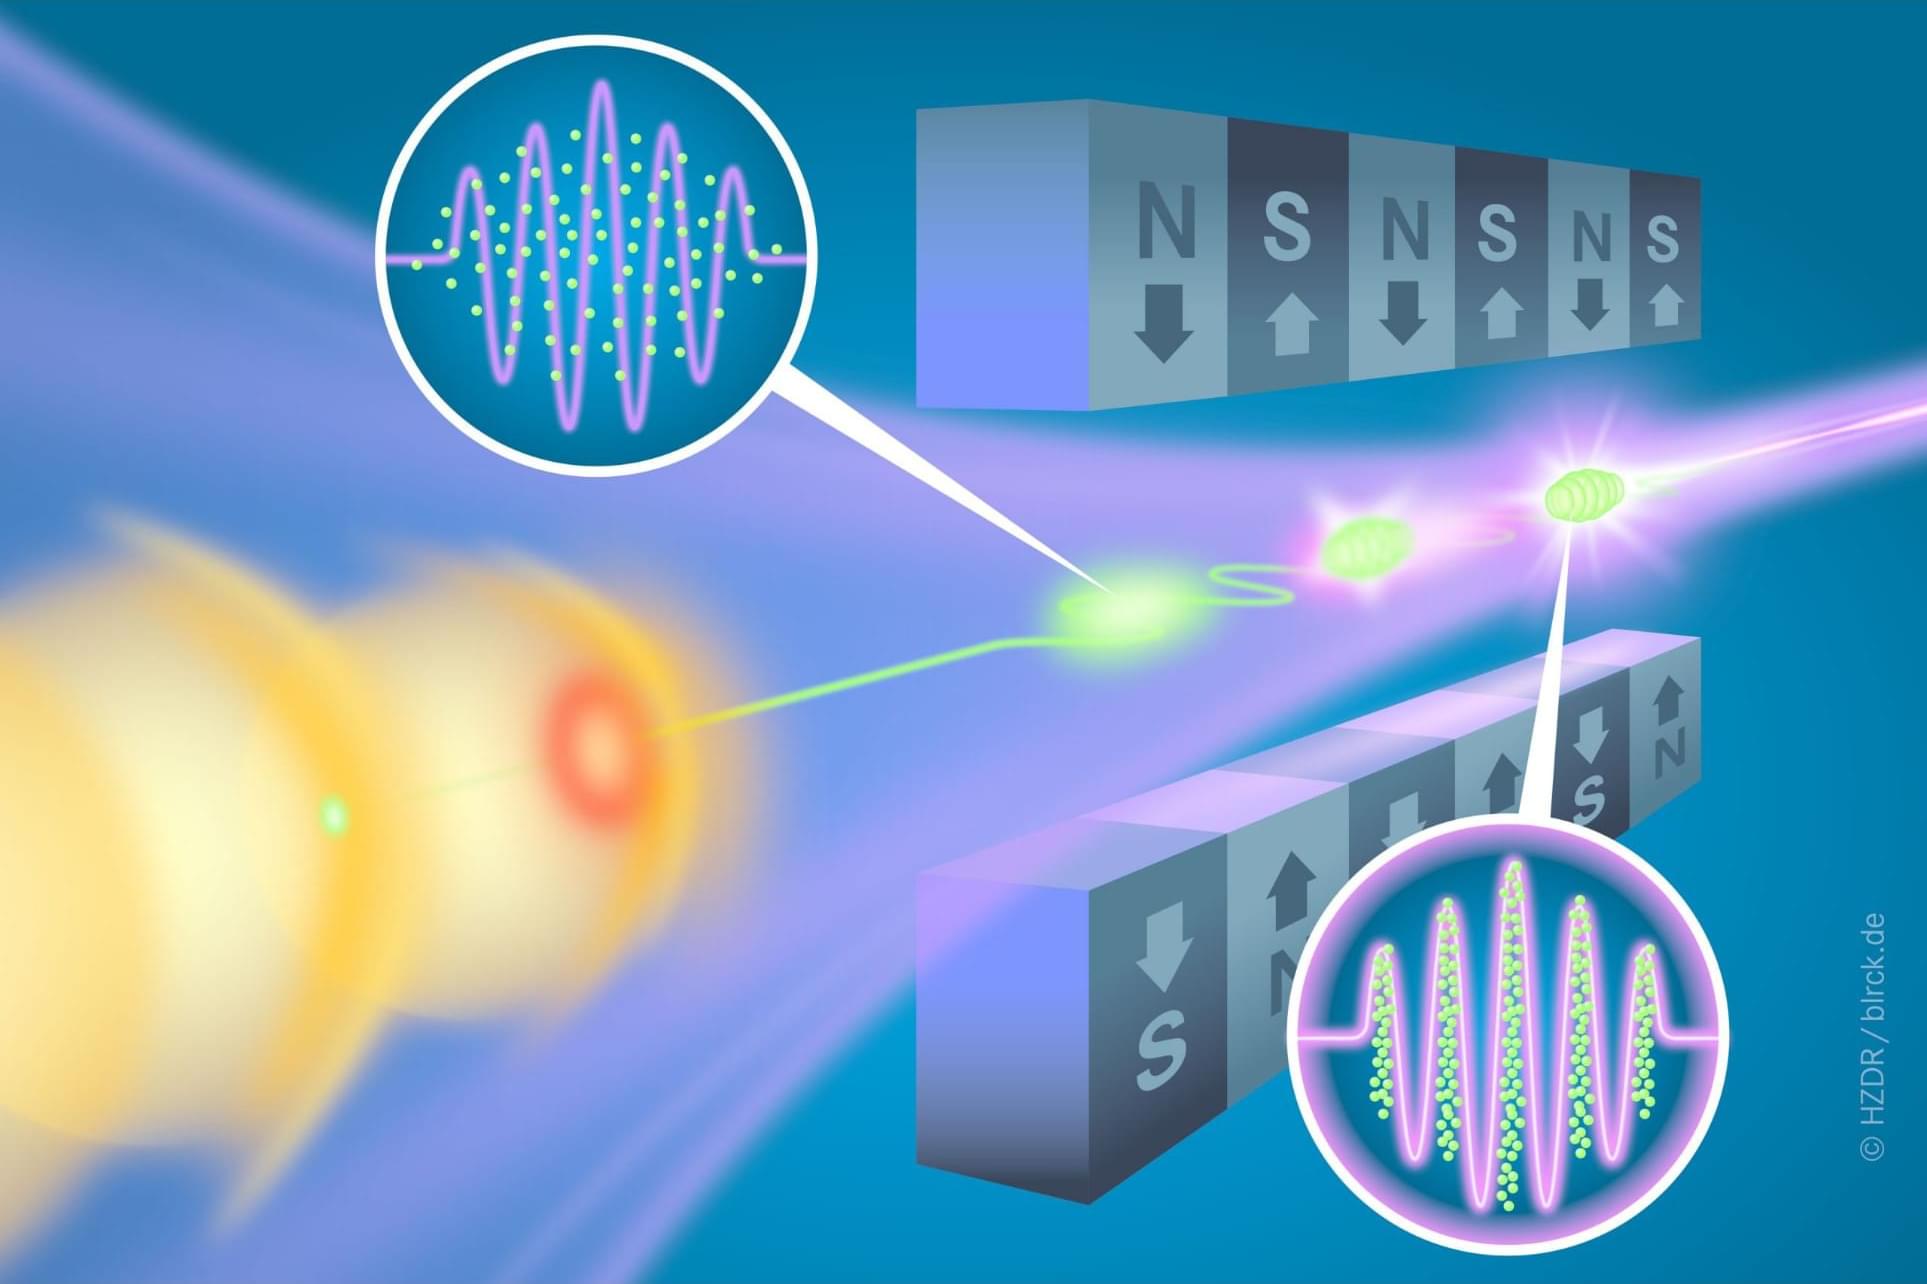
Researchers take a step toward smaller, more affordable free-electron lasers.

Scientists studying atoms, molecules, and new materials use light a little like a photographer uses a camera flash, illuminating their subjects with extremely brief, intense bursts. These flashes come from machines called free-electron lasers, or FELs, and demand for experiments at the large facilities that house them often leaves researchers facing long waits.

Researchers at the Helmholtz-Zentrum Dresden-Rossendorf (HZDR) in Germany and Synchrotron SOLEIL near Paris have now overcome a reliability problem in a compact design that could eventually help meet this demand. Writing in Physical Review Letters, the team reports the first stable, reproducible operation of a laser-plasma FEL in the high-gain regime, a state in which the light it generates undergoes strong amplification.

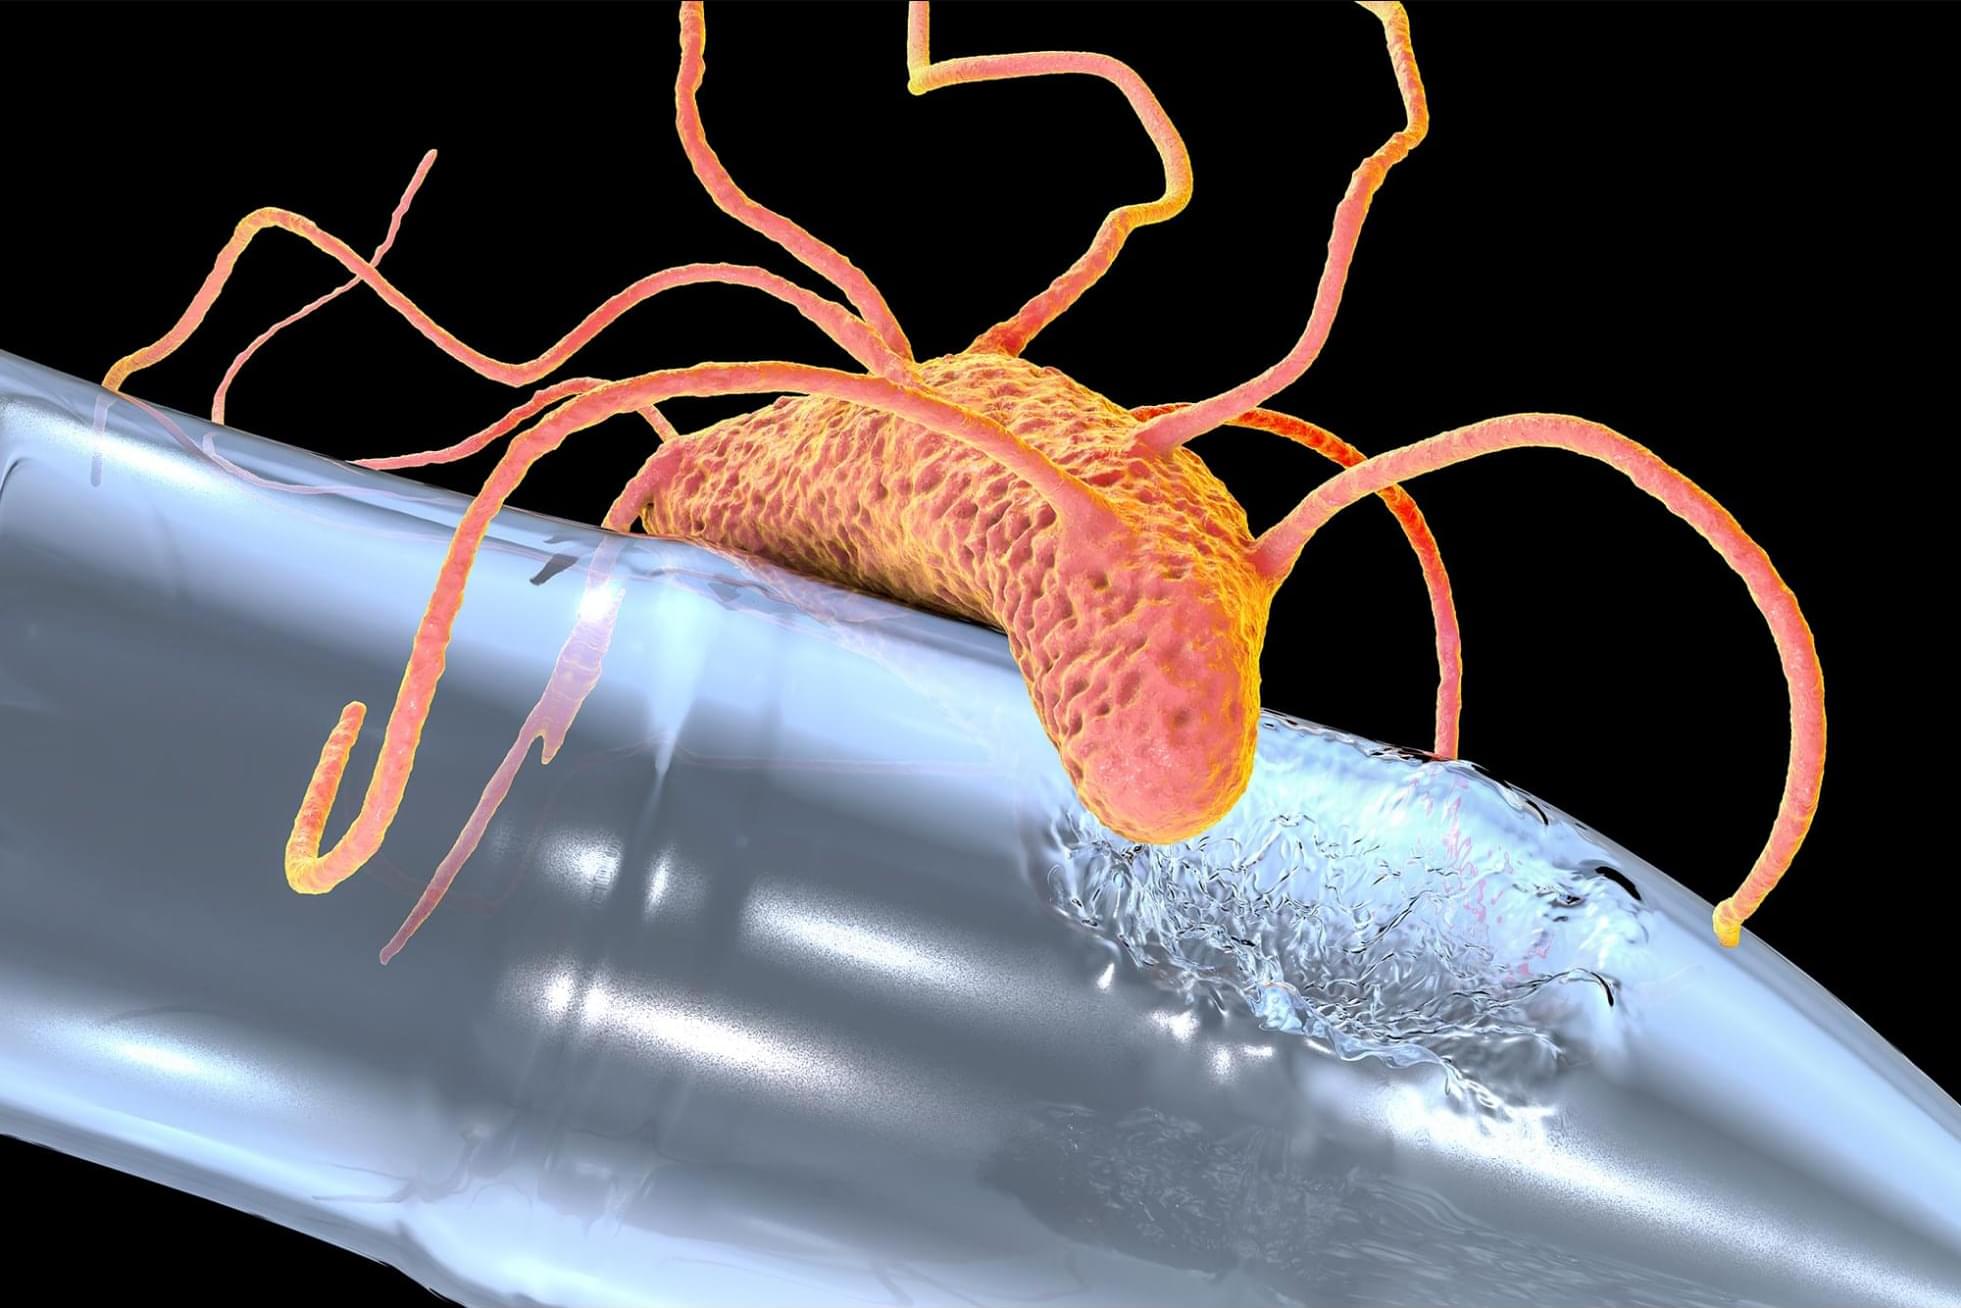
Scientists Discover “Pac-Man Enzyme” That Eats Plastic

A newly identified bacterial enzyme can break down certain polyesters and penicillin, suggesting a possible link between plastic digestion and antibiotic resistance.

For decades, synthetic plastic waste has been collecting in vast oceanic garbage patches and fragmenting into hazardous microplastics and nanoplastics simply because the biological world cannot rapidly digest it.

Microorganisms do colonize these synthetic materials in the environment to form biofilms, creating a unique microbial habitat that researchers call the “plastisphere.” The problem is not a lack of microbial appetite, but rather a profound chemical mismatch between modern synthetic polymers and the enzymes bacteria naturally possess.

Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan

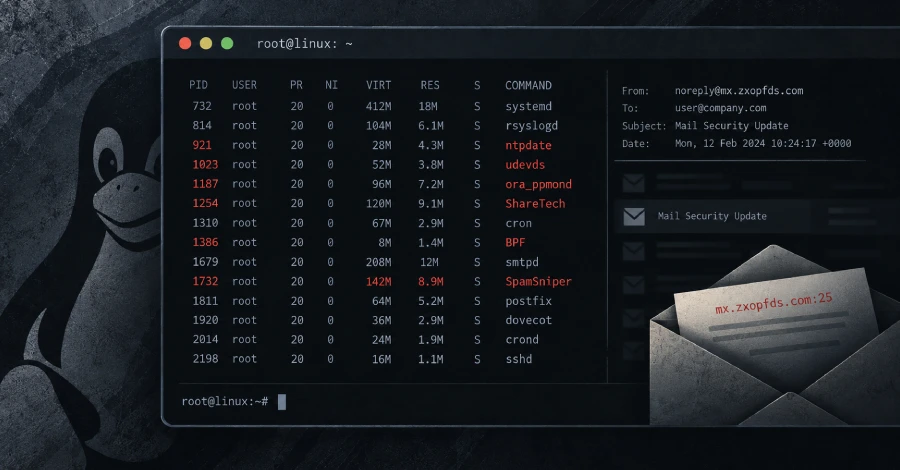
Linux backdoors targeting telecom and network appliances in South Korea and Taiwan have been disguising their traffic as email services and seemingly legitimate processes to blend in and evade detection.

Threat actors are known to name their malicious software after a legitimate operating system component or a process as a defense evasion measure. By borrowing the name of a real binary, it may make it appear less conspicuous among other Windows processes, lend it a false sense of trust, or be overlooked by an analyst during casual inspection.

However, the backdoors examined by Rapid7 have been found to go beyond imitating file names by assuming the identities of email security products like SpamSniper and ShareTech that are widely used in enterprise environments in South Korea and Taiwan.

LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings

A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker’s code as soon as the file is opened, security researchers have shown. There is no warning first, of the kind either program shows before it runs a macro.

The attack works only when the program’s Java support is enabled. So far, it has only been shown as a proof of concept, and there are no reports of its use in real attacks.

LibreOffice has already fixed the flaw, which it tracks as CVE-2026–63277, in updates released on October 5. It recommends that users move to version 26.2.5 or 26.8.0. Versions before those are affected.

Ninja Forms plugin flaw exploited to hack WordPress sites

Hackers are exploiting stored cross-site scripting (XSS) vulnerabilities in two unrelated WordPress plugins, Ninja Forms and WPC Product Bundles for WooCommerce, to install backdoors and create rogue admin accounts.

Both vulnerabilities received a high severity score and require an authenticated session to exploit. They are tracked as CVE-2026–93836, affecting WPC Product Bundles for WooCommerce versions 8.6.6 and older, and CVE-2026–94504, affecting Ninja Forms versions 3.15.3 and older.

The Ninja Forms plugin for WordPress is installed on more than 500,000 sites and allows creating custom forms without writing code.

/* */