Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Attacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 Repositories

Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories.

Before the repository spread, the assistant recommended software that the attacker had poisoned, and the recommendation was accepted. The worm stole repository secrets and source code for the company’s products.

The case appears in Mandiant’s September 2026 report. The public case study does not say when the intrusion happened or how the attacker took over the active coding-assistant session.

Google Patches Pixel Modem Flaw Amid Signs of Limited Targeted Exploitation

Back in June 2026, Google shipped patches for a high-severity flaw in Android’s Framework component (CVE-2025–48595, CVSS score: 8.4) that it said came under active exploitation.

Update

The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on September 16, 2026, added CVE-2026–58704 to its Known Exploited Vulnerabilities (KEV) catalog, requiring Federal Civilian Executive Branch (FCEB) agencies to apply the fixes by September 19, 2026.

Malware bypasses browser checks to force install Chrome, Edge extensions

A banking malware operation active since mid-2025 has been using a toolkit named KREMLIN to install malicious Chrome and Edge extensions that steal credentials, session tokens, and sensitive data.

Researchers at Elastic Security Labs found that the malicious extensions bypass Chromium’s integrity mechanisms and load in browsers as if they had been approved by the user.

The infection chain starts after the target user opens a JavaScript file disguised as a bank receipt, invoice, payment record, or business document.

Windows 11 KB5124008 update breaks domain trust for some users

Microsoft is investigating reports that the Windows 11 KB5124008 security update is breaking domain trust relationships on some enterprise systems, preventing users from logging in with valid domain credentials.

Administrators report on Reddit and Microsoft’s Q&A forums that affected computers lose their secure channel with Active Directory after the Windows 11 update is installed and devices reboot.

Last week, Microsoft confirmed to BleepingComputer that it is aware of the reports and is investigating.

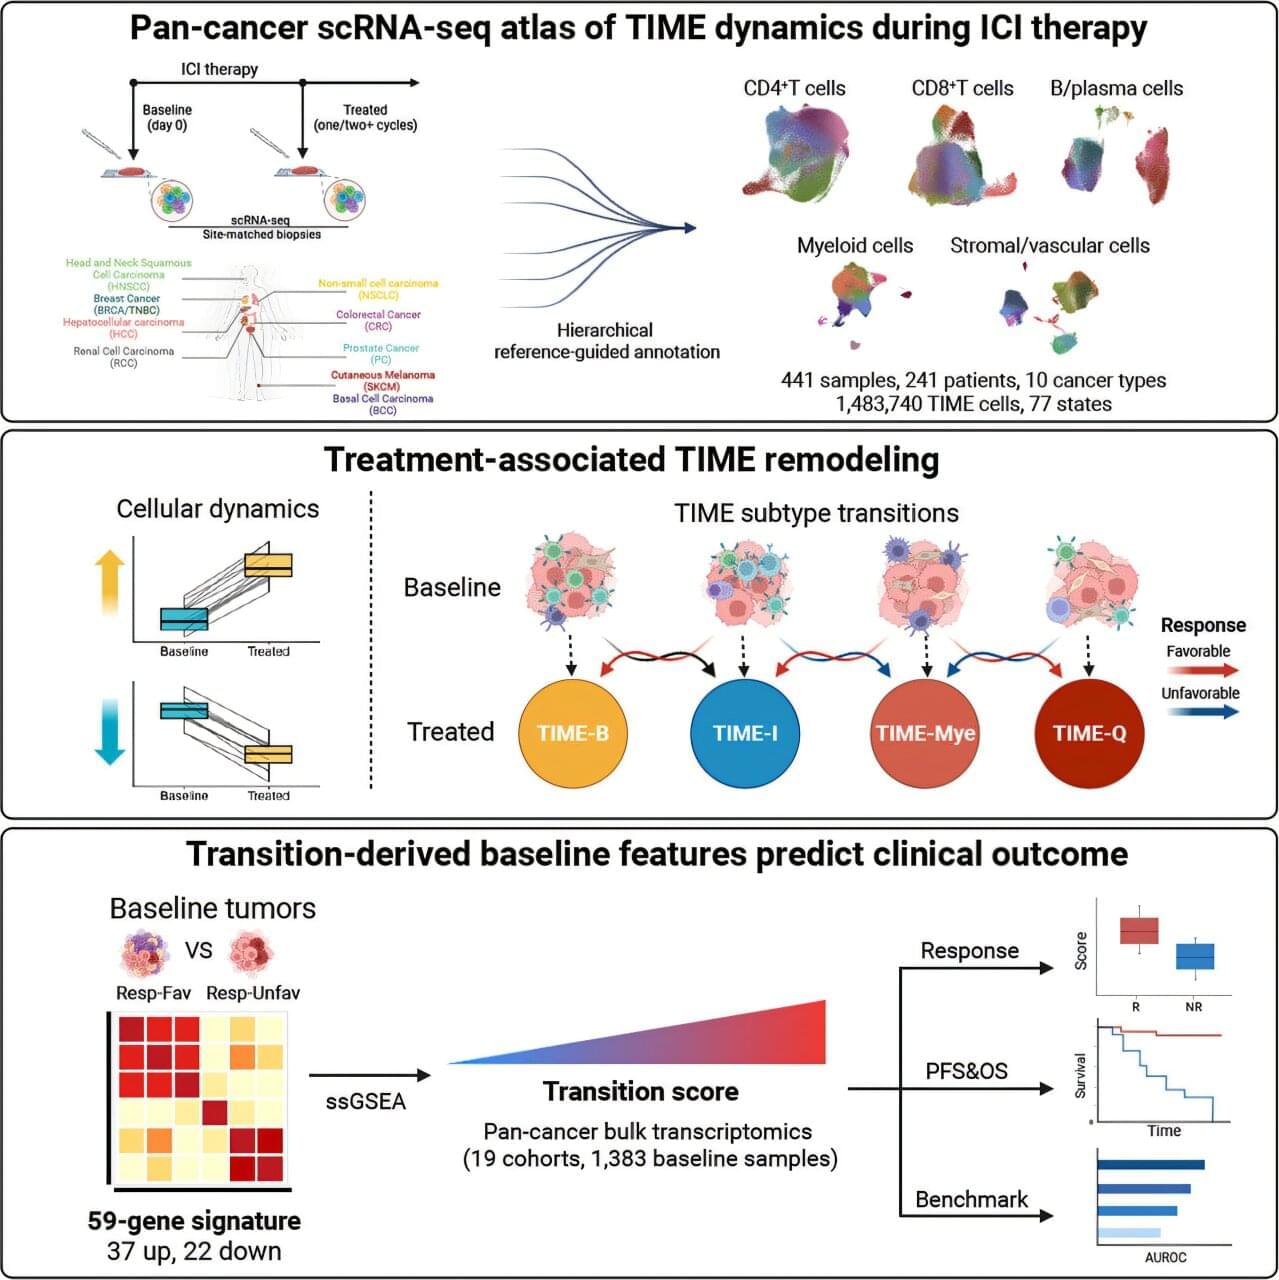
Early changes in the tumor environment may explain why immunotherapy works for some patients but not others

Two patients receive the same immunotherapy for the same cancer. In one, the tumor retreats and stays gone for years. In the other, the treatment does nothing. Oncologists still have no reliable way to tell these patients apart before therapy begins. Why does immunotherapy succeed for some and fail for others?

A new study led by Professor Dvir Aran of the Technion Faculty of Biology and the Henry and Marilyn Taub Faculty of Computer Science, together with first author Dr. Zhongyang Lin and collaborators including Professor Jürgen C. Becker of the German Cancer Consortium (DKTK), offers a new way to think about that question. Its central message: The answer may depend less on how a tumor looks before treatment begins than on how it changes during the first weeks of therapy. The findings are published in the journal Cancer Cell.

At the center of the study is the tumor microenvironment, the complex ecosystem of immune cells, blood vessels and structural cells that surround and interact with the tumor. This environment can either support the immune system’s attack or suppress it, and researchers have long suspected it plays a major role in whether immunotherapy succeeds or fails.

Software rapidly tracks viral variants with high accuracy to aid outbreak responses

It was mid-2020, and Patrick Varilly, a software engineer and data scientist, was stuck at home, eager to help the world navigate the ongoing COVID-19 pandemic. He reconnected with Pardis Sabeti, a core institute member of the Broad Institute who was at the forefront of analyzing how the SARS-CoV-2 virus was spreading, and with Ben Fry, her longstanding collaborator and principal at Fathom Information Design, a software firm known for tackling complex data problems. Varilly had worked closely with Sabeti and Fry at MIT more than 20 years earlier.

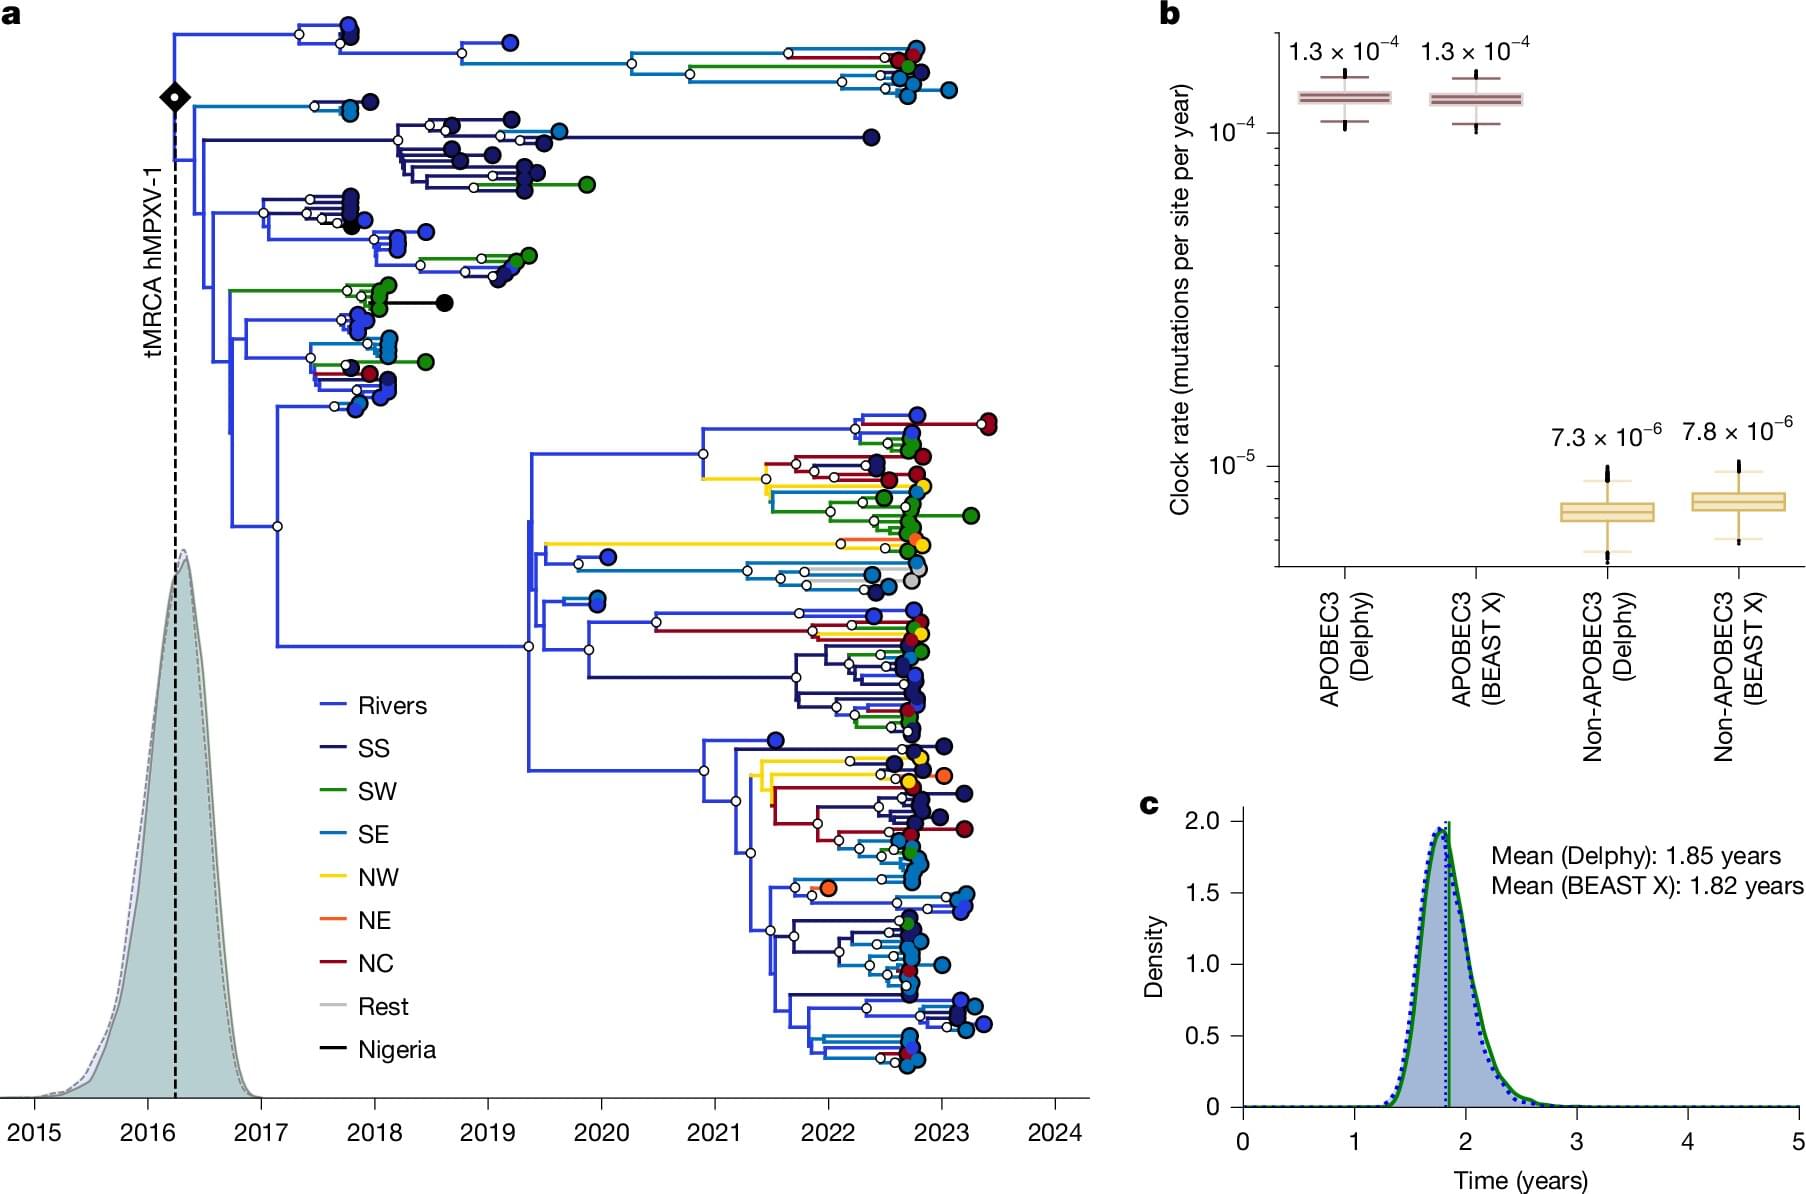
At the time, Sabeti, Fry and their teams were studying thousands of SARS-CoV-2 genomes from COVID-19 patients to reconstruct the path of viral transmission and identify which viral variants were emerging. Normally, retracing that path—by mapping how different variants are genetically related to each other in what’s called a phylogenetic tree—takes a lot of time and computing power.

Varilly, Sabeti and Fry saw an opportunity to accelerate the process while making data more accessible and easier to interpret. The result is Delphy, a new platform for rapid, interactive phylogenetic analysis. In a paper published in Nature, the researchers report how they rebuilt state-of-the-art phylogenetic tree models to make them faster, more efficient and scalable while maintaining the models’ accuracy. Because Delphy runs entirely within a web browser, anyone with a laptop can perform these analyses without specialized training, software or computing infrastructure.
/* */