Two CVSS 9.0 flaws in Linux KSMBD could enable remote code execution; one needs no authentication, and neither has a mainline fix.
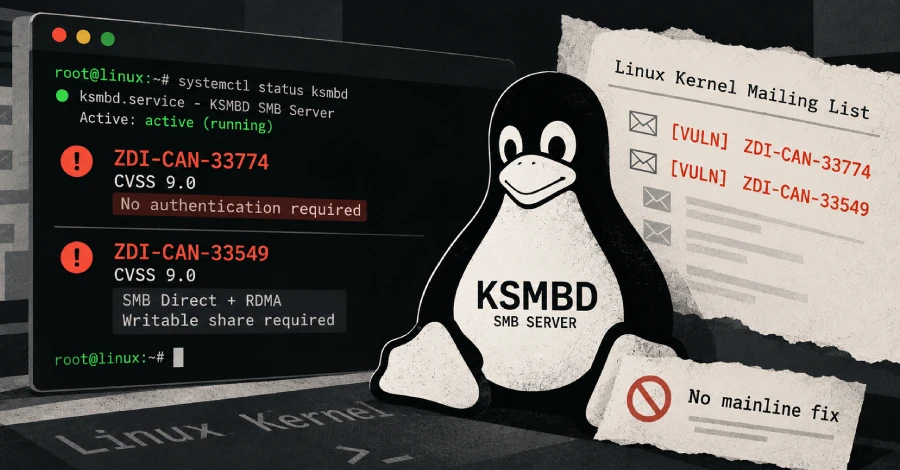
Two CVSS 9.0 flaws in Linux KSMBD could enable remote code execution; one needs no authentication, and neither has a mainline fix.
Social media giant Meta was ordered to pay 25 billion in penalties by a New Mexico court on Wednesday as part of a data privacy lawsuit that sprang from the company’s Cambridge Analytica data scandal, which came to light in 2018.
According to multiple reports from the Associated Press, the New York Times, Reuters, and the Wall Street Journal, state District Court Judge Francis J. Mathew called out Meta and Facebook for making misleading statements about the privacy of consumers in the state.
“Facebook promised users that they (the users) controlled their data,” Mathew wrote in his ruling. “This was false.”
INTERPOL’s Operation Serengeti III disrupted 10,909 malicious networks, arrested 1,462 suspects, and recovered over $105 million.
Japanese gaming giant Capcom has confirmed that hackers breached its membership service, CAPCOM ID, exposing more than 11.7 million customer email addresses and associated information.
Apart from emails, exposed data includes account creation date, last login timestamp, number of logins, and the IP address used at the last login.
Capcom found that for a small subset of 43 accounts, dates of birth, gender, nicknames, and countries were also exposed.
Arista Networks released security updates to patch an actively exploited zero-day vulnerability affecting VeloCloud Orchestrator (VCO) On-Prem deployments.
VCO is a web-based management portal that helps administrators configure, monitor, and manage VeloCloud SD-WANs (Software-Defined Wide Area Networks) and associated edge devices.
Tracked as CVE-2026–114625, this critical-severity flaw can allow attackers with basic privileges, access to the VCO web interface, and a valid authenticated session to escalate privileges through low-complexity SQL injection attacks that don’t require user interaction.
Hackers compromised the LiteLLM project’s PyPI package and published malicious Docker images with a payload that steals credentials, secrets, and environment variables.
The supply-chain attack affected all PyPI wheels (.whl installation packages) for LiteLLM version 1.107.0, impacting Windows, Linux, and macOS systems.
LiteLLM is an open-source Python SDK and AI gateway that enables applications to access AI models from different providers through a common API.
Attackers can steal credentials and begin exfiltrating data within minutes, often before security teams can respond. Exaforce examines real-world attacks involving stolen GitHub tokens, malicious AI installers, and MFA phishing, explaining why faster detection and automated containment are critical.
Security researchers at Amazon Threat Intelligence say attackers began targeting the PHP2Shell flaws four days before security patches were released on Wednesday.
Tracked as CVE-2026–109618 and CVE-2026–109619, the two critical vulnerabilities let attackers gain remote code execution (RCE) on vulnerable systems. The PHP security team patched them on October 21 after urging admins one day earlier to prepare to install the updates as soon as they became available.
PHP core developer Gina Peter Banyard warned before disclosure that applying the official security patches is the only permanent defense, while the UK National Cyber Security Centre (NCSC) asked UK organizations to immediately update PHP servers or take them offline until they can be patched.
GitLab has released security patches for a maximum-severity Regular Expression Compiler flaw that can let remote attackers run arbitrary code on vulnerable servers.
This security issue is tracked as CVE-2026–110264 and was reported by a security researcher using the ‘joaxcar’ handle through GitLab’s HackerOne bug bounty program.
CVE-2026–110264 stems from an integer overflow weakness in GitLab’s Regular Expression Compiler, a background engine that parses and validates regular expressions in configuration files.
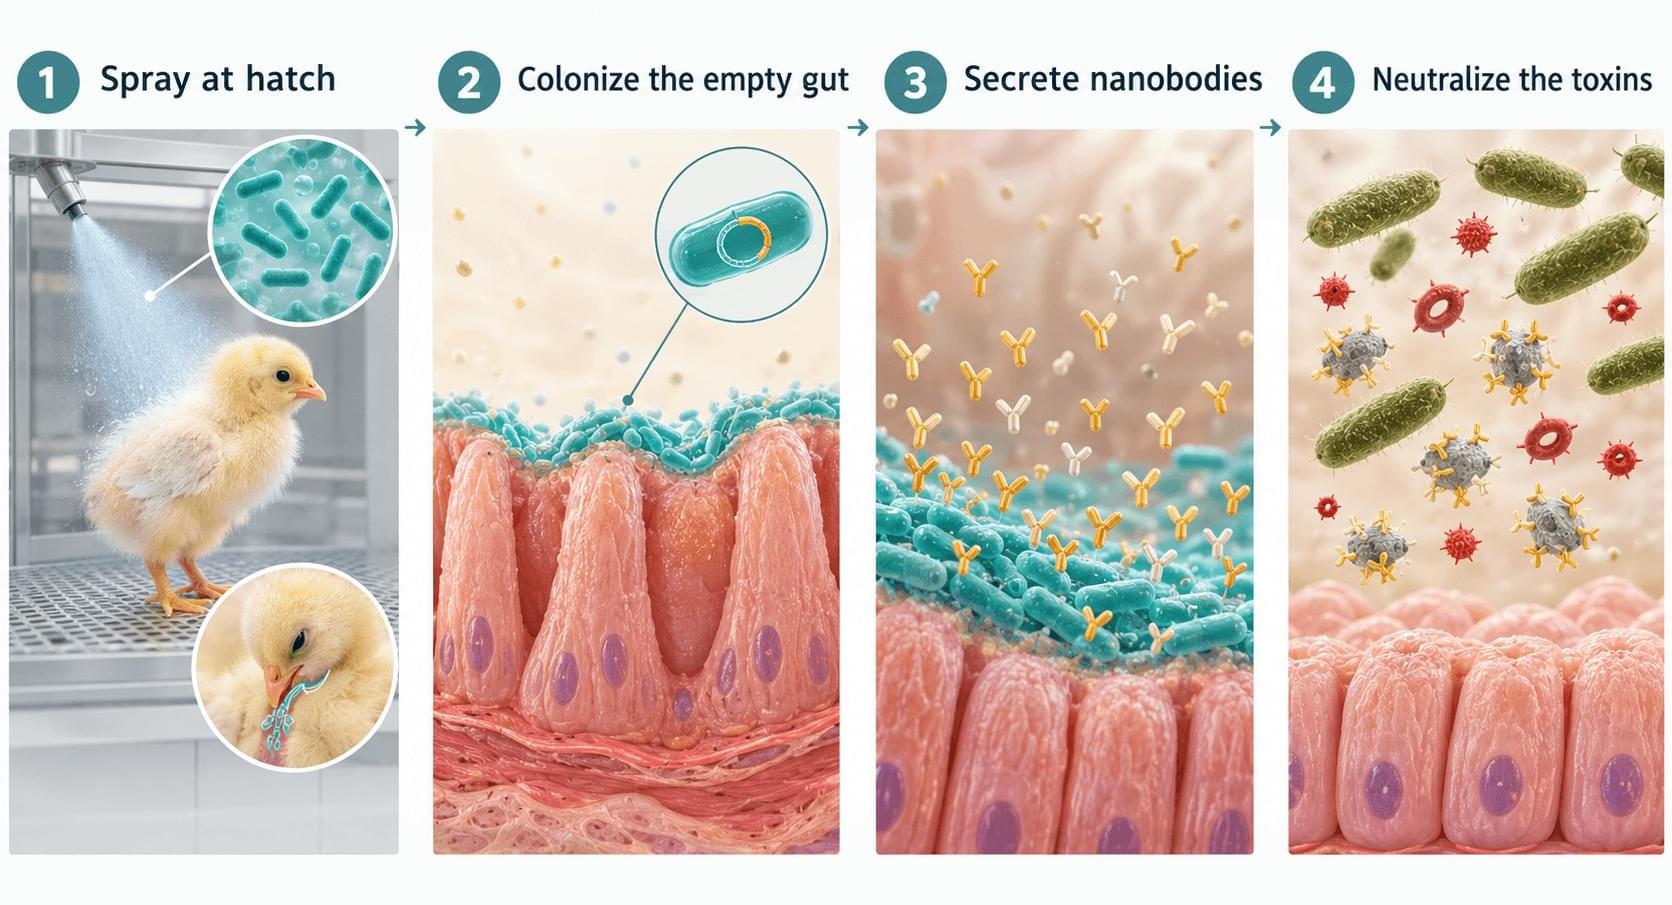
An interesting story of a company which has engineered bacteria to make nanobodies and prevent necrotic enteritis in poultry. They are also expanding into other animal health areas like canine medicine!
BiomEdit’s engineered probiotic is now in more than 35 million broilers. The pitch is not fewer dead chickens. It is feed conversion, which is where the $6 billion actually hides.