Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Linux Kernel TCP Flaw With 9.8 CVSS Score Affects Ubuntu, Red Hat and Other Distributions

Anthropic said on October 27 that its AI model wrote an exploit that uses the flaw to let a remote attacker with no credentials run commands as root on Linux servers with a multipath TCP listener.

As of October 29, Ubuntu and RHEL have not released a fixed kernel. Red Hat, Amazon, Oracle, and SUSE score the flaw between 5.9 and 8.1, lower than the kernel team’s 9.8.

The flaw is a race condition in the code that sets up new IPv4 TCP connections. It can make the kernel read memory it has already freed, a bug type known as a use-after-free.
26,400 Valid Cloud and AI Credentials Found Exposed in Public Gitee Repositories

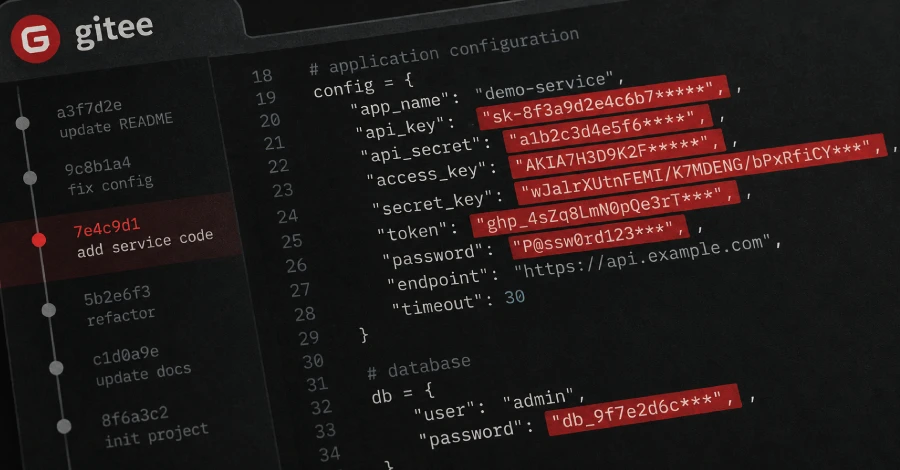
26,400 credentials that developers left in public code on Gitee, a Chinese code-hosting service, still worked when a researcher tested them. Anyone who copied one from that code could have used it.

Independent researcher Ben Zimmermann found them by scanning 7.25 million public Gitee repositories and reported the results on October 28. Most were keys for cloud and AI services, led by 9,473 Alibaba Cloud AccessKey pairs.

Zimmermann sent the vendors with the most exposed keys a list of their credentials, but he did not contact the developers who leaked them. When he published, he had not confirmed that any of the reported credentials had been revoked. So anyone who has pushed a key to a public Gitee repository cannot assume it has been revoked.

Cisco Patches Actively Exploited ASA and FTD VPN Flaw That Can Crash Firewalls

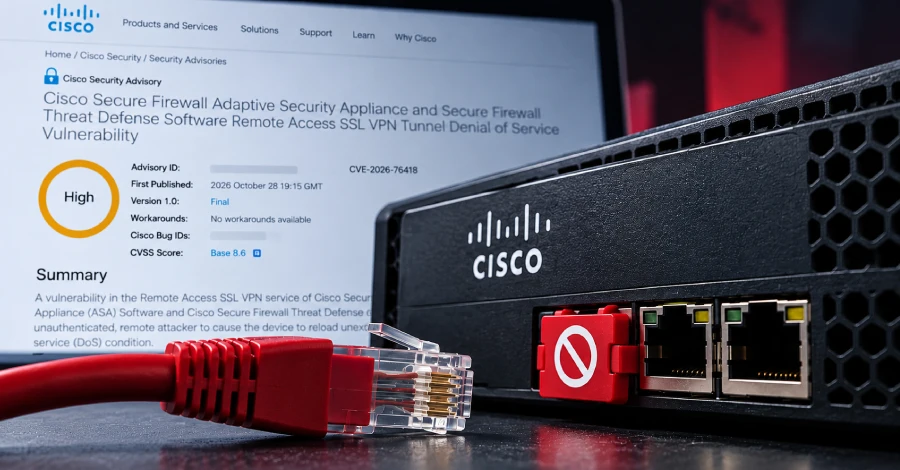
The vulnerability, tracked as CVE-2026–76418, is rated 8.6 on the CVSS scoring system. Successful exploitation could allow an unauthenticated, remote attacker to cause the device to reload unexpectedly, resulting in a denial-of-service (DoS) condition.

According to Cisco, the issue is rooted in the Remote Access SSL VPN service of ASA and FTD software.

“This vulnerability is due to logic errors when secondary authentication is configured on a tunnel group,” it said in a Wednesday advisory. “An attacker could exploit this vulnerability by sending a crafted request when connecting to the SSL remote access VPN. A successful exploit could allow the attacker to cause the affected device to reload, resulting in a DoS condition.”

Chrome extensions with 13.4 million installs caught hijacking searches

A massive search-hijacking campaign involving 319 Chrome extensions with a combined 13.4 million reported installations redirected users’ searches through tracking servers to generate advertising revenue from Bing and Yahoo.

A new report by Socket’s John Tuckner expands on the researcher’s April 2025 discovery of 57 Chrome extensions with 6 million users, adding 264 newly identified add-ons with another 8.7 million users.

“These extensions were created by a handful of organized operators all working from the same idea: quietly take over the browser’s default search engine, route every query through a suspicious proxy server, and collect partner referral payments from Yahoo or Bing under a syndication partner ID,” explained Tuckner.

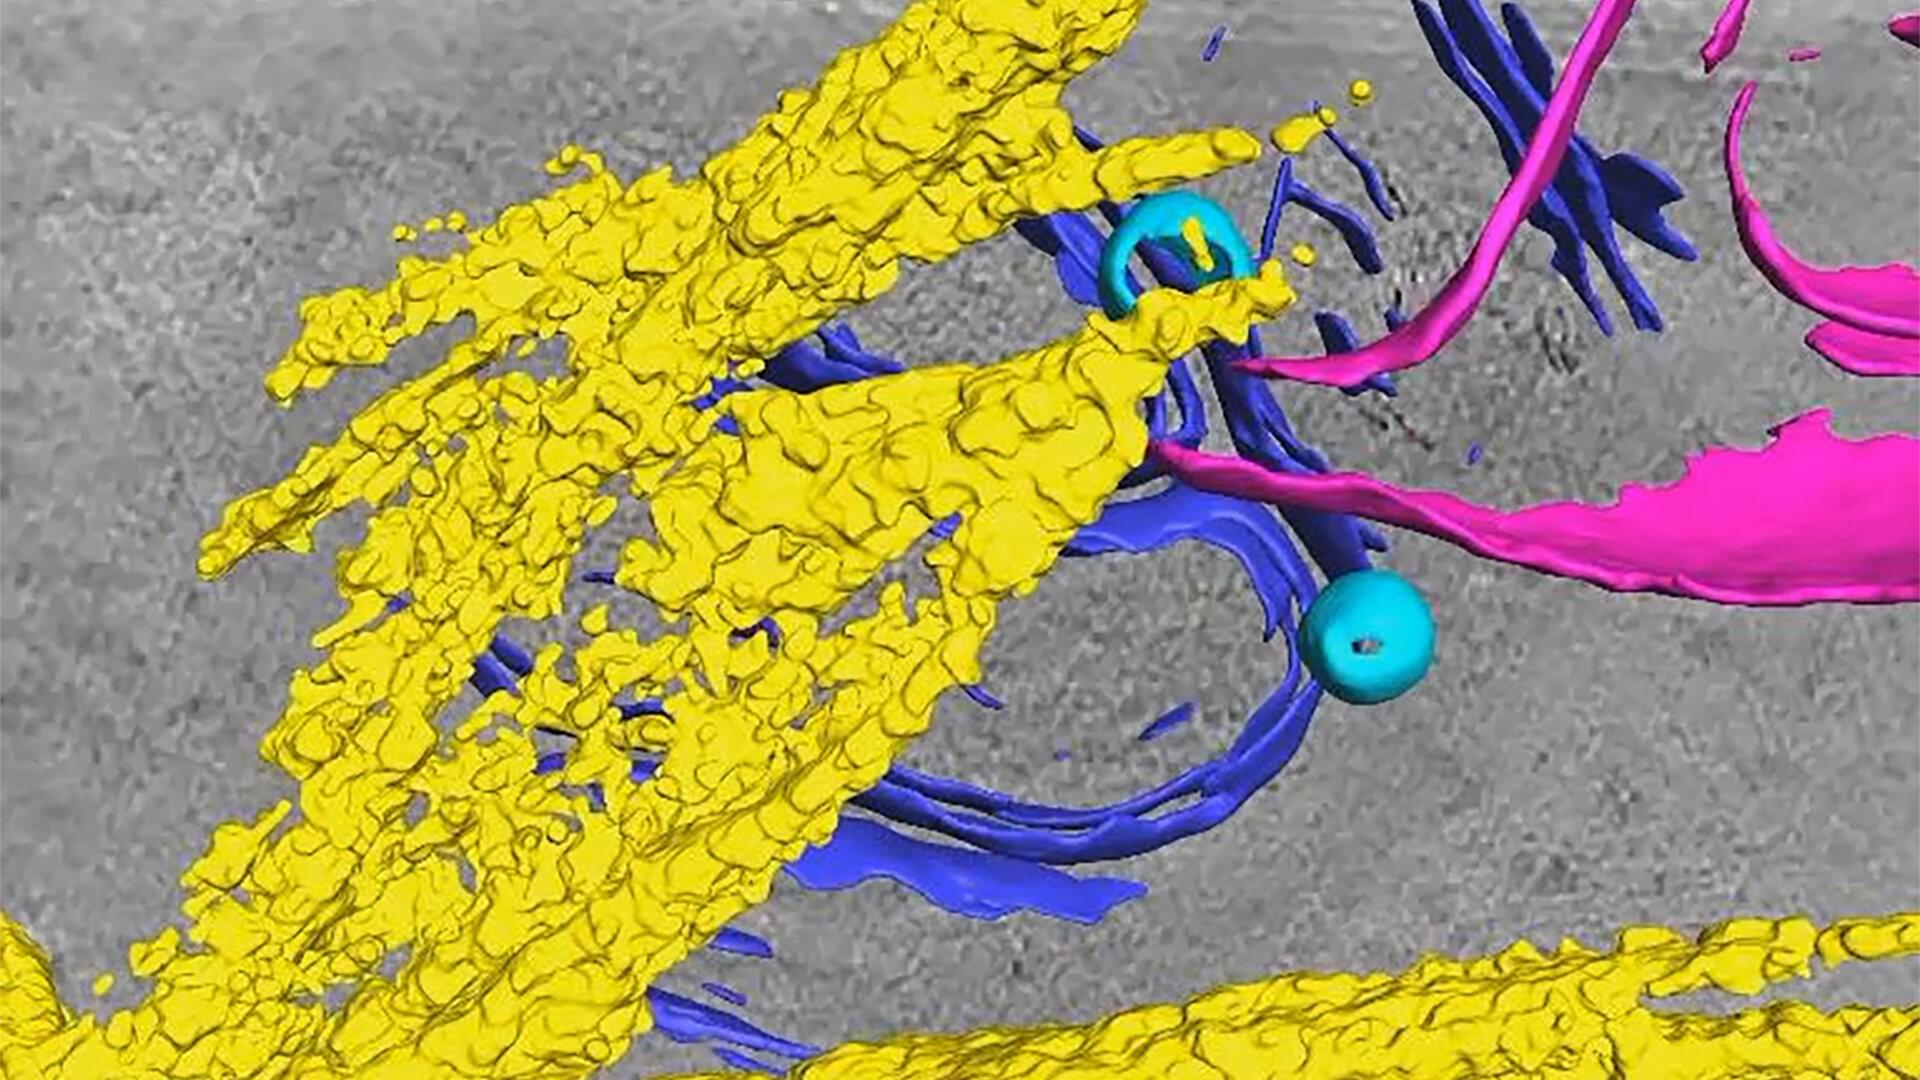
Protein fibers, a hallmark of Alzheimer’s, spotted making genetic deliveries to sperm cells

Unexpectedly, a kind of protein that is usually linked with diseases in the brain may play a vital role in semen, helping shepherd genetic material into sperm cells, scientists at Columbia’s Zuckerman Institute report in the journal Molecular Cell.

These findings raise the possibility that these proteins, known as amyloids, may one day help improve gene-editing technologies such as CRISPR.

“This is wild biology,” said senior author on the paper Anthony Fitzpatrick, Ph.D., a principal investigator at Columbia’s Zuckerman Institute. “Amyloids are most often thought of as a hallmark of Alzheimer’s, Parkinson’s and other neurodegenerative diseases in the brain, but they also have functional roles throughout the body and keep turning up in unexpected places.”

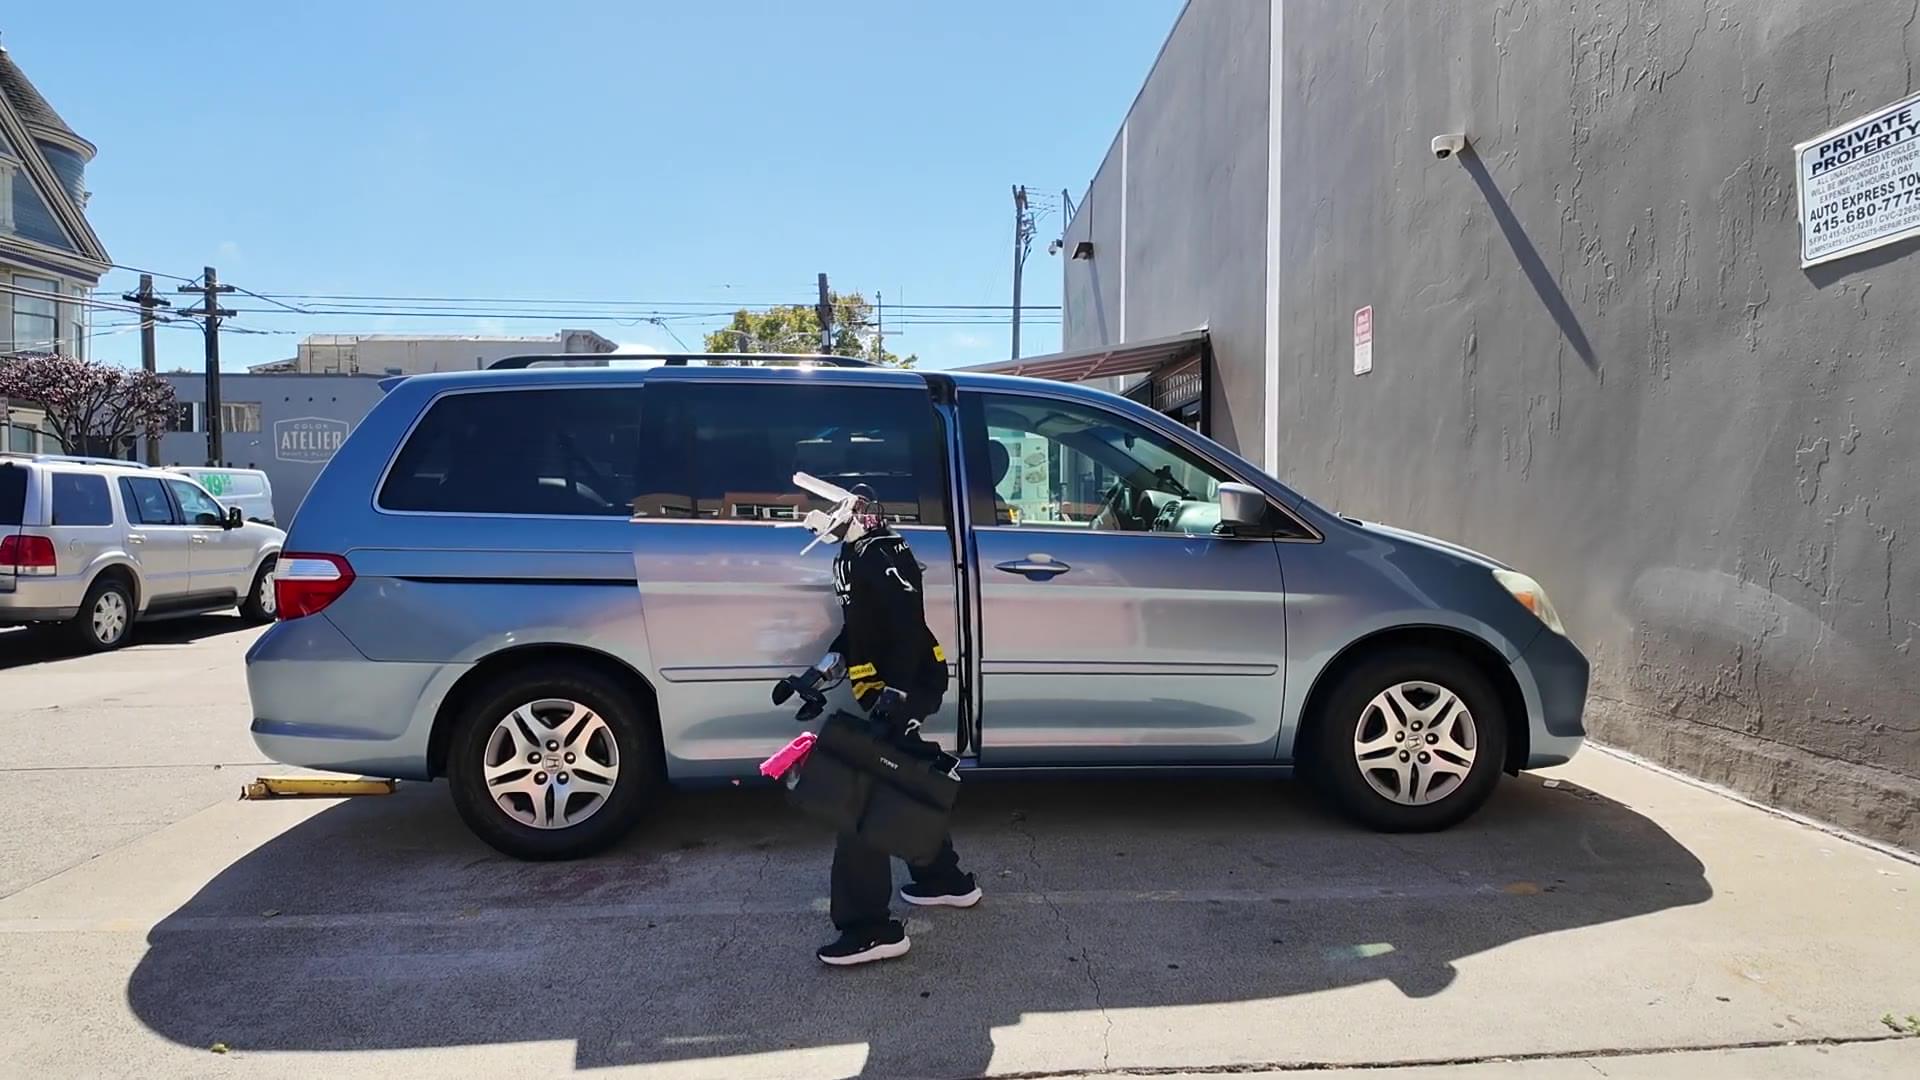
Tau Robotics: Humanoid Cleaning Service in San Francisco

You can now book humanoid cleaners on a recurring subscription, for up to 3 hours per cleaning at https://tau-robotics.com.

Video is first take, uncut, shown at 4× speed. See the reply for detailed footage at 1× speed.


Two humanoid robots clean your home for one, two, or three hours, supervised live by a human operator. Invite-only.