Apple patched CVE-2026–86950, a CoreGraphics flaw that may have been exploited in targeted attacks via maliciously crafted
Hackers have used a malware family called NeedyMantis to maintain long-term access to networks they had already breached, Microsoft said in a technical analysis.
The malware has been seen in a small number of targeted intrusions at telecommunications organizations, universities, medical nonprofits, intergovernmental organizations, and government contractors. Its use goes back to at least October 2025.
Microsoft found NeedyMantis while following up on indicators from Kaspersky’s investigation into the supply chain attack on DAEMON Tools. In that attack, official, signed installers for the DAEMON Tools Lite disk image program carried malicious code from April 8, 2026. The developer replaced them with a clean version on May 5.
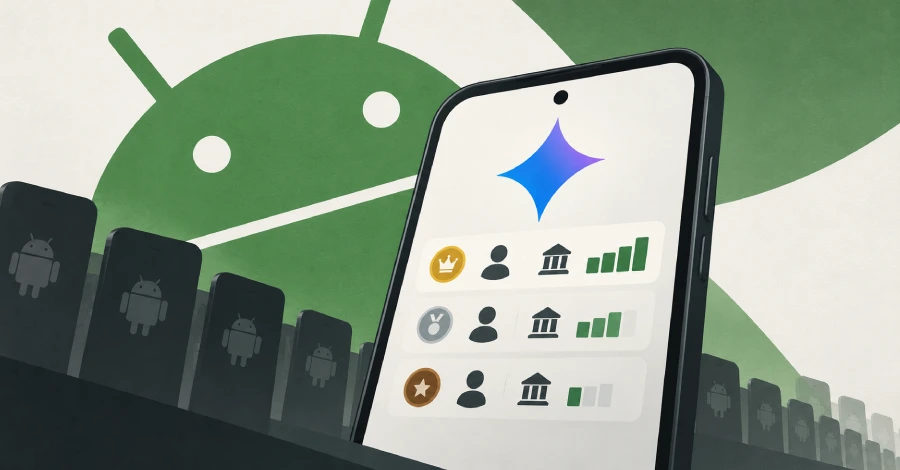
RatHat’s operators build and publish the Android banking trojan and control infected phones from a web console, according to security company Cleafy has traced nearly 100 deployments of that console since April 2026. It said this fits a malware-as-a-service model, in which each customer runs a separate copy.
The console stores what the malware collects from each phone, including text messages and passwords entered into fake login screens overlaid on banking apps.
Its latest version asks Google’s Gemini AI model to estimate each victim’s bank balance from those messages and sorts the phones into high-value and mid-value groups.
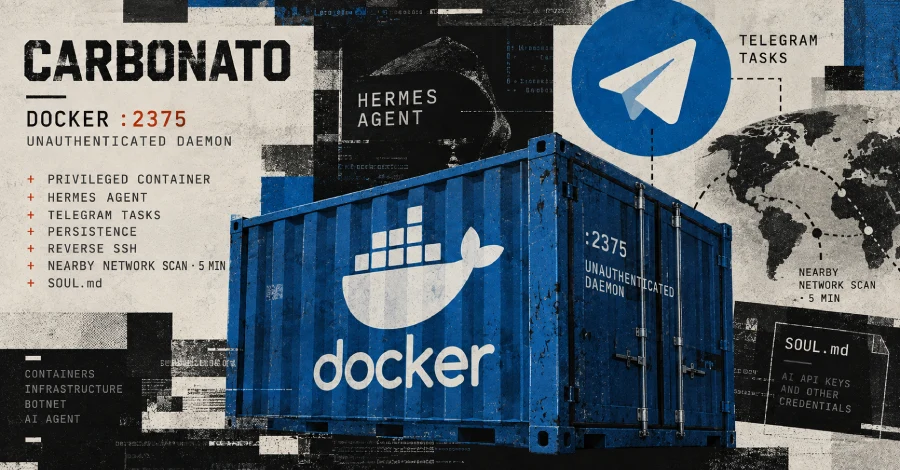
Cybersecurity researchers have disclosed details of a new botnet malware called Carbonato that’s targeting exposed Docker daemons to deploy an open-source artificial intelligence (AI) agent framework called Hermes Agent.
“The implant installs the framework unchanged, then overwrites its SOUL.md persona file,” ThreatDown said. “The 39-line prompt directs it to execute tasks received through Telegram, maintain persistence, and collect credentials.”
At a high level, the botnet breaks into Docker daemons exposed without authentication on port 2,375 and scans neighboring networks every five minutes to propagate further. On each host, it installs Hermes Agent with instructions to follow operators’ Telegram commands.
Researchers found more than 16,000 misconfigured Supabase databases exposing readable tables with personally identifiable information, passwords, or authentication tokens.
Based on the analysis of table schemas, researchers at cyber risk management company UpGuard believe that a very small set of the exposed information includes credit card data.
Supabase is an open-source development platform built around PostgreSQL that provides developers with a range of backend services to build and launch apps and websites faster.
The JadePuffer ransomware operator is targeting Azure tenants with agent-driven attacks that conduct reconnaissance, steal credentials, and destroy core components.
The malware emerged in July, with researchers at cloud security company Sysdig highlighting that it uses AI agents to automate the entire attack chain, from reconnaissance, credential theft, and lateral movement to persistence and data encryption.
Shortly after, the company noted that JadePuffer expanded its focus to AI assets, training datasets, and vector databases, using a tool called EncForge.
A former U.S. Army soldier has been sentenced to 70 months in prison for hacking and extorting at least 10 U.S. technology and telecommunications companies between April 2023 and December 2024.
21-year-old Cameron John Wagenius (also known online as ‘kiberphant0m’ and ‘cyb3rph4nt0m’) was arrested in Texas in December 2024.
He pleaded guilty in February 2025 to hacking AT&T and Verizon after being charged on two counts of unlawfully transferring confidential phone records, and in July 2025 to multiple counts of aggravated identity theft, conspiracy to commit wire fraud, and extortion related to computer fraud.
The ShinyHunters extortion gang is using a URL-encoding trick to bypass web application firewall rules that mitigate the Oracle PeopleSoft CVE-2026–35273 flaw, allowing the threat actors to resume widespread exploitation of a flaw on vulnerable servers.
Google’s Mandiant and Threat Intelligence Group (GTIG) say this new technique has allowed the threat actor to once again target PeopleSoft servers that had not applied security updates and instead blocked access to the vulnerable PSEMHUB endpoint using a WAF.
On June 10, BleepingComputer first reported that the ShinyHunters extortion gang was targeting Oracle PeopleSoft servers using a zero-day vulnerability, allowing them to steal data from 100 organizations.
Cloudflare has fixed a vulnerability in Containers and Sandboxes that allowed customers with a Workers Paid account to recover residual data from other customers’ containers on the same physical host.
Cloudflare Containers is a service available on the Workers Paid plan that lets developers run containerized applications on Cloudflare’s infrastructure, alongside Cloudflare Workers.
Developers and companies building applications on Cloudflare typically use it, including those running backend services, processing jobs, and code execution environments.