Toggle light / dark theme

ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure

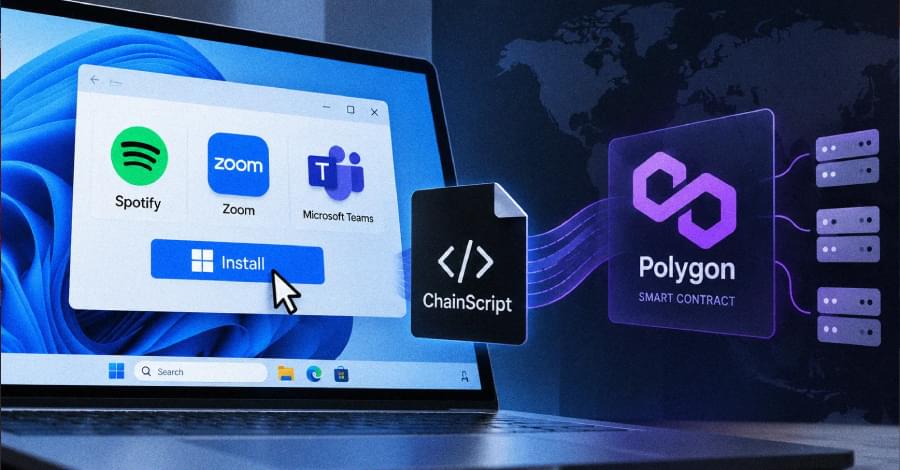
The cybersecurity company described the activity as part of a broader pattern of attacks that employ trusted services and large language model (LLM) shared chats to serve fake installation instructions, while bypassing browser warnings, URL inspection, and Safe Browsing heuristics.

In a report published last month, Microsoft said it observed a macOS ClickFix campaign propagating MacSync and Atomic Stealer using a cluster of no less than 250 look-alike domains.

“The campaign evolved from broadly serving ClickFix lures to using a server-side browser-fingerprinting gate that shows the lure primarily to visitors whose environment appears consistent with a genuine macOS browser,” it said. “This cloaking limits visibility for crawlers, sandboxes, and some automated analysis workflows.”
Microsoft reminds admins to migrate Entra ID users to passkeys

Microsoft has reminded administrators to migrate Entra ID users to phishing-resistant methods, such as passkeys, to avoid sign-in disruptions after it retires SMS first-factor sign-in starting in February 2027.

Admins also have alternatives, including QR code authentication, FIDO2 security keys, and other Entra ID-supported authentication methods.

Before this date, organizations should ensure all users use a phishing-resistant method because they will no longer be able to use SMS or voice to complete multifactor authentication and sign in to their accounts.

The Changing College Degree: Why Students Need Fluency in AI, Emerging Technologies, and Cybersecurity

By Chuck Brooks Higher education is being reshaped by rapid technological convergence—AI, quantum computing, robotics, cybersecurity, biotechnology, and advanced communications—which is dissolving traditional boundaries between academic disciplines and professions. As the document notes, “the traditional boundaries between technology and virtually every other profession are disappearing.” Students no longer need to become engineers, but they must understand how technology works, how to use AI effectively, how to protect digital environments, and how to communicate complex ideas. My article argues that future career readiness depends on a blend of AI fluency, cybersecurity awareness, technological literacy, critical thinking, ethics, and human communication skills.

Google Gemini Broke Into Real Company Systems After Security Test Domain Mix-Up

Google’s Gemini model has become the latest artificial intelligence (AI) system to access the internet and break into other companies during a cybersecurity evaluation. The development was first reported by The Wall Street Journal.

The incidents occurred in May 2026 as part of a test run conducted by Israeli company Irregular. The evaluation partner was also involved in similar hacks disclosed by OpenAI, Anthropic, and Meta.

According to the Journal, the model gained access to a protected system after repeatedly guessing its password. Two other cases related to the model finding credentials in a public repository, allowing it to obtain unauthorized access to protected systems.

Fake LastPass Authenticator GitHub repos push new Rapuncel infostealer

An ongoing malware campaign uses SEO-optimized GitHub repositories to impersonate well-known software firms to push a previously undocumented information stealer called Rapuncel.

LastPass and Delphos Labs uncovered the campaign, which they report impersonates the password manager brand and at least 39 other companies.

Alongside the Rapuncel infostealer, the repositories deliver a Microsoft-signed kernel driver that can disable 145 antivirus and endpoint detection and response (EDR) products.

Microsoft Teams will let admins block custom file extensions

Microsoft Teams will soon let administrators tweak the list of file extensions commonly associated with malware and security threats to meet their company’s security requirements.

This will come as an update to Weaponizable File Protection, a built-in Teams messaging safety feature that scans conversations and blocks chat or channel messages with dangerous, high-risk file attachments.

As detailed in a new Microsoft 365 roadmap entry, the feature is currently in development and will start rolling out in November 2026.

New RatHat Android malware uses AI to automate device control

A new Android malware called RatHat has been discovered, targeting users with an AI-powered subsystem that helps operators remotely navigate compromised devices.

Zimperium zLabs researchers analyzed the malware and believe it is linked to threat actors from China after finding it using LLM prompts written in Chinese.

The researchers say the malware is distributed through malvertising, SMS, and phishing sites promoting APK downloads from outside Google Play.

Brevo supply-chain attack injected ClickFix scripts on customer sites

Brevo confirmed that attackers stole a Cloudflare API key and used it to inject malicious ClickFix scripts into its websites and JavaScript files embedded on customer sites to distribute malware.

The customer relationship management and digital marketing company says the attackers used the API key to create a malicious Cloudflare Worker that modified content at the CDN edge for approximately five and a half hours on September 14.

The attack affected pages on brevo.com, sendinblue.com, login/account/my/onboarding.brevo.com, and sibforms.com. The Cloudflare worker also modified the Brevo forms script, Brevo Conversations widget, and the Brevo SDK loader scripts that customers embed on their websites.