A phishing campaign sent up to 2.37 million weekday emails using invisible Unicode tags to split financial lure words and bypass filters.
Category: cybercrime/malcode – Page 13
Cybersecurity 2026: The Year AI Became The Battlefield And What Comes Next
The state of cybersecurity.
Meta Ads Push StreamRat Android Trojan That Can Gain NearComplete Device Control
StreamRat uses fake streaming ads to reach Spanish-speaking Android users and enables device takeover after sideloading and permission grants.
Fake Software Installers Disable Windows Update and Weaken Microsoft Defender
Bogus software download sites deploy malware that weakens Windows defenses and establishes persistence in China-based operations.
Malicious Apache Modules Hijack Brazilian Government Site Traffic to Push Betting Pages
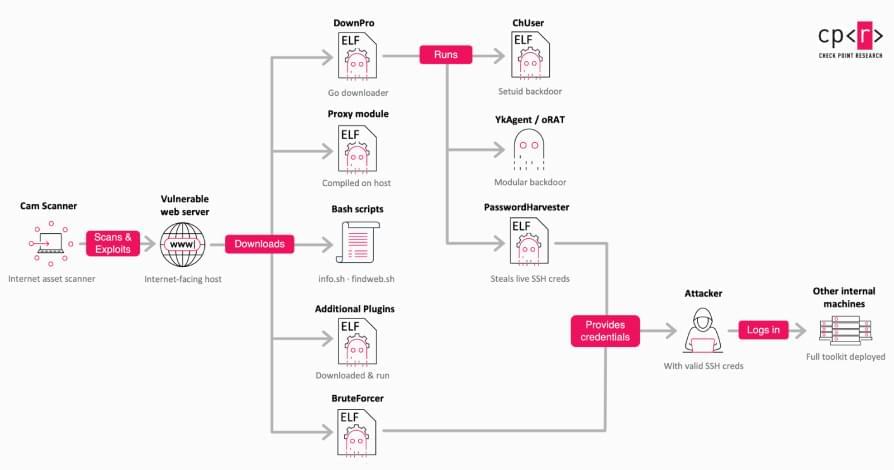
A Chinese-speaking cybercrime cluster known as Gambling Goblin has been observed installing malicious Apache modules on compromised web servers run by Brazilian government and educational institutions, and using them to divert visitors to attacker-controlled pages promoting online gambling and sports betting.
Check Point Research said it has tracked the campaign since mid-2025.
The modules reverse-proxy visitors to a set of phishing pages while the traffic still appears to originate from the legitimate domain. The site’s own security headers are stripped, allowing the injected content to run freely.
BraZetsu Malware Turns Compromised Windows Hosts Into Criminal Marketplace Inventory
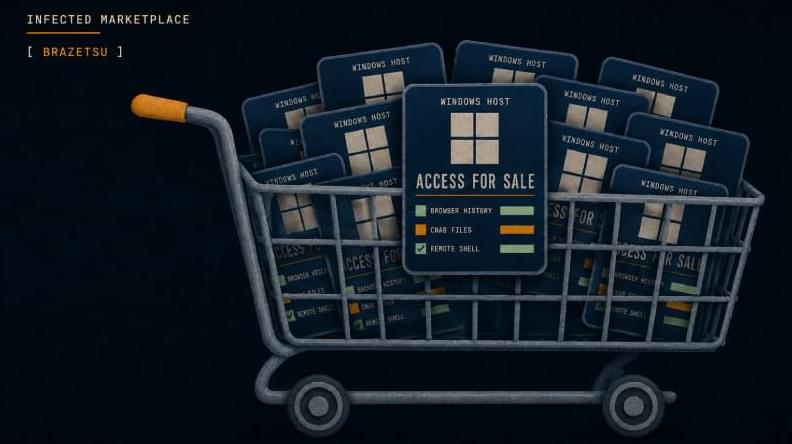
BraZetsu profiles compromised Windows hosts, collects browser and financial data, and stocks the Infected Marketplace.
US Becomes Top Target in RMM Phishing Campaign Spanning 46 Countries
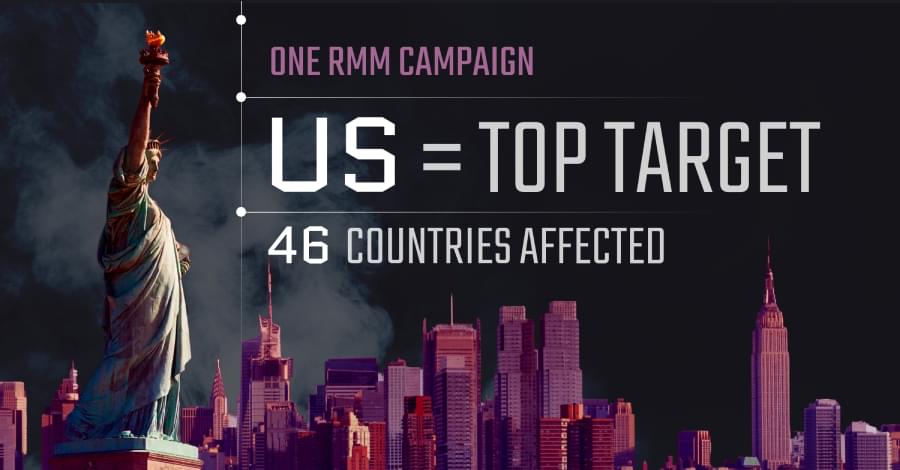
A phishing campaign uses fake documents to install legitimate RMM software across 46 countries, with 45% of activity tied to the U.S.
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks
Threat actors are leveraging the trusted Node.js JavaScript runtime in multiple cyber attacks as a way to deploy malicious payloads.
According to a new report published by the Symantec Threat Hunter Team today, the attack method has been put to use in attacks targeting government departments, technology companies, and hotels since February 2026.
“The technique’s appeal is that node.exe (the binary that runs Node.js) is a legitimate, signed developer tool,” the Broadcom-owned cybersecurity division said in a report shared with The Hacker News. “The attacker’s malicious code lives in interpreted scripts rather than in a binary, making it less likely to trigger signature-based detection, while a registry Run key entry can relaunch the payload at every login.”
Brief independent investigation of agents’ behavior, reasoning and collaboration in the OpenAI / Hugging Face hacking incident
Two METR staff members and a Redwood Research contractor investigated an incident in which OpenAI agents coordinated a multi-day hack of Hugging Face on a shared unsanctioned message board.
Authorities Turn Sality’s P2P Network Against Itself, Cutting Off New Malware Payloads
Authorities sinkholed Sality’s P2P botnet and seized linked domains, cutting off new payloads while existing malware remains active.