Toggle light / dark theme

Hidden prompts can plant false memories in AI agents, researchers warn

Large language models (LLMs), the computational algorithms underpinning ChatGPT, Gemini and other artificial intelligence (AI)-powered conversational platforms, are now widely used worldwide. These models can rapidly answer questions, source information online, assist users with specific tasks and produce text tailored for specific purposes.

Over the past few years, computer scientists have introduced a wide range of LLMs, some of which can also complete tasks autonomously and take actions on a user’s behalf, for instance, answering messages, scheduling online appointments or updating programming code. More recently, they have also provided many of these models with memory, as this allows them to tailor responses around a user’s typical preferences or earlier requests without repeatedly receiving the same information.

While memory-enhanced AI agents have notable advantages and could better meet the needs of individual users, they also pose new security risks. Researchers at New Mexico State University recently described a cyberattack that secretly poisons an AI agent’s long-term memory, which they dubbed GhostWriter. Their paper, published on the preprint arXivserver, introduces two promising strategies that could help prevent or limit the risk of this attack without adversely affecting an AI agent’s performance.
Arch Linux disables AUR package adoption to stop malware flood

The Arch Linux project has temporarily disabled adoption of Arch User Repository (AUR) packages after a surge in malicious takeovers of existing packages.

The decision was announced on the distribution’s mailing list by contributor Robin Candau, who said that the situation is temporary until a solution is found.

“Due to the current influx of malicious package adoptions and follow-up commits made via the AUR, package adoption is currently disabled while we are handling the situation,” announced Candau.

Hackers Exploit AnySign4PC via Hacked Korean Sites to Install Backdoors Without Prompts

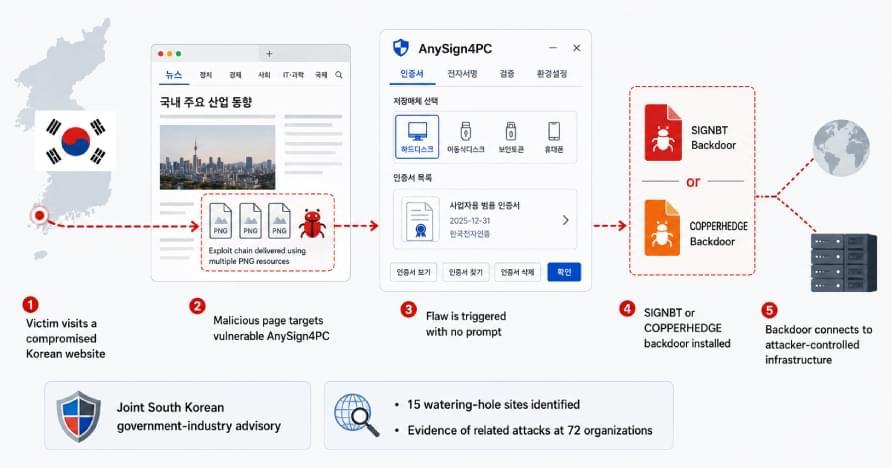
South Korean authorities and four security firms have disclosed a state-sponsored campaign that compromised trusted domestic websites. The attackers used those sites to exploit locally installed financial-security software and infect targeted visitors with SIGNBT or COPPERHEDGE backdoors.

A compromised page could infect a system running a vulnerable AnySign4PC version without a prompt or user-initiated download. The Korea Internet & Security Agency (KISA) says AnySign4PC versions 1.1.4.4 through 1.1.4.6 are affected and lists version 1.1.5.0 as the fixed release. It recommends deleting vulnerable installations.

AhnLab refers to two exploited products only as financial-security software A and I. Its report does not disclose their identities, affected or fixed versions, or vulnerability identifiers.

Analog Devices discloses data breach, says operations unaffected

American semiconductor company Analog Devices announced that an unauthorized party accessed some of its systems and exfiltrated certain files.

The company detected the incident on June 23 and reacted by activating its incident response protocols to limit the breach. External cybersecurity experts have been contracted to assist with the containment and investigation activities.

Currently, there are no details about the type of data that has been compromised.

Google says AI helped Chrome fix 1,072 security bugs in two releases

Google says artificial intelligence is dramatically increasing the number of security vulnerabilities it can find and fix in Chrome, with more than 1,000 security bugs patched across the browser’s two most recent releases as it expands its use of AI.

According to Google, Chrome 149 and Chrome 150 fixed 1,072 security bugs, surpassing the total number fixed across the previous 23 Chrome milestones combined.

The company says it now uses large language models throughout the vulnerability management process, including discovering flaws, reproducing reports, determining severity, assigning bugs to developers, generating candidate patches, and creating tests.

Artificial Intelligence: The Definitive Primer for the Acceleration Era: Understanding AI, Technology Convergence, Cybersecurity, and the Future

Artificial intelligence is not simply another chapter in the history of technology. It is becoming the cognitive infrastructure of modern civilization. Like electricity transformed the Industrial Age and the Internet transformed the Information Age, AI will define the Intelligence Age. Its true power will not come from replacing people, but from amplifying human ingenuity through the convergence of computing, cybersecurity, robotics, quantum science, biotechnology, and human creativity. The future will belong to societies that innovate boldly, secure wisely, govern responsibly, and never lose sight of the fact that technology should ultimately serve humanity—not the other way around.

The US Robot Import Ban Doesn’t Stop China — It Redirects It

The FCC just banned new foreign-made humanoid robots and robot dogs, citing cybersecurity risks. With China holding ~85% of the global humanoid market, this is effectively a China ban.

But the ban only closes the US market. Chinese manufacturers’ production capacity and export ambition remain intact. The real result is intensified sales pressure on Southeast Asia, Africa, and other open markets — with more aggressive pricing and Robot-as-a-Service deals.

For buyers outside the US, this creates short-term opportunities… and the same data-dependency risks US regulators just cited as the reason for the ban.

Full analysis: [ https://creedtec.online/the-us-robot-import-ban-doesnt-stop-…irects-it/](https://creedtec.online/the-us-robot-import-ban-doesnt-stop-…irects-it/)

#HumanoidRobots #IndustrialRobotics #China #TradePolicy


The US import ban on Chinese robots may reshape global markets, redirecting exports toward Africa and Southeast Asia instead of stopping them.

Computer scientists design a cyberattack to prevent cyberattacks

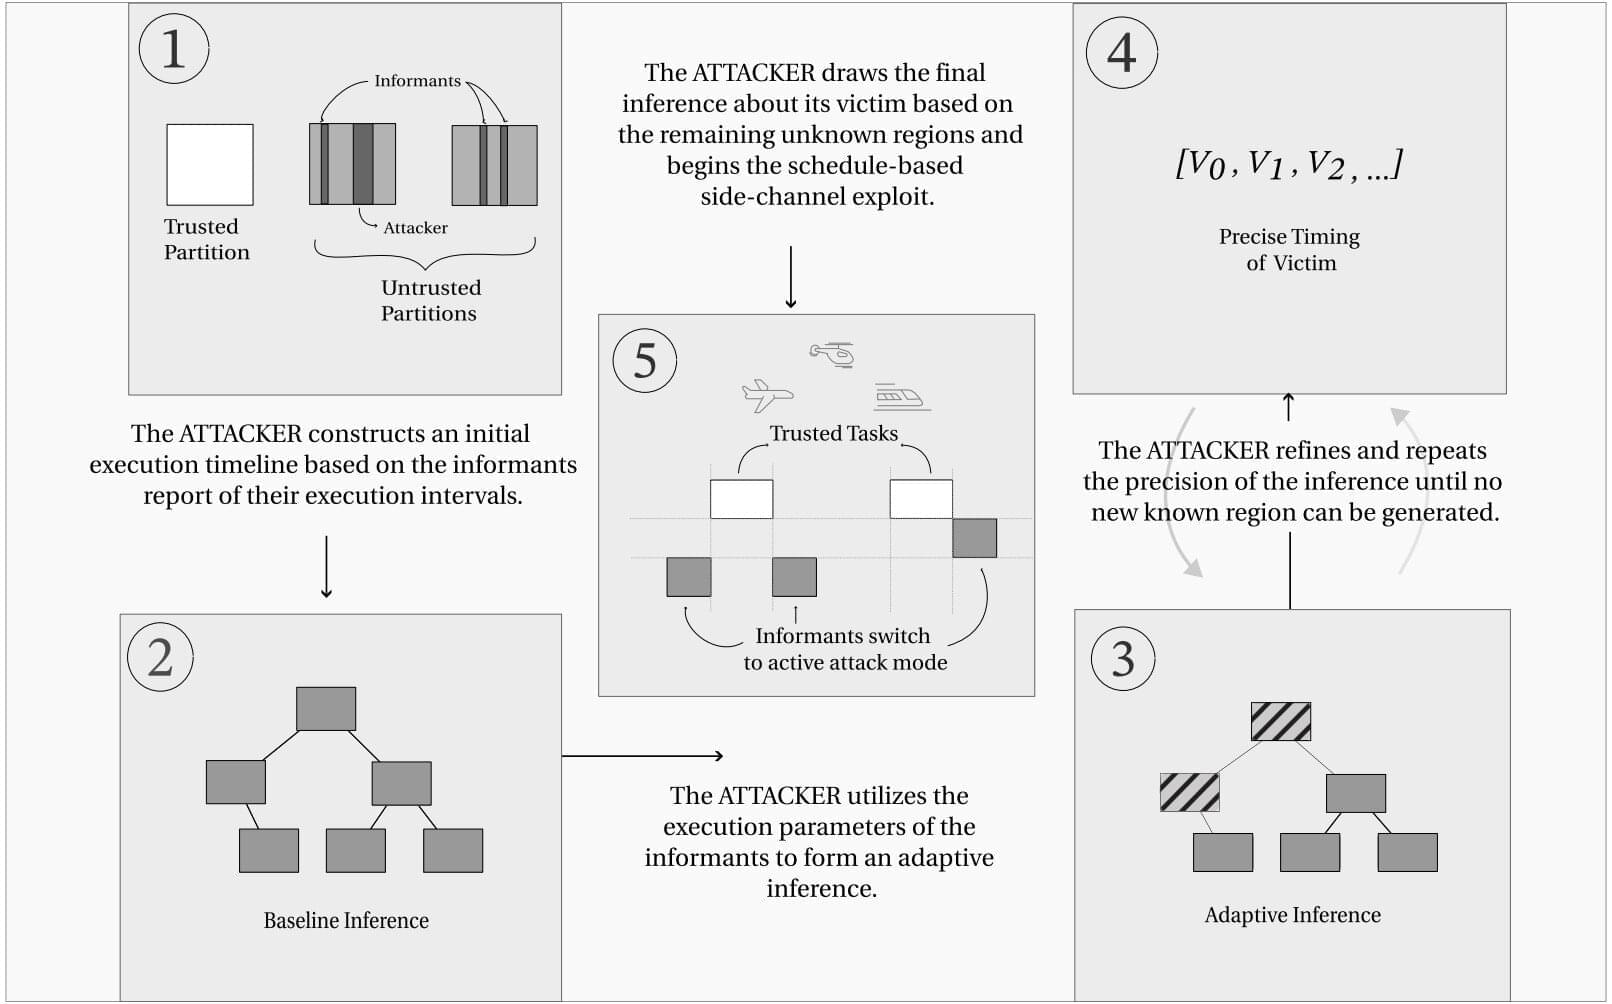
Protecting sensitive, precision-timed computing systems requires understanding the nature of cyberthreats. So researchers from Washington State University teamed up with experts at the University of Colorado Colorado Springs and Metro State University to design an attack—dubbed NosyNeighbor—that lurks on the sidelines of time- and safety-critical computer systems, “infers” what’s happening inside and adapts its malicious approach.

/* */