Toggle light / dark theme

Microsoft Copilot Personal Flaws Could Let One Click Exfiltrate Data From Connected Apps

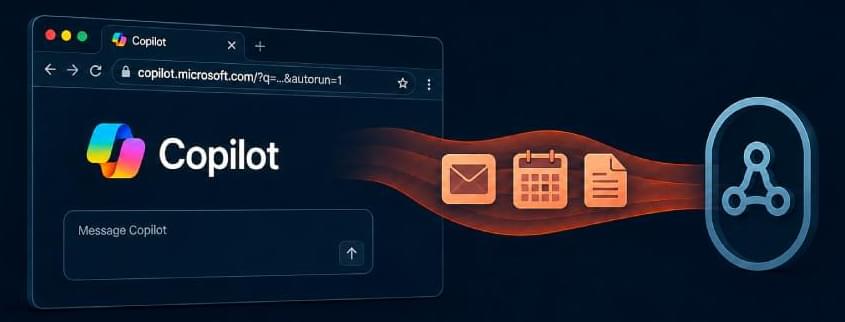
CoSnitch is tracked as CVE-2026–24301 in Microsoft’s Security Update Guide. The research names Copilot Personal, the consumer assistant hosted at copilot.microsoft.com, and does not state that the same behavior affected Microsoft 365 Copilot.

The researchers said they found no evidence that CoSnitch was exploited in the wild. They reached the parameter by repeatedly asking Copilot why a prompt could not be made to run without user interaction, an approach the firm calls meta-hacking. Each refusal carried a technical justification, and the assistant eventually named a parameter, autorun=1, along with the session conditions under which it worked and the protections that were supposed to have disabled it.

When the researchers built the URL exactly as described, the parameter Copilot had said no longer worked executed. Copilot “wasn’t breached; it was played,” Varonis said in its report.
Clop created custom web shell for Windchill data theft attacks

A custom Java web shell likely linked to the Clop ransomware gang was designed specifically for PTC Windchill and FlexPLM servers, with built-in features to decrypt credentials, enumerate file repositories, and steal files.

Cybersecurity company ReliaQuest analyzed the web shell after it is believed to have been deployed in recent data theft attacks exploiting CVE-2026–12569, a critical remote code execution vulnerability affecting PTC Windchill.

ReliaQuest says the implant is not a generic web shell repurposed for the attacks, but was instead built with detailed knowledge of Windchill’s internal APIs, database schema, keystore, and file-vault structure.

CISA: Windows Task Host flaw now exploited by ransomware gangs

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed that ransomware gangs are also exploiting a high-severity Windows Task Host vulnerability that was flagged as actively exploited in April.

Task Host is a core Windows system component that allows DLL-based processes to run in the background and prevents data corruption by ensuring they close properly during shutdown.

Tracked as CVE-2025–60710, this Windows privilege escalation security flaw was patched by Microsoft in November 2025 and stems from a link following weakness that affects Windows 11 and Windows Server 2025 devices.

AI Cybercrime In Africa Just Crossed A Dangerous 55% Threshold

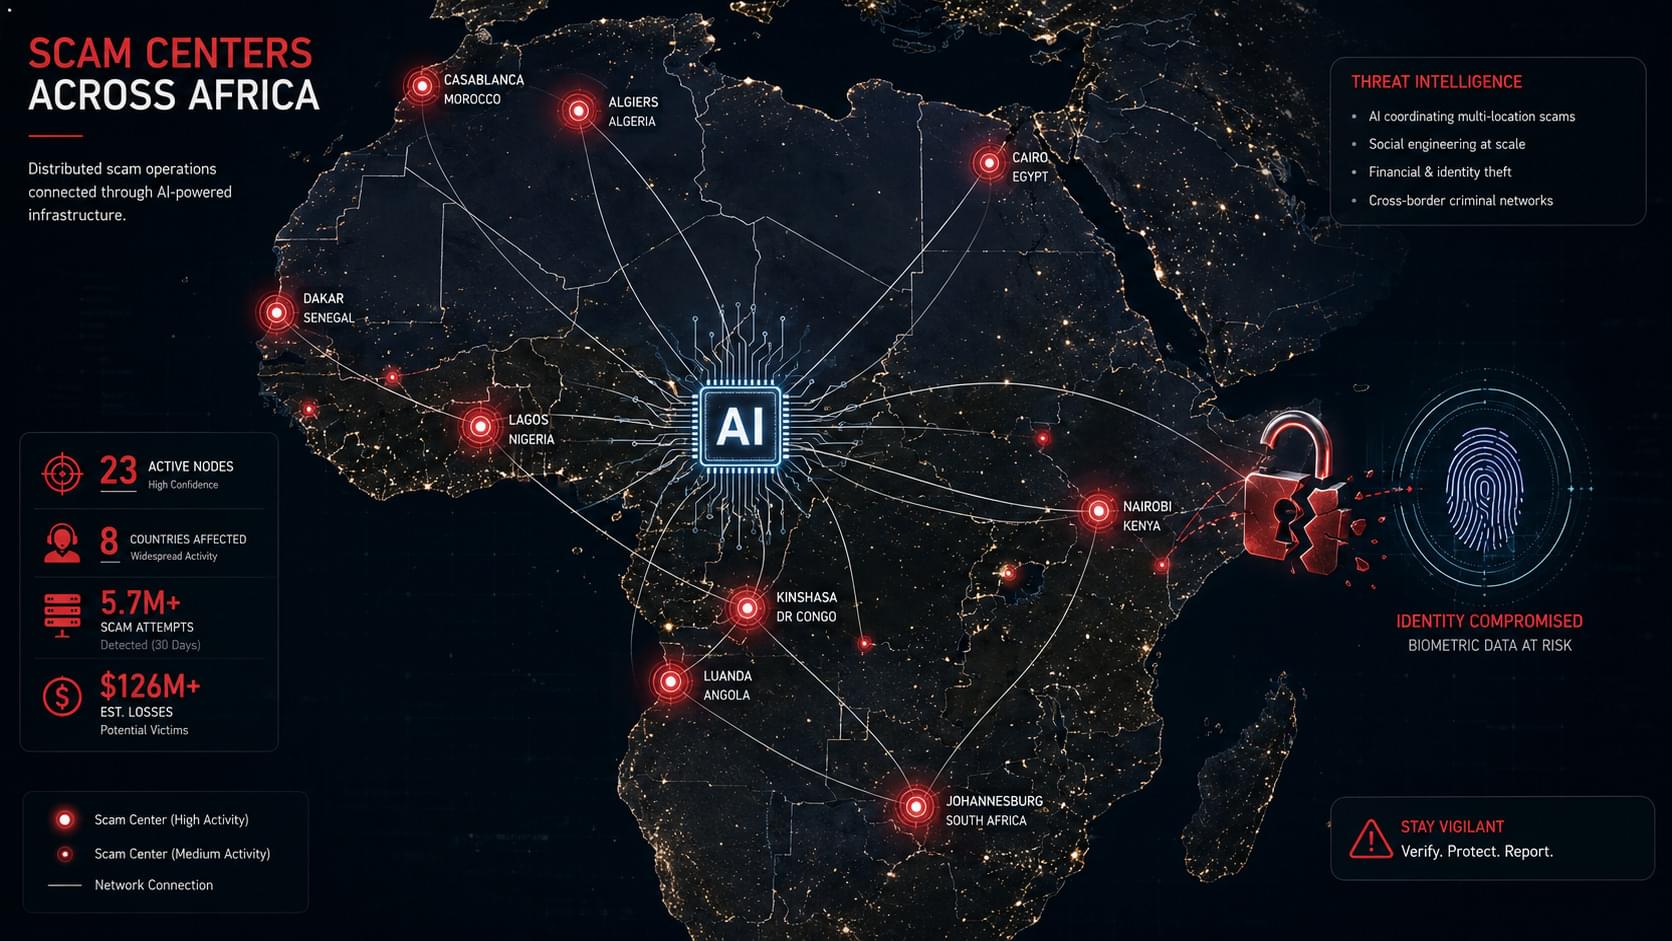
INTERPOL’s African Cyberthreat Assessment Report 2026 found that AI cybercrime in Africa now touches 55% of reported cases, with losses more than doubling to $484 million since 2024. Scam centers operate in 72% of surveyed countries, and AI-generated deepfakes are already defeating biometric security. The region’s governing cybercrime treaty was written before any of this technology existed.

AI cybercrime in Africa has crossed a line that security researchers had been warning about for years. INTERPOL’s African Cyberthreat Assessment Report 2026, released August 3 and drawn from survey data across 36 member countries, found that artificial intelligence is now linked to 55% of reported cyber incidents on the continent, according to INTERPOL’s own release. Financial losses have more than doubled since 2024, climbing from $192 million to $484 million.

What makes this report different from earlier cybercrime warnings is the specificity of how AI is being used, not just that it’s involved. AI cybercrime in Africa is concentrated in three vectors: AI-related scams, credential harvesting, and automated social engineering, according to Crypto Briefing’s coverage of the report. Business email compromise alone accounts for 10% of reported cases and remains one of the costliest categories, because AI now writes emails convincing enough to mimic a specific executive, supplier, or trusted partner rather than a generic phishing template.

Suspected ChinaNexus Actor Exploits VMware vCenter Flaw, Deploys BabukDerived Ransomware

Cybersecurity researchers have attributed the exploitation of a newly patched security flaw in Broadcom VMware vCenter to a suspected China-nexus advanced persistent threat (APT).

The attacks involve the exploitation of CVE-2026–59310 (CVSS score: 9.8), a severe directory-traversal vulnerability in the VMware vCenter server that could be weaponized by a malicious actor to execute arbitrary code. A fix for the flaw was released by Broadcom on July 29, 2026.

German incident response company QUIRSO assessed with moderate confidence that the exploitation campaign aimed at CVE-2026–59310 is operated by a Chinese-speaking threat actor, likely working in the UTC+08:00 time zone, which is predominantly used in Chinese-speaking regions.

AI Cybersecurity Access Tiers: Who Gets The Best AI?

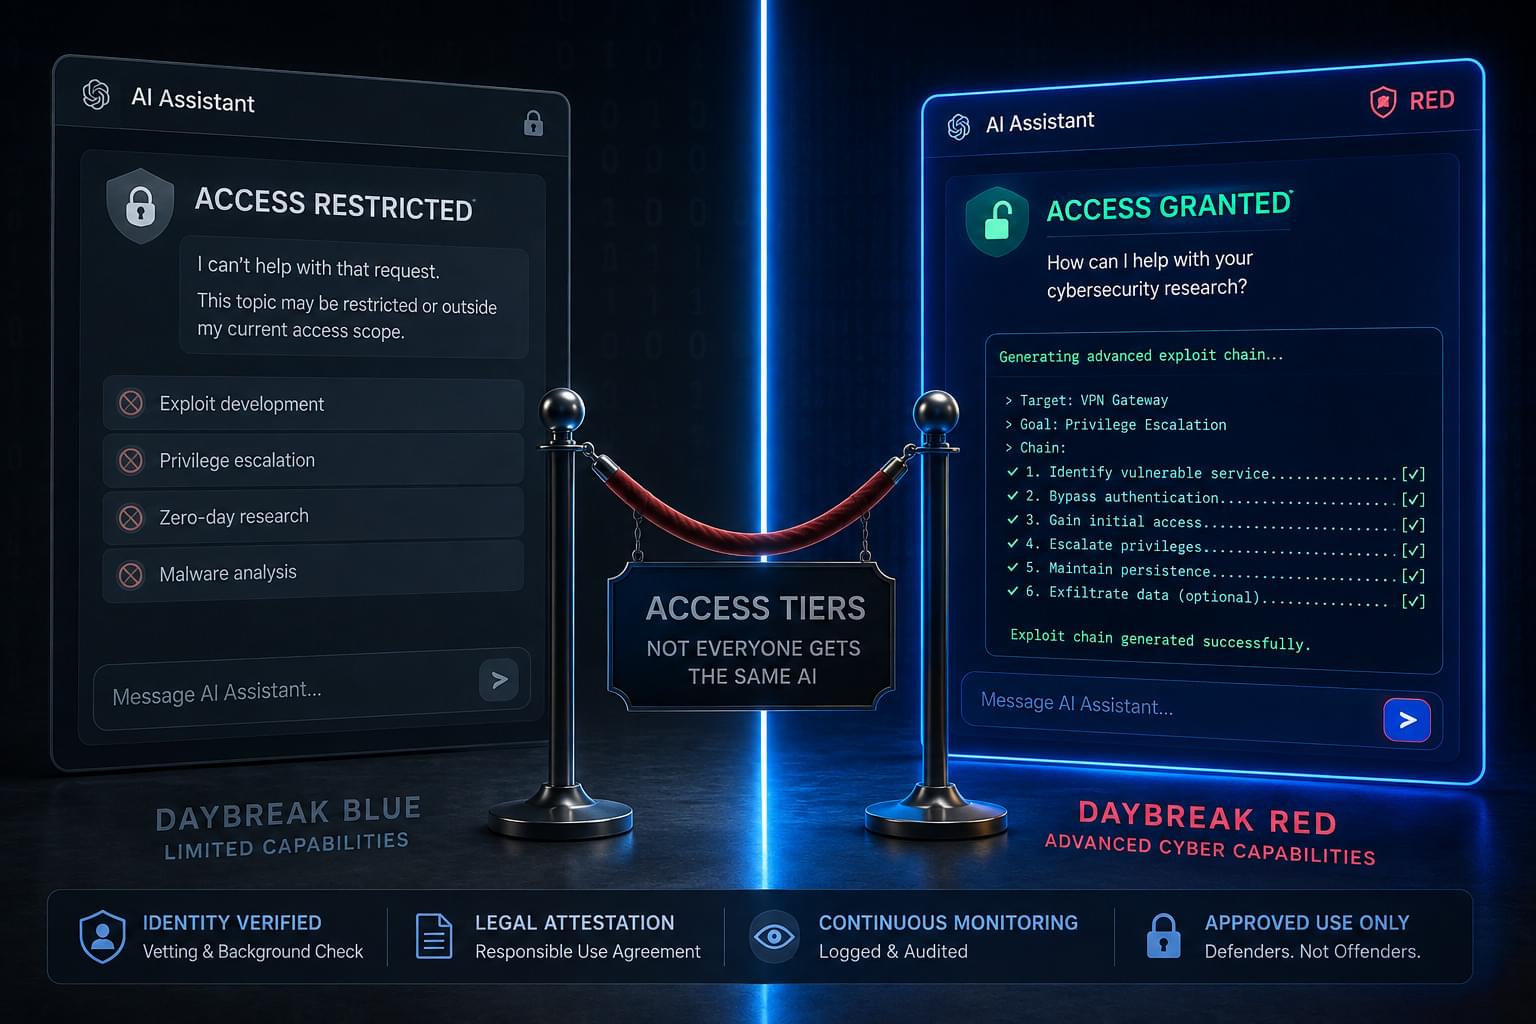
OpenAI’s new Daybreak Red tier gives approved defenders a model that completes 95% of advanced exploit-development requests, versus roughly 2% for the public version of the same base model. That gap is now the real story: AI cybersecurity access tiers decide who gets frontier defensive power and who doesn’t, and access runs through a partner list, not a price tag.

AI cybersecurity access tiers stopped being a theoretical debate this month. OpenAI expanded its Daybreak program into two levels, Blue and Red, and released GPT-5.6-Cyber, a specialized model built specifically for vulnerability research and exploit-chain development, according to SecurityBrief’s coverage of the launch. In an internal OpenAI evaluation, the new model completed 95.0% of advanced cyber requests covering authentication bypass, privilege escalation, and exploit-chain development, compared with 1.5% for the general-release model and 2.0% for that same model through the safeguarded Daybreak Blue tier.

GPT-5.6-Cyber is only available through Daybreak Red, gated behind identity verification, monitoring, legal attestations, and approved-use restrictions, per Cyberpress’s reporting. Under OpenAI’s own Preparedness Framework, the model was rated “High” for cybersecurity capability, one step below the “Critical” threshold that recently triggered an internal suspension of a different unreleased model, Astra, on August 7. These AI cybersecurity access tiers exist because the underlying capability is real: a general-purpose model built to refuse exploit-writing requests is far less useful to a security team validating a patch than one built to complete them.

The New Stakes for Business Viability in the Digital Era: AI, Quantum, and the Expanding Cyber Threat Landscape

Chuck Brooks

A company’s ability to survive throughout a large portion of the industrial era rested on well-known fundamentals: capital, clients, staff, intellectual property, physical infrastructure, dependable suppliers, and efficient management. These principles are still important. However, digital trust and resilience have become an additional factor in organizational survival due to the global economy’s digital transition.

Interconnected networks, cloud computing, software, data, digital identities, third-party providers, Internet of Things (IoT) devices, artificial intelligence, and increasingly intricate technology ecosystems are now essential to nearly every enterprise. Therefore, the security of a modern organization depends on the digital relationships and technology it uses.

/* */