Toggle light / dark theme

Physicists define new material blueprint for next-generation microchip encryption

Behind every secure online transaction or encrypted message lies a string of completely unpredictable numbers. A team of physicists has now proposed a theoretical way around a long-standing roadblock, opening the door to next-generation security chips that protect everyday data without slowing performance.

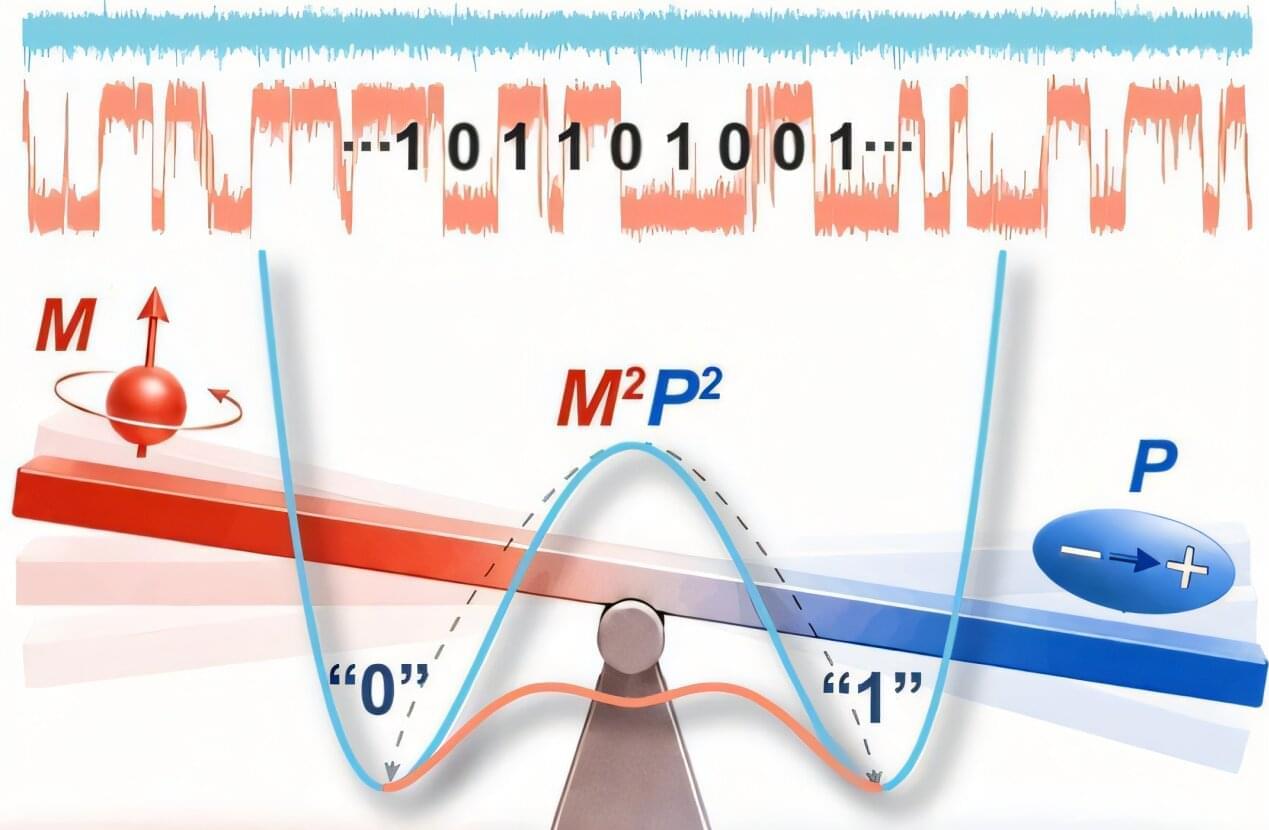
In a study published in Physical Review Letters, a research team co-led by Rice University’s Jun-Jie Zhang and Boris Yakobson describes a new class of materials. The research was conducted in collaboration with Shuai Dong, chair of the School of Physics at Southeast University in China.

These materials, called autferroics, could speed up physical true random number generators (TRNG) thousands of times while keeping signals clear.
Hackers start exploiting critical WordPress flaw for code execution

Threat actors have moved from probing WordPress sites vulnerable to CVE-2026–87902 to exploiting the flaw to write files to disk that execute shell commands when accessed.

Initial attack traffic was only for reconnaissance and started less than five hours after the patch was released in WordPress 7.1.2. Malicious activity increased by ten times, and attackers are now trying to deliver payloads.

WordPress security firm Patchstack reports that it observed the first malicious requests at 17:44 UTC on September 22 from a small group of IP addresses targeting multiple sites under its protection.

AI & the Threats & Dangers of Data Poisoning

Chuck Brooks is the president of Brooks Consulting International and one of Executive Mosaic’s GovCon Experts.

In my book Inside Cyber, I explored how artificial intelligence has evolved into the most potent weapon in an attacker’s arsenal as well as our most effective defensive tool. This dual nature is at the core of a significant change in security and privacy. The rate of change has only quickened since the book was released. We have advanced further into what I refer to as the Acceleration Era, in which AI systems, including large language models, or LLMs, improve quickly, incorporate into crucial processes and have a growing impact on business, governmental and societal decisions.

Data poisoning, or the intentional or unintentional contamination of the training data that forms these models, is one of the most pernicious new threats in this setting. Recent studies have highlighted LLMs’ continued vulnerability. A surprisingly small number of carefully constructed malicious documents, roughly a few hundred—can implant backdoors or change behavior in models with hundreds of millions to billions of parameters, according to studies, including collaborative work involving Anthropic, the UK AI Security Institute and the Alan Turing Institute. The amount of poisoned material does not have to increase in proportion to the size of the model or the amount of training data. The malicious samples’ absolute presence is what counts.

Quantum communication protocol enables three users to establish a shared secure key

Quantum key distribution allows two users to establish secret keys whose security is grounded in the laws of quantum mechanics. Extending this capability to multiple users is an essential step toward quantum networks that support secure communication among many participants. Quantum cryptographic conferencing addresses this need by enabling multiple users to share the same secure key, which they can then use to protect group communications.

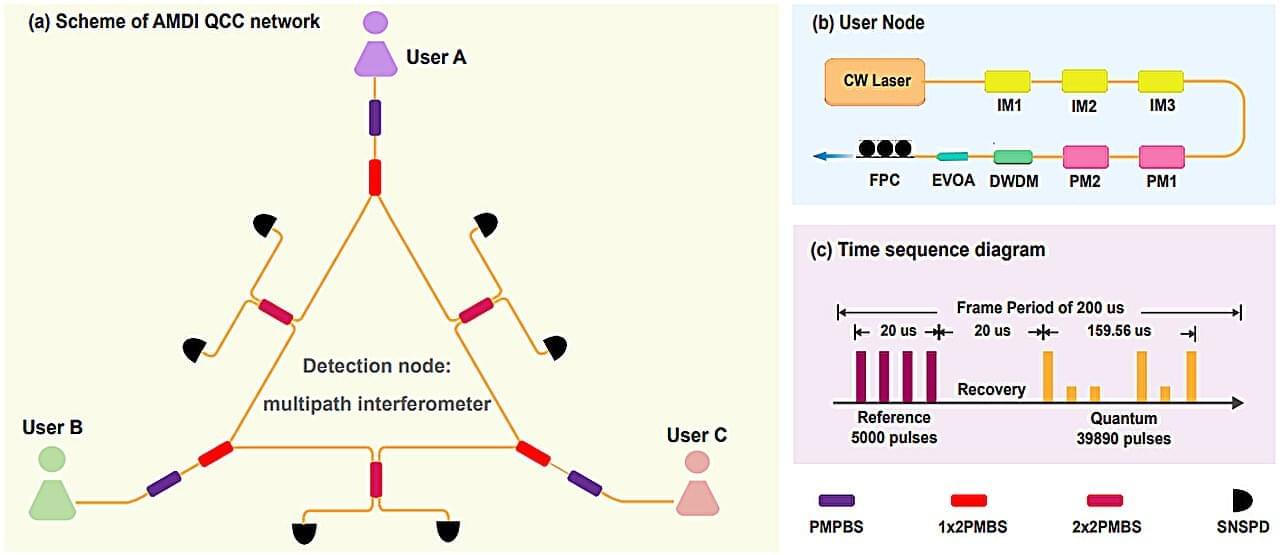
In an article published in Physical Review Letters, a team led by professor Xiao-Song Ma at Nanjing University reports the experimental realization of asynchronous measurement-device-independent quantum cryptographic conferencing, or AMDI QCC. The demonstration addresses two major challenges in developing practical quantum networks: maintaining useful key-generation rates as networks grow and reducing the complexity of controlling optical phases.

As illustrated above, three users independently send optical pulses to a shared GHZ measurement station, where a fiber-based multipath interferometer enables interference between signals from different users and single-photon detection.

Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDR

A fake LastPass Authenticator installer offered on GitHub installs a Windows kernel driver that shuts off antivirus and other security software before a password stealer runs if a victim downloads and runs it, researchers at LastPass and Delphos Labs said on September 17.

Microsoft’s own hardware-compatibility program signs the driver, scored zero detections on VirusTotal when researchers checked it in August, and was not on Microsoft’s list of blocked drivers. LastPass says none of its own systems, services, or customer vaults were touched, and that the attackers only borrowed its name.

The lure is a fake GitHub page (github.com/LastPass-Authenticator) that ranks in search results for terms like “LastPass Authenticator download” and looks like a real LastPass product page.

Microsoft: September updates break File History backup feature

Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after installing the September 2026 security updates.

File History (introduced in Windows 8 and replaced by Windows Backup, which backs up data to OneDrive) automatically saves copies that let users recover accidentally deleted or damaged files using an older version from hours, days, or weeks ago.

By default, File History backs up all folders under the user’s account profile (Documents, Music, Pictures, Videos, and Desktop) to an external hard drive, such as a USB flash drive, or a network storage location (NAS).

WordPress Click2Shell flaw lets hackers execute PHP on the server

Technical details and a proof-of-concept exploit have been published for a new WordPress cross-site request forgery (CSRF) vulnerability dubbed ‘Click2Shell’ that affects the platform’s Core component.

The security problem does not have an official identifier but was addressed last week with the release of WordPress version 7.1.1.

It is a pre-authenticated remote code execution chain that allows an attacker to install any theme in the official WordPress.org catalog and run an arbitrary PHP file.

Microsoft fixes broken Excel copy and paste for all Office users

Microsoft has fixed a known issue that causes copy-and-paste failures for Excel users after installing the September 2026 security updates.

The bug was confirmed following a wave of customer reports on Reddit and the Microsoft Q&A forums that this month’s updates (including the KB5002914 security update) break copy-and-paste, autofill, and formula dragging in Excel.

“In Microsoft Excel 2024, 2021, 2019, and 2016, as well as Excel Online in Office Online Server, the paste operation might fail silently,” Microsoft explains in a support document updated on Friday.

/* */