It’s fully keyframable in Sequencer and supports both Deferred and Path Traced rendering.
Category: futurism – Page 18
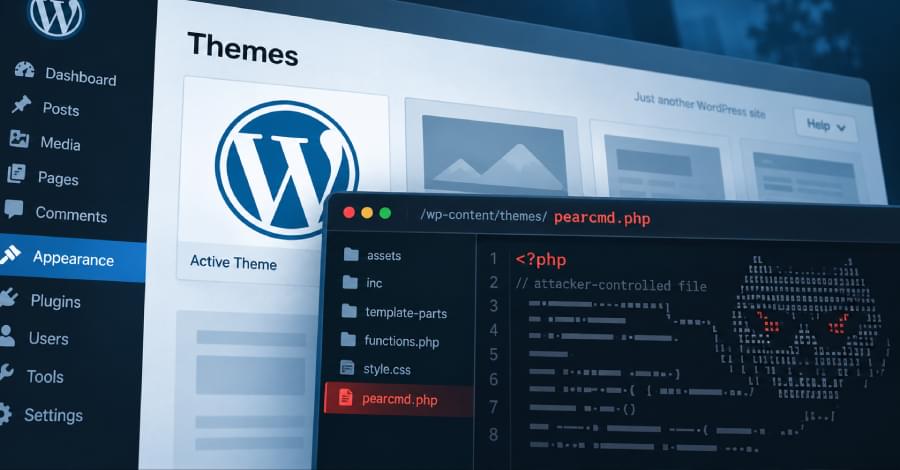
Attackers Exploit WordPress CVE-2026–87902 Within Hours of Disclosure
Attackers are exploiting WordPress CVE-2026–87902 to include pearcmd.php and write PHP files when specific theme and server conditions are met.
Exposed GitLab project email addresses let attackers push code
Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports.
The addresses are part of a built-in GitLab feature called “Email work item to this project” and contain a long-lived token tied to the developer’s account.
These addresses are generated automatically and contain a string that serves as a credential for creating work items via email. When an external client sends a message to one of them, GitLab parses it into a project issue or task.
SONY WALKMAN IS BACK! IN 2026 😐😯#shorts
🎧 Sony Walkman: https://link.amazon/B0i0MG1hE (Affiliate Link)(As an Amazon Associate, I earn from qualifying purchases)Are you entirely tired of constant s…
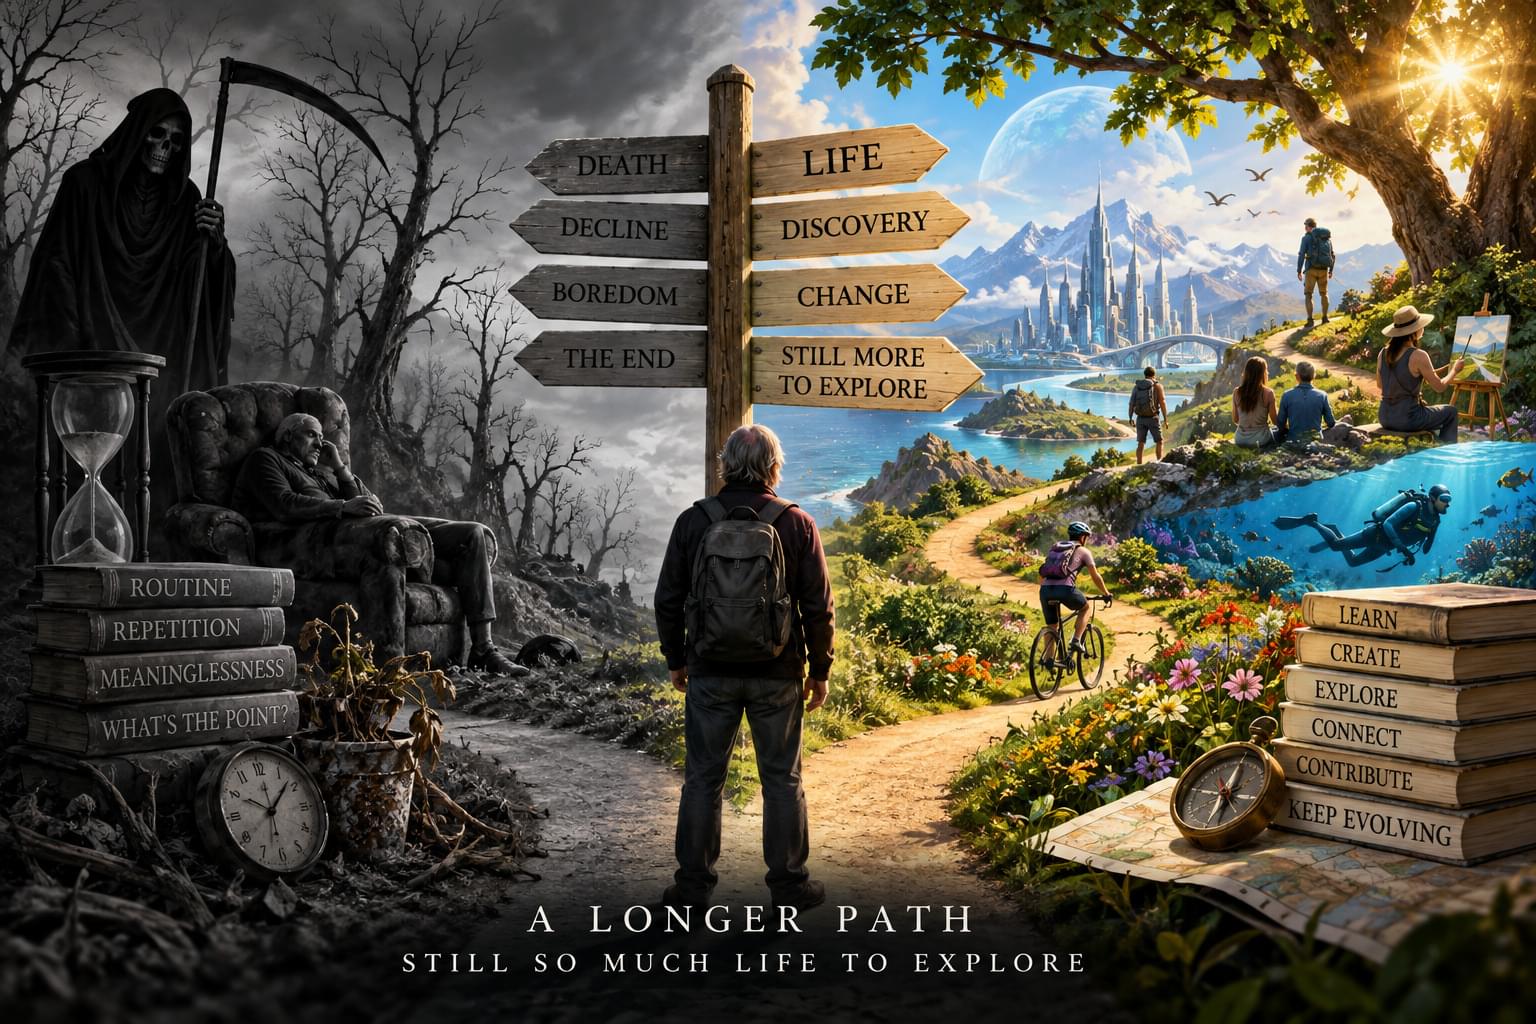
Is There a Right Time to Die?
The Open-Ended Life
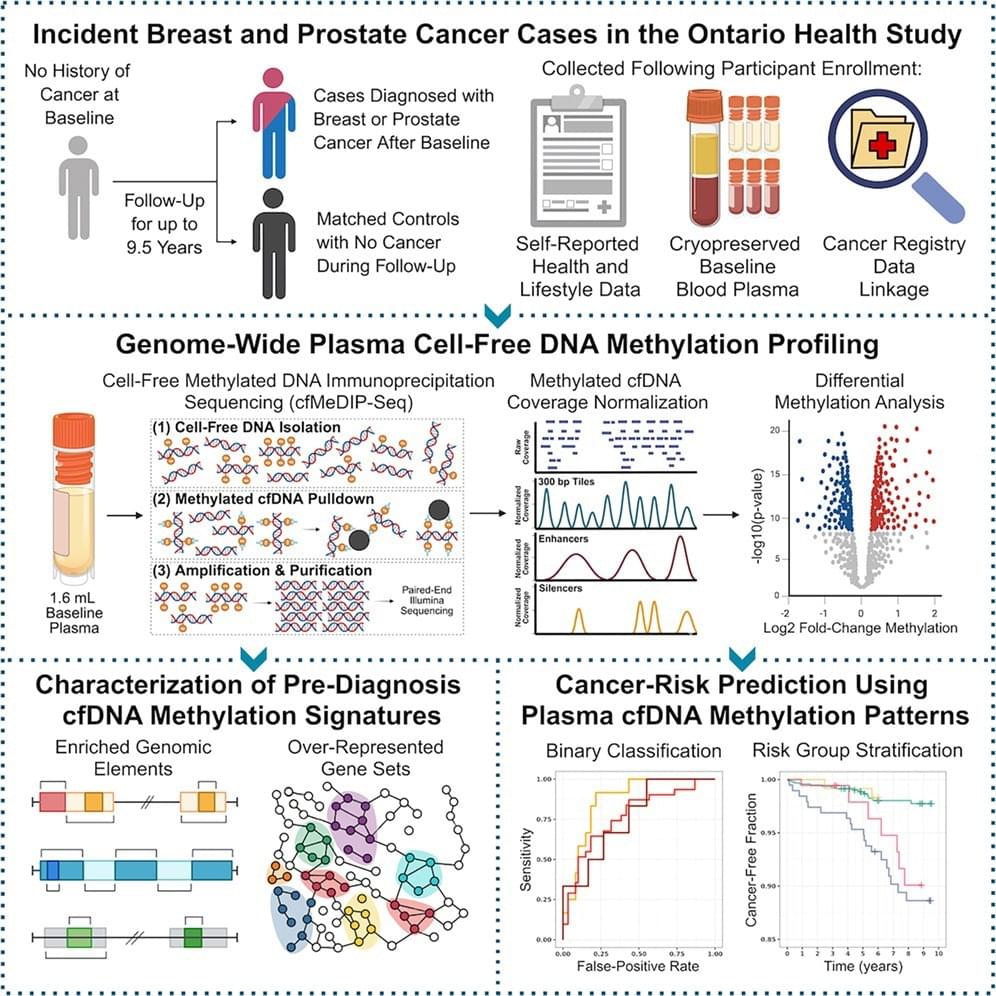
Cancer-related DNA changes may appear in blood years before diagnosis
Researchers found that genome-wide plasma cfDNA methylation profiles collected before diagnosis contained early molecular signatures associated with future prostate and breast cancer, with prostate silencer methylation providing the stronger risk stratification. Breast enhancer signals were weaker and varied by subtype and disease stage, indicating that cfDNA methylation may have greater value for risk assessment and surveillance than as a standalone diagnostic test.
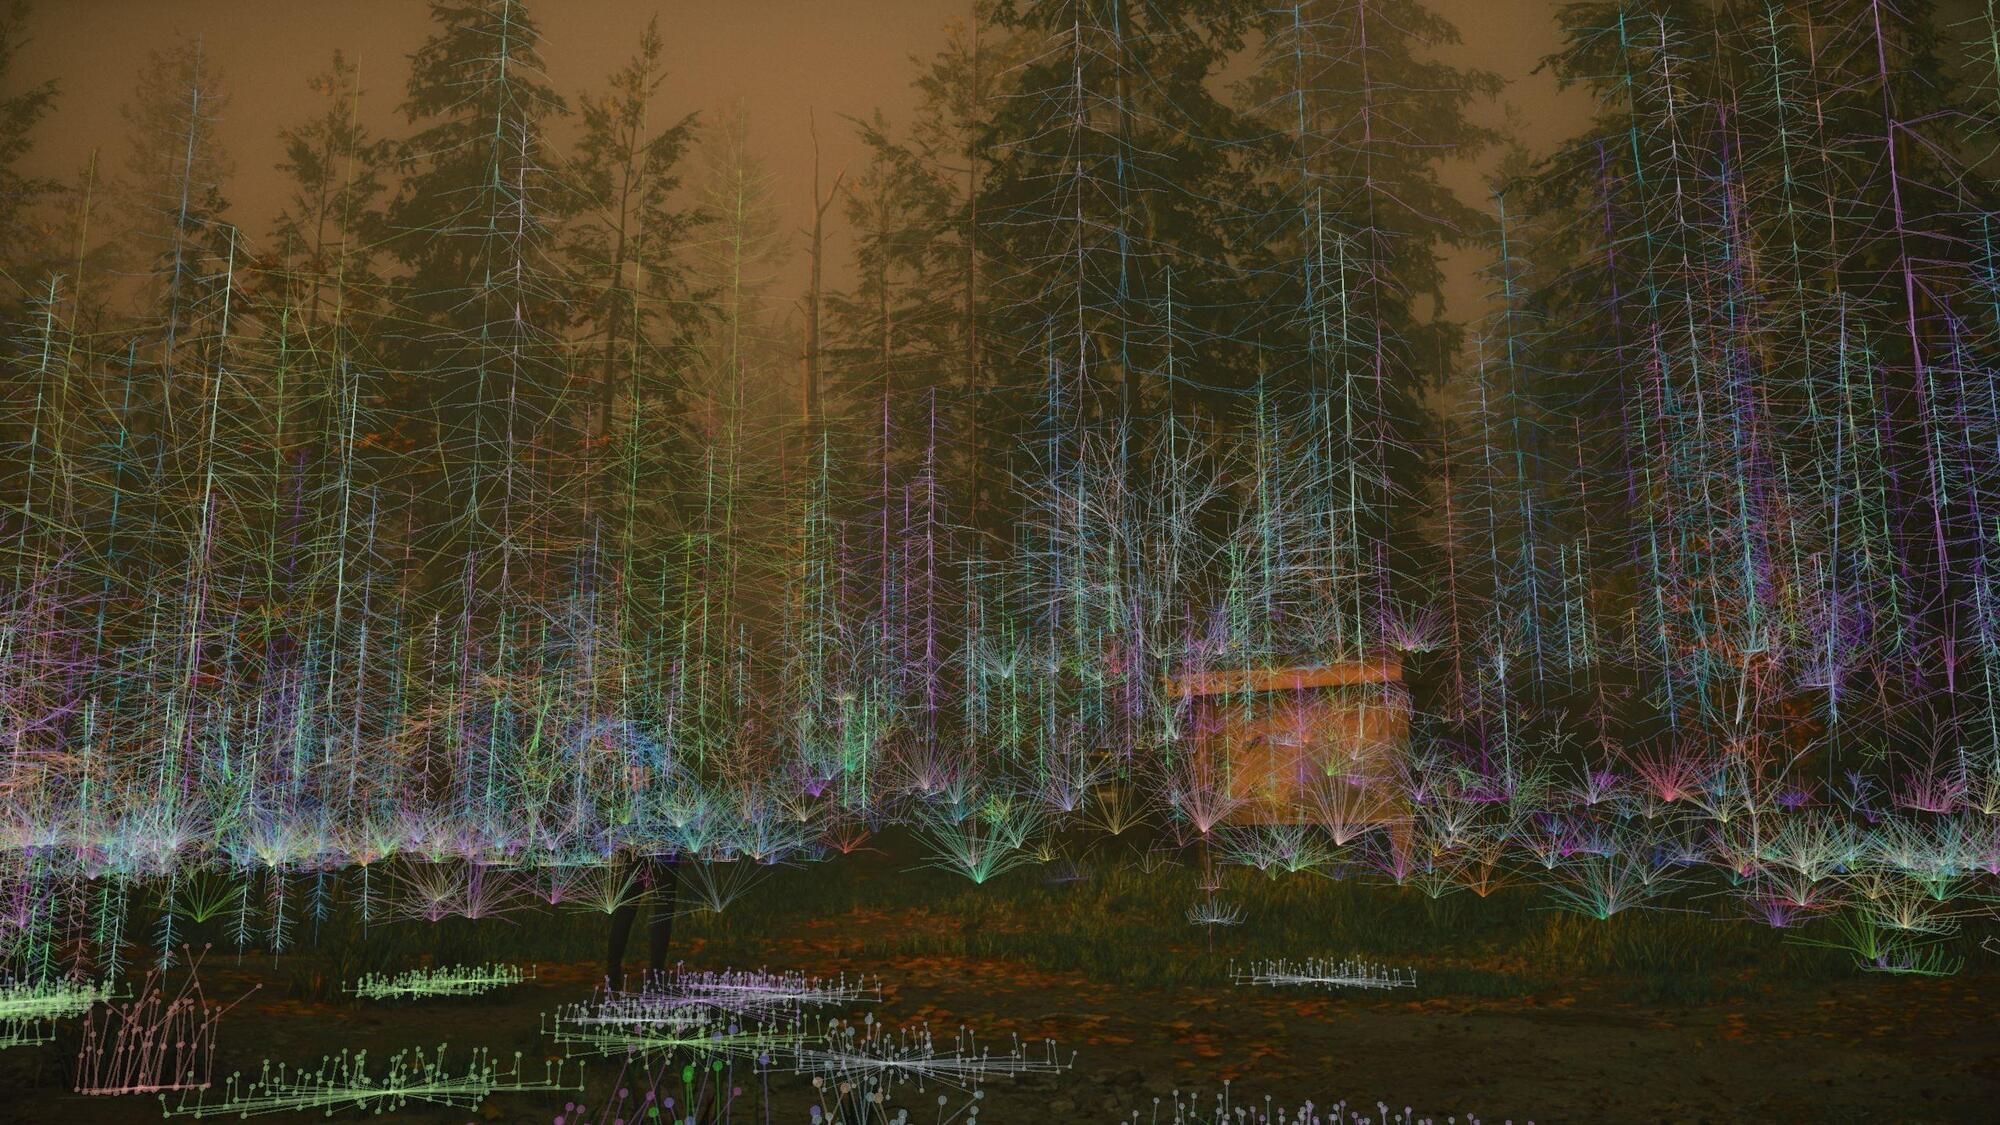
Touch grass? Not when AMD has whittled down ray tracing memory usage by 98% for these hardware-sapping bushes and trees
I don’t need to get out more.
WordPress Issues Patch for Critical Flaw That Can Enable Code Execution on Some Servers
WordPress fixes a critical unauthenticated path traversal flaw that can load local PHP files and, on some servers, enable code execution.
Convolution theorem (Laplace transformation)
Convolution theorem is important part of Laplace transformation.
Department of Microbial Infection and Immunity and
2Department of Microbiology, The Ohio State University, Columbus, Ohio, USA.
3Department of Microbiology and Immunology, Faculty of Pharmacy, Helwan University–Ain Helwan, Helwan, Egypt.