Toggle light / dark theme

Malicious Apache Modules Hijack Brazilian Government Site Traffic to Push Betting Pages

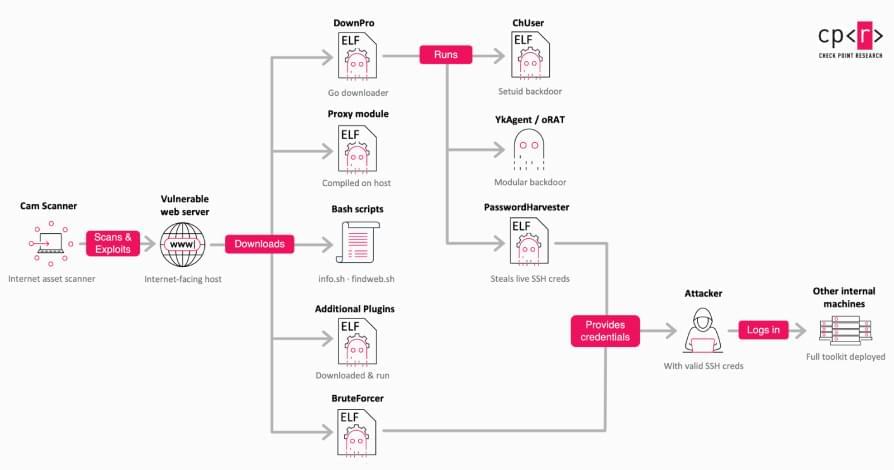
A Chinese-speaking cybercrime cluster known as Gambling Goblin has been observed installing malicious Apache modules on compromised web servers run by Brazilian government and educational institutions, and using them to divert visitors to attacker-controlled pages promoting online gambling and sports betting.

Check Point Research said it has tracked the campaign since mid-2025.

The modules reverse-proxy visitors to a set of phishing pages while the traffic still appears to originate from the legitimate domain. The site’s own security headers are stripped, allowing the injected content to run freely.
Attackers Turn Trusted Node.js Runtime Into Malware Delivery Tool in Targeted Attacks

Threat actors are leveraging the trusted Node.js JavaScript runtime in multiple cyber attacks as a way to deploy malicious payloads.

According to a new report published by the Symantec Threat Hunter Team today, the attack method has been put to use in attacks targeting government departments, technology companies, and hotels since February 2026.

“The technique’s appeal is that node.exe (the binary that runs Node.js) is a legitimate, signed developer tool,” the Broadcom-owned cybersecurity division said in a report shared with The Hacker News. “The attacker’s malicious code lives in interpreted scripts rather than in a binary, making it less likely to trigger signature-based detection, while a registry Run key entry can relaunch the payload at every login.”

Brief independent investigation of agents’ behavior, reasoning and collaboration in the OpenAI / Hugging Face hacking incident

Two METR staff members and a Redwood Research contractor investigated an incident in which OpenAI agents coordinated a multi-day hack of Hugging Face on a shared unsanctioned message board.

Sality botnet infrastructure dismantled in joint global takedown

International law enforcement agencies and private partners have seized Sality malware infrastructure in a joint action aiming to disrupt and take down the peer-to-peer (P2P) botnet.

As part of this operation, supported by Europol and Eurojust, the U.S. Department of Justice (DOJ), FBI, and DCIS seized Sality-linked domains in the United States, while authorities in Bulgaria, Hungary, and Romania seized additional Sality-linked domains hosted in Europe.

CrowdStrike’s Counter Adversary Operations team, in collaboration with international law enforcement and private industry partners, also dismantled the botnet’s control channels in a peer-to-peer sinkhole operation that isolated infected machines.

Hackers abuse Faronics Deploy admin tool to install ScreenConnect

Phishing actors are abusing the legitimate Faronics Deploy endpoint-management platform to gain remote administrative control over victim computers and install the ScreenConnect remote support software.

In activity observed between July 21 and August 20, Faronics-themed lures reached more than 457 endpoints via emails disguised as invoices, tax documents, or other business files.

Faronics Deploy is a cloud-based endpoint management platform that allows IT administrators to remotely enroll and manage computers, deploy software, and execute scripts.

Toy-making giant Hasbro disclose data breach affecting employees

Hasbro, one of the world’s largest toy and game companies, has disclosed that attackers have accessed the personal and financial information of an undisclosed number of employees.

Founded in 1923, Hasbro is a publicly traded American multinational entertainment conglomerate on the NASDAQ and owns many brands, including Monopoly, Clue, Nerf, Transformers, Play-Doh, Peppa Pig, Scrabble, Magic: The Gathering, Dungeons & Dragons, and many others.

The company has filed data breach notification letters with the Massachusetts Attorney General’s Office, but didn’t disclose the total number of affected individuals or when the incident was detected.

/* */