Silver Fox exploited a Microsoft-signed WatchDog driver in May 2025 to bypass defenses, deploy ValleyRAT, and enable fraud.
Category: cybercrime/malcode – Page 108

Lazarus Group Expands Malware Arsenal With PondRAT, ThemeForestRAT, and RemotePE
Lazarus Group used PondRAT, ThemeForestRAT, and RemotePE in a 2024 DeFi attack, likely via Chrome zero-day.
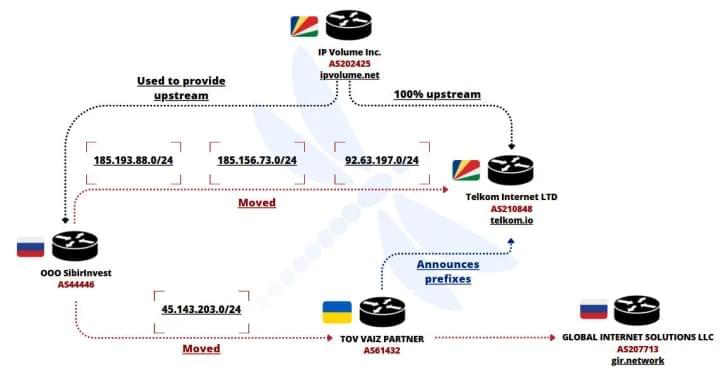
Ukrainian Network FDN3 Launches Massive Brute-Force Attacks on SSL VPN and RDP Devices
FDN3 brute-force attacks peaked July 6–8, 2025, tied to Seychelles bulletproof hosts enabling ransomware entry.

TransUnion suffers data breach impacting over 4.4 million people
Consumer credit reporting giant TransUnion warns it suffered a data breach exposing the personal information of over 4.4 million people in the United States, with BleepingComputer learning the data was stolen from it’s Salesforce account.

Amazon disrupts Russian APT29 hackers targeting Microsoft 365
Researchers have disrupted an operation attributed to the Russian state-sponsored threat group Midnight Blizzard, which sought access to Microsoft 365 accounts and data.
Also known as APT29, the hacker group compromised websites in a watering hole campaign to redirect selected targets “to malicious infrastructure designed to trick users into authorizing attacker-controlled devices through Microsoft’s device code authentication flow.”
The Midnight Blizzard threat actor has been linked to Russia’s Foreign Intelligence Service (SVR) and is well-known for its clever phishing methods that recently impacted European embassies, Hewlett Packard Enterprise, and TeamViewer.

ScarCruft Uses RokRAT Malware in Operation HanKook Phantom Targeting South Korean Academics
ScarCruft’s Operation HanKook Phantom uses RokRAT malware in spear-phishing campaigns, targeting South Korean academics for espionage.
Malicious npm Package nodejs-smtp Mimics Nodemailer, Targets Atomic and Exodus Wallets
Cybersecurity researchers have discovered a malicious npm package that comes with stealthy features to inject malicious code into desktop apps for cryptocurrency wallets like Atomic and Exodus on Windows systems.
The package, named nodejs-smtp, impersonates the legitimate email library nodemailer with an identical tagline, page styling, and README descriptions, attracting a total of 347 downloads since it was uploaded to the npm registry in April 2025 by a user named “nikotimon.” It’s currently no longer available.
“On import, the package uses Electron tooling to unpack Atomic Wallet’s app.asar, replace a vendor bundle with a malicious payload, repackage the application, and remove traces by deleting its working directory,” Socket researcher Kirill Boychenko said.

The Coming Inflection Point For Quantum Technology
In the not-too-distant future, quantum technology will become a disruptive force that has the capacity to rethink computers, cybersecurity, science, and data analytics
TamperedChef Malware Disguised as Fake PDF Editors Steals Credentials and Cookies
TamperedChef malware spread via fake PDF editors from June 26 to August 21, stealing credentials and cookies.

Researchers Find VS Code Flaw Allowing Attackers to Republish Deleted Extensions Under Same Names
VS Code flaw lets attackers reuse deleted extension names, enabling ransomware payload delivery and supply chain risks.