Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Fake LastPass Authenticator Installer Abuses Microsoft-Signed Driver to Kill Antivirus and EDR

A fake LastPass Authenticator installer offered on GitHub installs a Windows kernel driver that shuts off antivirus and other security software before a password stealer runs if a victim downloads and runs it, researchers at LastPass and Delphos Labs said on September 17.

Microsoft’s own hardware-compatibility program signs the driver, scored zero detections on VirusTotal when researchers checked it in August, and was not on Microsoft’s list of blocked drivers. LastPass says none of its own systems, services, or customer vaults were touched, and that the attackers only borrowed its name.

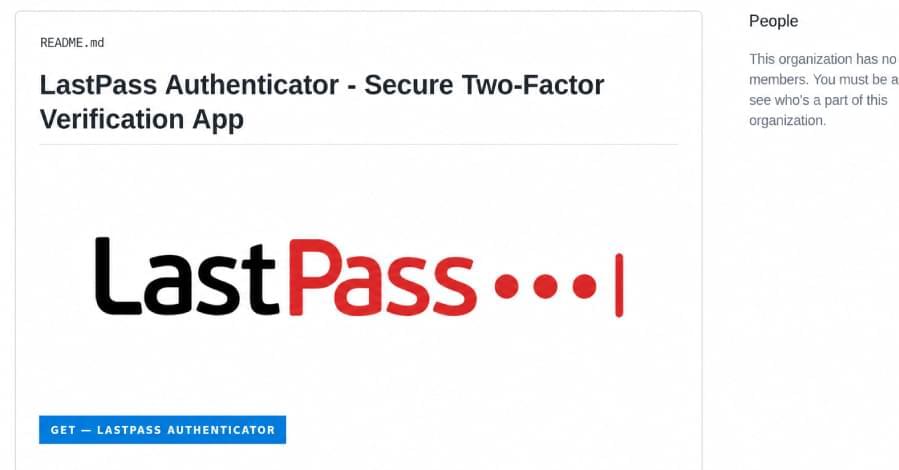
The lure is a fake GitHub page (github.com/LastPass-Authenticator) that ranks in search results for terms like “LastPass Authenticator download” and looks like a real LastPass product page.
Google Fined €403 Million Over GDPR Violations Tied to Location Data

Google has been fined €403 million for breaking the EU’s data protection law, the GDPR, in the way three of its features handled people’s location data from May 2018 to February 2020.

Ireland’s Data Protection Commission (DPC), Google’s lead regulator in the EU, also ordered the company to make its processing comply with the law within 6 months. The DPC has not said publicly which processing the order covers, and it says its full decision will be published later.

The three features are Web & App Activity, Location History and Location Accuracy.

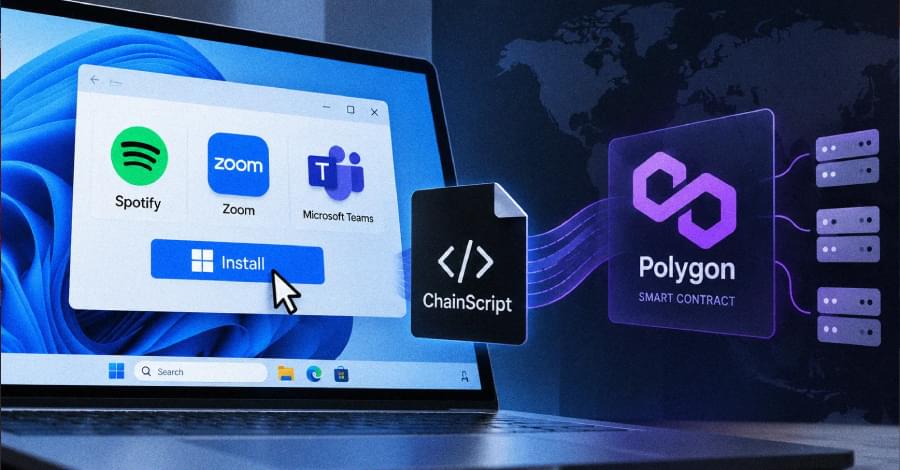
ClickFix Lures Deploy ChainScript RAT Using Polygon to Rotate C2 Infrastructure

The cybersecurity company described the activity as part of a broader pattern of attacks that employ trusted services and large language model (LLM) shared chats to serve fake installation instructions, while bypassing browser warnings, URL inspection, and Safe Browsing heuristics.

In a report published last month, Microsoft said it observed a macOS ClickFix campaign propagating MacSync and Atomic Stealer using a cluster of no less than 250 look-alike domains.

“The campaign evolved from broadly serving ClickFix lures to using a server-side browser-fingerprinting gate that shows the lure primarily to visitors whose environment appears consistent with a genuine macOS browser,” it said. “This cloaking limits visibility for crawlers, sandboxes, and some automated analysis workflows.”

Microsoft: September updates break File History backup feature

Microsoft warned that the built-in File History backup feature in Windows may stop working on some systems after installing the September 2026 security updates.

File History (introduced in Windows 8 and replaced by Windows Backup, which backs up data to OneDrive) automatically saves copies that let users recover accidentally deleted or damaged files using an older version from hours, days, or weeks ago.

By default, File History backs up all folders under the user’s account profile (Documents, Music, Pictures, Videos, and Desktop) to an external hard drive, such as a USB flash drive, or a network storage location (NAS).

WordPress Click2Shell flaw lets hackers execute PHP on the server

Technical details and a proof-of-concept exploit have been published for a new WordPress cross-site request forgery (CSRF) vulnerability dubbed ‘Click2Shell’ that affects the platform’s Core component.

The security problem does not have an official identifier but was addressed last week with the release of WordPress version 7.1.1.

It is a pre-authenticated remote code execution chain that allows an attacker to install any theme in the official WordPress.org catalog and run an arbitrary PHP file.

Microsoft to retire Microsoft 365 Companion apps in December

Microsoft announced that it will retire the Calendar, People, and Files Microsoft 365 companion apps on December 16 and urged admins to remove them from managed devices in their organization.

This follows Microsoft’s October 2025 announcement that it will begin automatically installing them on all Windows 11 enterprise devices with the Microsoft 365 desktop client apps by the end of December 2025.

The Microsoft 365 companion apps integrate Copilot for contextual AI assistance and can help locate people within the organization, access Microsoft 365 and locally stored files, and manage one’s schedule using the Microsoft 365 calendar from the Windows 11 taskbar.

Microsoft fixes broken Excel copy and paste for all Office users

Microsoft has fixed a known issue that causes copy-and-paste failures for Excel users after installing the September 2026 security updates.

The bug was confirmed following a wave of customer reports on Reddit and the Microsoft Q&A forums that this month’s updates (including the KB5002914 security update) break copy-and-paste, autofill, and formula dragging in Excel.

“In Microsoft Excel 2024, 2021, 2019, and 2016, as well as Excel Online in Office Online Server, the paste operation might fail silently,” Microsoft explains in a support document updated on Friday.

Microsoft reminds admins to migrate Entra ID users to passkeys

Microsoft has reminded administrators to migrate Entra ID users to phishing-resistant methods, such as passkeys, to avoid sign-in disruptions after it retires SMS first-factor sign-in starting in February 2027.

Admins also have alternatives, including QR code authentication, FIDO2 security keys, and other Entra ID-supported authentication methods.

Before this date, organizations should ensure all users use a phishing-resistant method because they will no longer be able to use SMS or voice to complete multifactor authentication and sign in to their accounts.

/* */