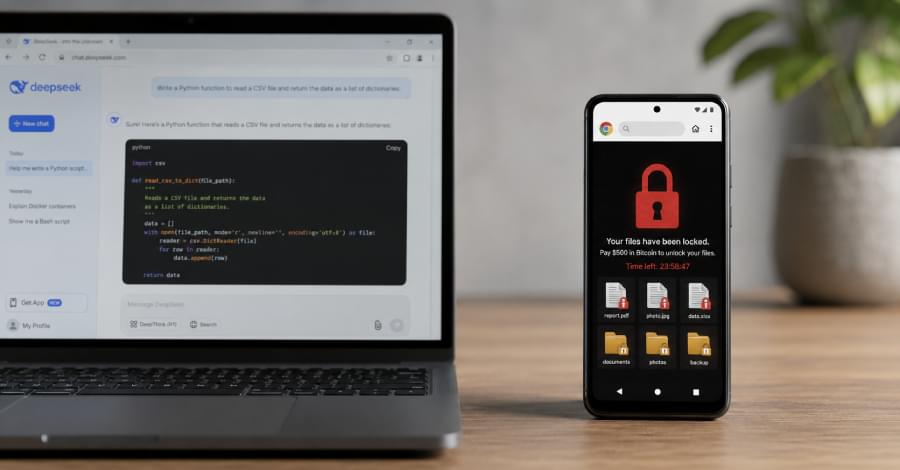
Uses Chromium’s File System Access API after user permission to encrypt files without a native payload or reported in-the-wild abuse
Category: cybercrime/malcode – Page 33
New ChocoPoC malware targets researchers via trojanized PoC exploits
Multiple weaponized proof-of-concept (PoC) exploits on GitHub were found delivering a Python-based remote access trojan (RAT) named ChocoPoC that can execute commands and steal sensitive data in a campaign believed to target cybersecurity researchers.
Hiding malware in PoC exploits for various vulnerabilities is not new, as there are examples of threat actors posing as real security researchers and taking advantage of trending vulnerabilities to target vulnerability and penetration testers or low-skilled hackers.
However, ChocoPoC stands out for not embedding the malware directly in the exploit file but for adding malicious Python packages to the PoC’s dependency list.
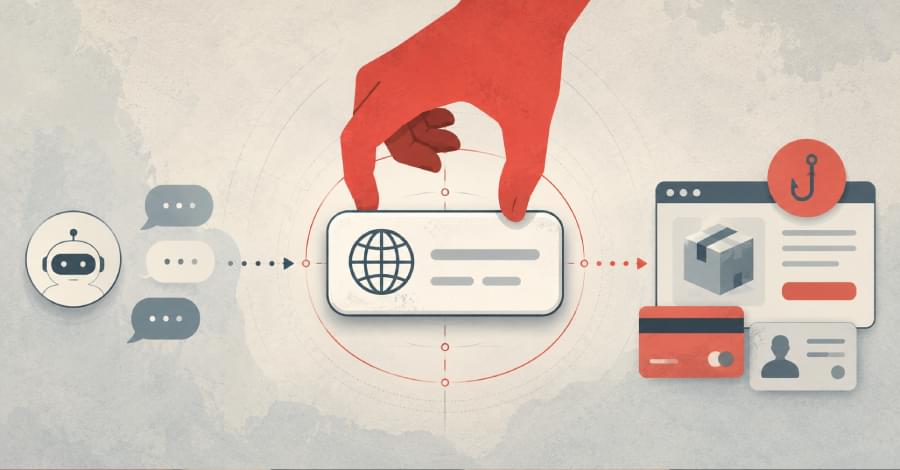
Phantom Squatting Uses AI-Hallucinated Domains for Phishing and Malware
Phantom squatting is the domain version of slopsquatting, where attackers register the fake software package names that AI coding tools invent. That is not a hypothetical.
A large USENIX study found code-generating models routinely suggest package names that do not exist, and the PhantomRaven campaign turned exactly that behavior into malware hidden in 126 npm packages with more than 86,000 installs.
It points to a larger shift: model output is becoming input. Developers, agents, and security teams act on AI-generated links and names before anyone verifies them, and AI keeps shrinking the time defenders have to react.
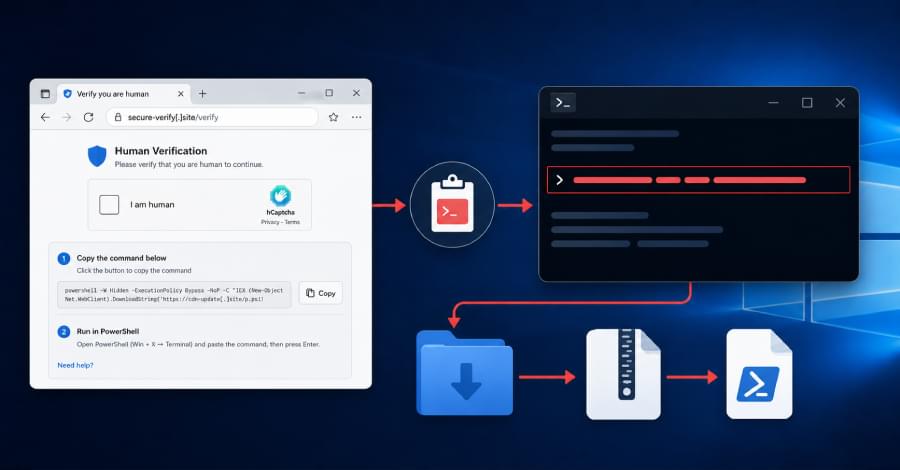
Researcher Analyzes 3,000 Live ClickFix Payloads, Exposing API-Driven Malware Delivery
Researcher analyzed 3,000 ClickFix payloads and found rotating wrappers plus a Downloads-folder method built to bypass AMSI.
RustDuck Botnet Rebuilds in Rust to Hijack Routers and Servers for DDoS
XLab says the two-stage botnet abuses weak Telnet/SSH logins, exposed ADB, and old flaws while shifting its core to Rust.
Private industry and government to completely abandon traditional cybersecurity postures
The threat landscape is no longer just malicious actors on keyboards. Attackers are accelerating their capabilities with agentic AI, automating attacks at scale, and creating zero-day exploits at unprecedented speeds.
University of Chicago Just Found a Shortcut Quantum Computers Needed for Years
University of Chicago researchers may have found the shortcut quantum computers have needed for decades.
In this video, we break down a major quantum computing breakthrough involving QLDPC error correction codes, reconfigurable atom arrays, and movable neutral atoms controlled by laser light. This new approach could reduce the number of physical qubits needed for practical fault-tolerant quantum computing by a factor of ten to twenty.
That matters because quantum computers have always faced one massive problem: qubits are extremely fragile. Traditional surface-code error correction can require thousands of physical qubits just to protect one reliable logical qubit, pushing useful quantum computers decades into the future. But this new blueprint could bring the requirement down from millions of qubits to tens of thousands.
We also explain why this discovery could affect medicine, drug discovery, encryption, post-quantum cybersecurity, climate technology, materials science, artificial intelligence, and the global race to build real quantum machines.
This is not a finished quantum computer yet. It is a credible engineering roadmap through one of the biggest bottlenecks in the field. But it may move practical quantum computing much closer than experts expected.
Watch the full video to understand why this University of Chicago breakthrough could change the quantum timeline.
China Has Matched Anthropic in Cybersecurity, Resetting AI Race
A clampdown on top U.S. AI is fueling concern that Washington is handing Beijing a cyberwarfare advantage.
AI can be an ally in rooting out ransomware threats
AI can be used to prevent cybersecurity threats linked to ransomware, says University of Cincinnati researcher Nelly Elsayed.
“We are in a hype era of AI,” says Elsayed, associate professor in the UC School of Information Technology. “Some people support it, others fear it, but in general people who design technology are trying to use it for good.”
Elsayed, founder and leader of the Applied Machine Learning and Intelligence Lab at UC, recently published research in the Journal of Information Security and Applications, arguing that generative AI may be an ally in strengthening ransomware defense.