Toggle light / dark theme

DNA origami turns secret messages into nano–Morse code that acts as multiplayer molecular encryption

Mathematics has always been at the core of securing information. From online banking to government communications, modern society relies on cryptography, in which complex mathematical algorithms transform readable information into an unreadable form to keep it secure. But as computing power grows and quantum technology advances, these mathematical safeguards are increasingly vulnerable to being broken. That’s where biology stepped in.

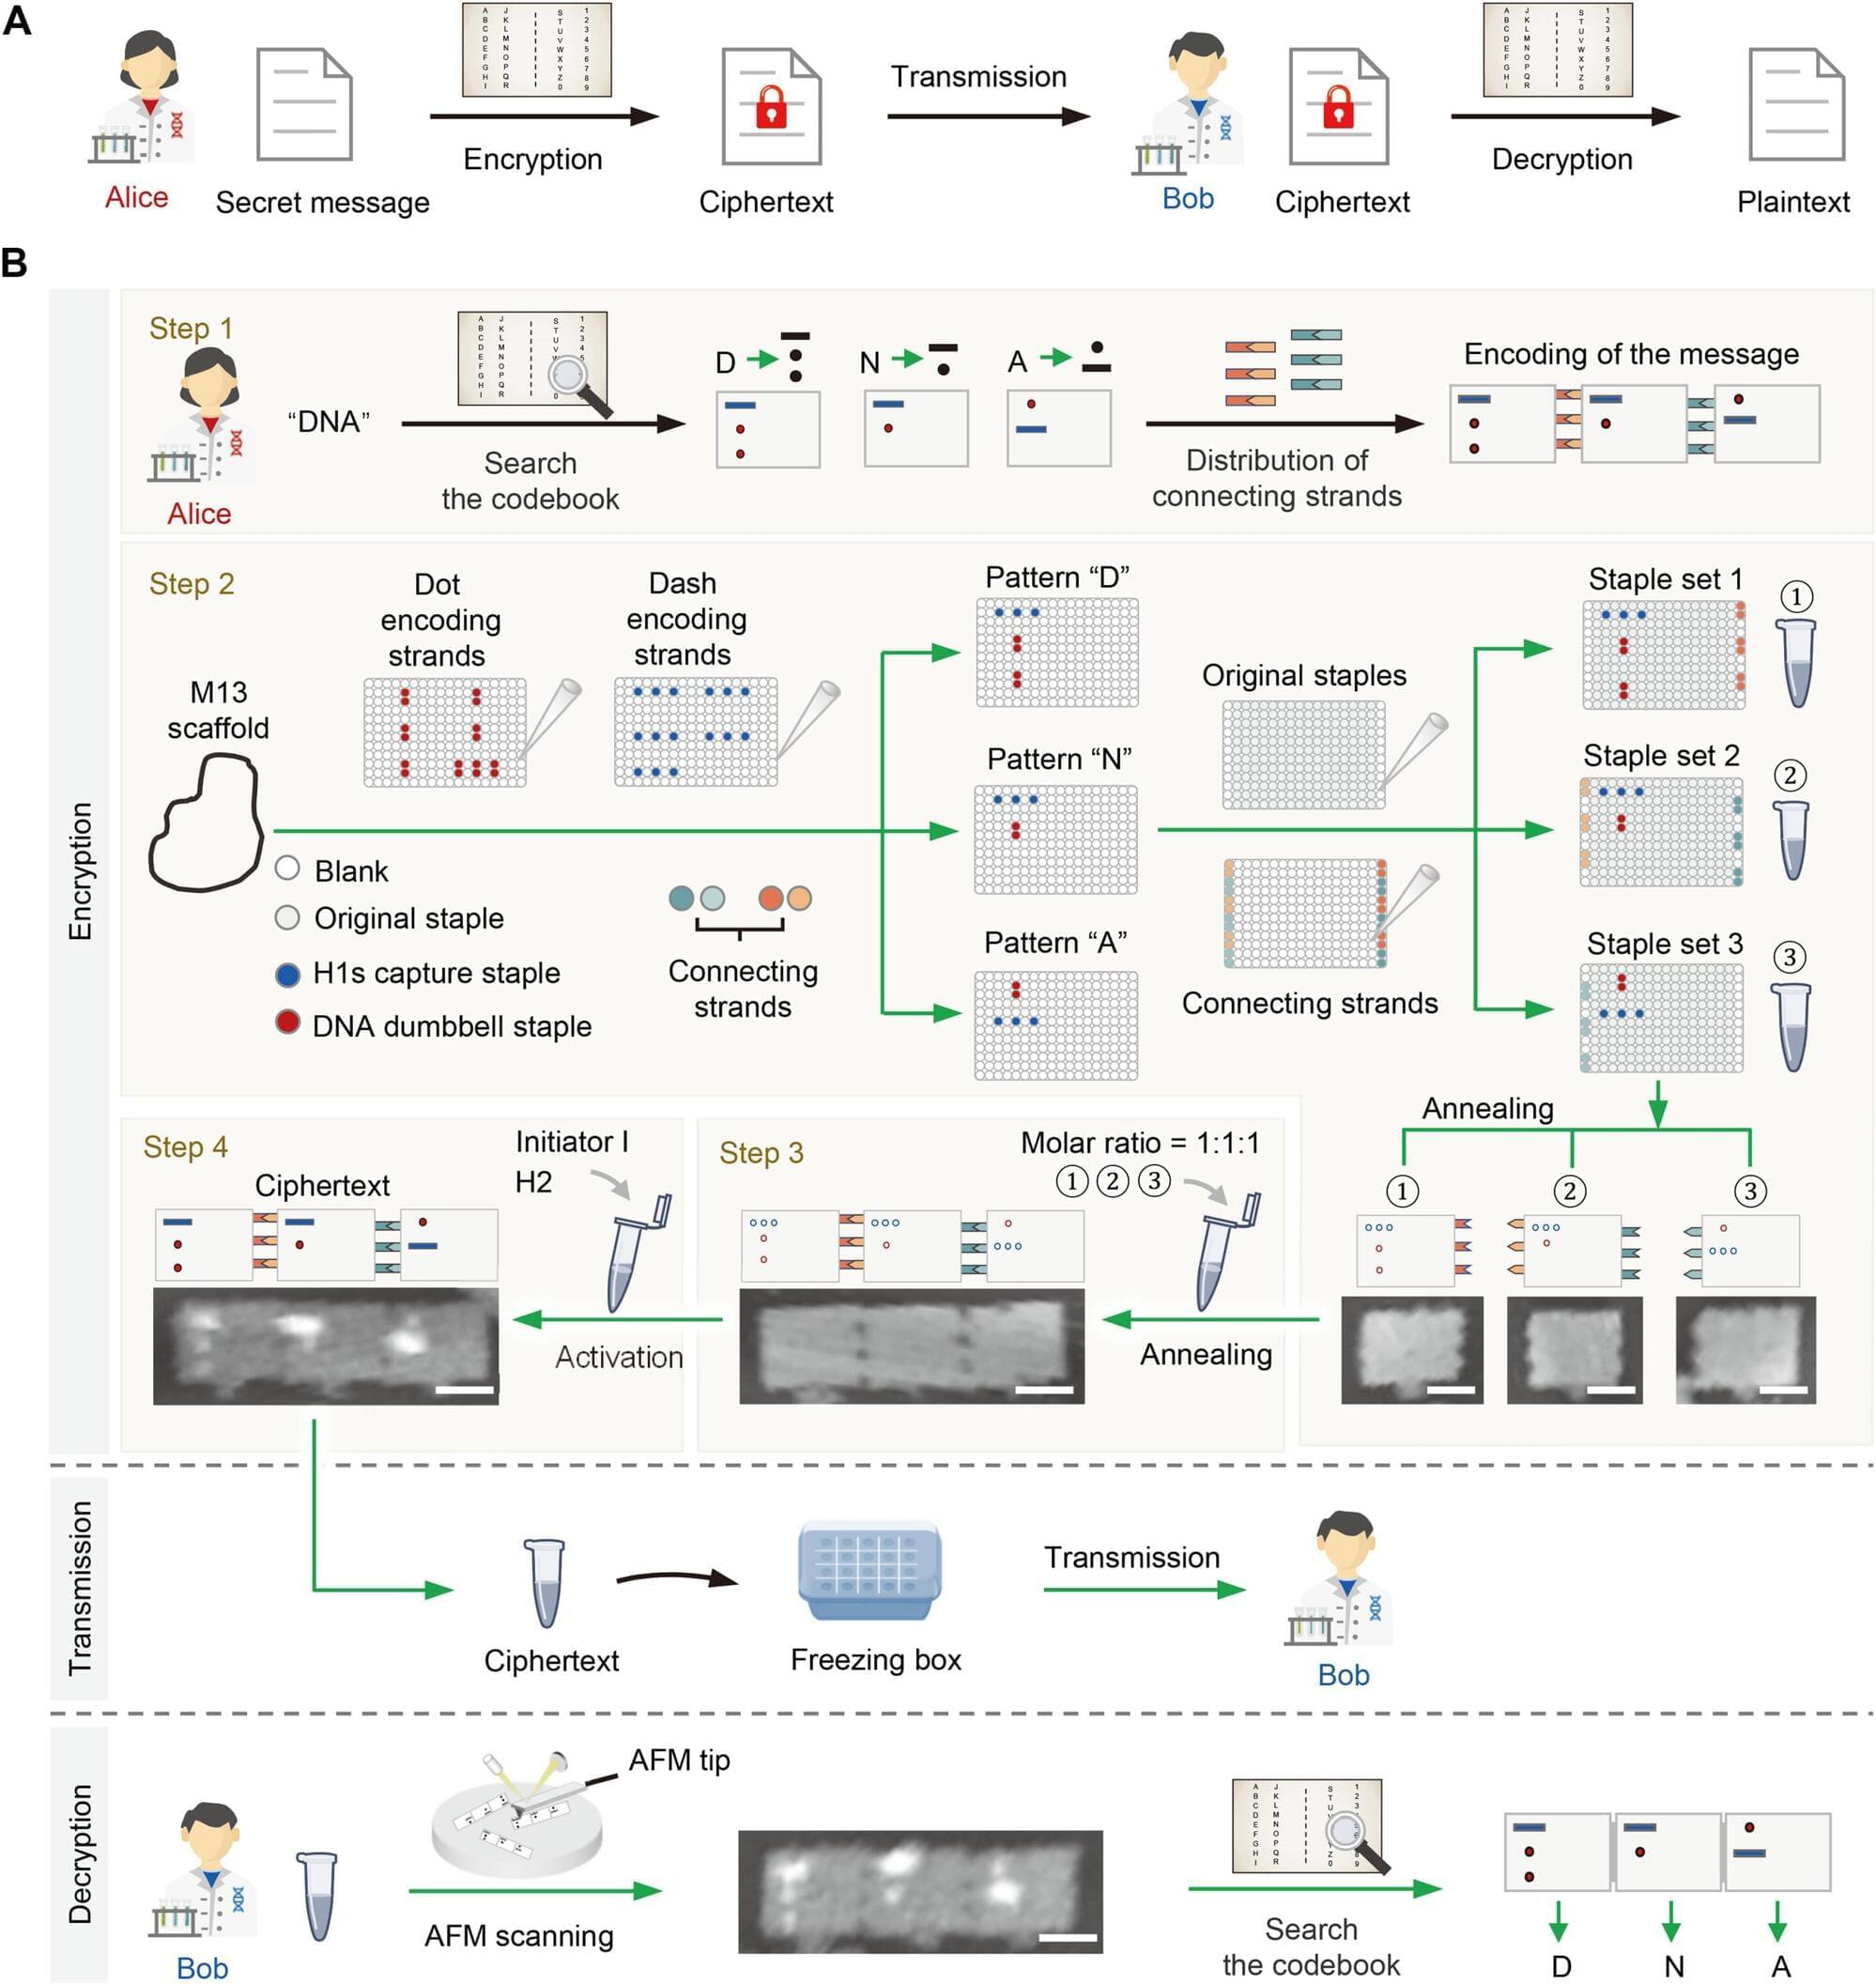
Choosing DNA as their information protector, researchers from China developed a multilayer encryption device that takes advantage of the double-helix molecule’s programmable nature to create an origami structure that can store information with high security.

This new system used tiny, custom-built rectangular structures made of DNA, in which researchers stored the message as dots and dashes, creating a nanoscale version of Morse code. To hide the message further, they turned the flat DNA origami surfaces into tubes, physically blocking the patterns from being read or imaged. With the help of a matching unlocking key, the recipient can trigger a reaction that unrolls the DNA back to its flat form, allowing them to read and verify the message.
Testing the limits of what’s possible (and what isn’t) with AI

When can we trust the results we get from AI, and when is learning impossible? Researchers have shown that there are some problems that even the most powerful AI cannot reliably solve, no matter how much data it is given.

The researchers, from the University of Cambridge and the University of California, Santa Barbara, designed “adversarial” mathematical systems to fool any AI algorithm. Like ethical hackers stress-testing a network’s security, these adversarial systems were designed to map out exactly where and why AI prediction breaks down.

Many real-world systems—like those in the oceans, the human brain or robotics—are too complex to describe neatly with equations, so researchers often learn how they behave by using machine learning. But these AI methods don’t always work well, returning unreliable results or poor predictions.

Google and Microsoft Pull ModHeader With 1.6 Million Installs After Dormant Collector Found

Google and Microsoft have pulled ModHeader, a popular header-editing extension with roughly 1.6 million installs across Chrome and Edge, after researchers found a hidden browsing-history collector built into its official store version.

The collector was dormant. An empty allow-list kept it switched off, and no proof has emerged that it ever gathered or sent a single browsing domain.

The analysis came from Stripe OLT, a UK security firm, which checked the code against Google’s own Web Store signature and confirmed the collector shipped inside the genuine extension, not a counterfeit.

The Future Will Be Shaped By Accelerated Technological Development And Visionary Leadership

Chuck Brooks is the president of Brooks Consulting International and one of Executive Mosaic’s GovCon Experts.

We are on the brink of a transformative era where rising technologies are colliding to create unparalleled innovation. artificial intelligence, nanotechnology and quantum technologies are transforming research and development, expediting prototyping and disrupting various industries.

This convergence, propelled by exponential processing power, molecular precision and intelligent systems, promises trillions in economic value while posing significant concerns in security, ethics and labor preparedness.

Microsoft expects more Windows security updates from AI-discovered flaws

Microsoft says Windows users should expect to see an increase in security updates as the company increasingly relies on artificial intelligence to discover vulnerabilities in its codebase.

In a blog post published today, Microsoft said advances in AI have significantly accelerated vulnerability discovery, allowing engineers to identify more security issues before they can be exploited in zero-day attacks.

“The pace of vulnerability discovery is changing with advances in AI making it possible to find more issues, faster, across more code, with new mechanisms that can accelerate both discovery and analysis,” Microsoft said.

Entra passkey enrollment vishing targets Microsoft 365 users

A threat actor has been targeting organizations across multiple sectors with voice-based fake security requests that ask Microsoft 365 users to enroll a new Entra passkey.

The attacker is taking advantage of a new capability Microsoft opened to administrators in May, allowing them to run “passkey registration campaigns” to entice users to enrol passkeys for more secure authentication.

The campaign has been running since April and involves calling targeted users and trying to convince them to register a new passkey under the attacker’s control.

Accenture confirms breach after hacker offers stolen data for sale

IT services giant Accenture has confirmed it suffered a security breach after a threat actor claimed to have stolen 35 GB of source code and other data from the company.

“We are aware of this isolated matter, and we have remediated its source. There is no impact to Accenture operations and service delivery,” Accenture told BleepingComputer.

Accenture is a global professional services company that provides consulting, technology, cloud, engineering, and managed services to businesses and governments worldwide.