
UNC5142 exploits blockchain smart contracts and WordPress flaws to deliver stealer malware worldwide.
Category: cybercrime/malcode – Page 94

Air Force asks industry for digital signal processing and cyber security for signals intelligence (SIGINT)
Technology areas include electronic intelligence; autonomous processing; and new ways of blending cyber security and signals intelligence.
Chinese Threat Group ‘Jewelbug’ Quietly Infiltrated Russian IT Network for Months
Chinese group Jewelbug hacked a Russian IT provider, exploiting Microsoft tools and exfiltrating data via Yandex Cloud.

Over 100 VS Code Extensions Exposed Developers to Hidden Supply Chain Risks
Wiz exposed 550 leaked secrets in VS Code extensions, as TigerJack exploits marketplaces with malware.
Chinese Hackers Exploit ArcGIS Server as Backdoor for Over a Year
“This attack highlights not just the creativity and sophistication of attackers but also the danger of trusted system functionality being weaponized to evade traditional detection,” the researchers noted. “It’s not just about spotting malicious activity; it’s about recognizing how legitimate tools and processes can be manipulated and turned against you.”
ReliaQuest told The Hacker News it cannot share any further details regarding when the attack commenced other than noting that the attackers had access to the system for over a year.
“The threat actor likely resorted to this method over an N-day flaw for a simple reason: why use an exploit if they didn’t have to?,” it pointed out. “They likely gained initial access through a weak administrator password and then repurposed a software component into a backdoor.”
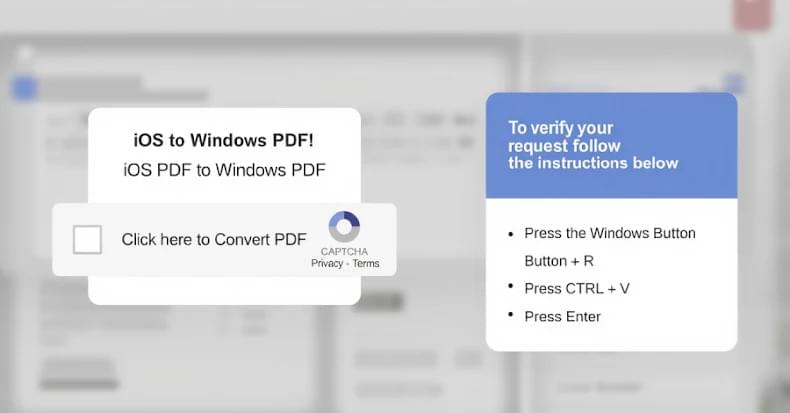
Researchers Expose TA585’s MonsterV2 Malware Capabilities and Attack Chain
Researchers link TA585 to MonsterV2 RAT stealer delivered via IRS-themed phishing, JavaScript injects, and GitHub lures.
Microsoft Warns of ‘Payroll Pirates’ Hijacking HR SaaS Accounts to Steal Employee Salaries
Storm-2657 exploits phishing and weak MFA to hijack HR SaaS accounts and redirect payroll funds.
Researchers Warn RondoDox Botnet is Weaponizing Over 50 Flaws Across 30+ Vendors
RondoDox expands to exploit 56 flaws across 30 vendors, fueling global IoT botnet attacks.
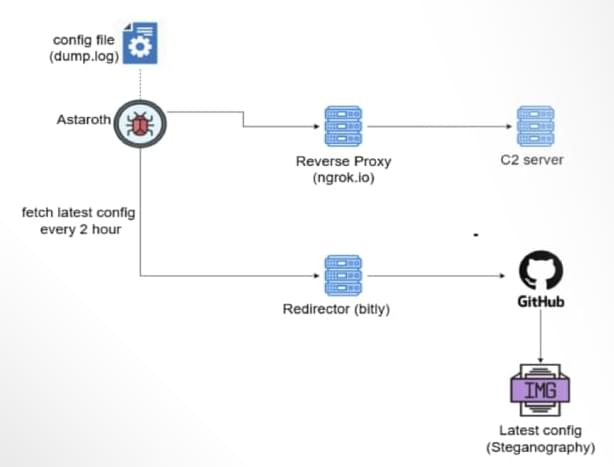
Astaroth Banking Trojan Abuses GitHub to Remain Operational After Takedowns
Cybersecurity researchers are calling attention to a new campaign that delivers the Astaroth banking trojan that employs GitHub as a backbone for its operations to stay resilient in the face of infrastructure takedowns.
“Instead of relying solely on traditional command-and-control (C2) servers that can be taken down, these attackers are leveraging GitHub repositories to host malware configurations,” McAfee Labs researchers Harshil Patel and Prabudh Chakravorty said in a report.
“When law enforcement or security researchers shut down their C2 infrastructure, Astaroth simply pulls fresh configurations from GitHub and keeps running.”
New Rust-Based Malware “ChaosBot” Uses Discord Channels to Control Victims’ PCs
Rust-based ChaosBot exploits Discord and phishing to infiltrate networks, while Chaos-C++ adds data destruction.