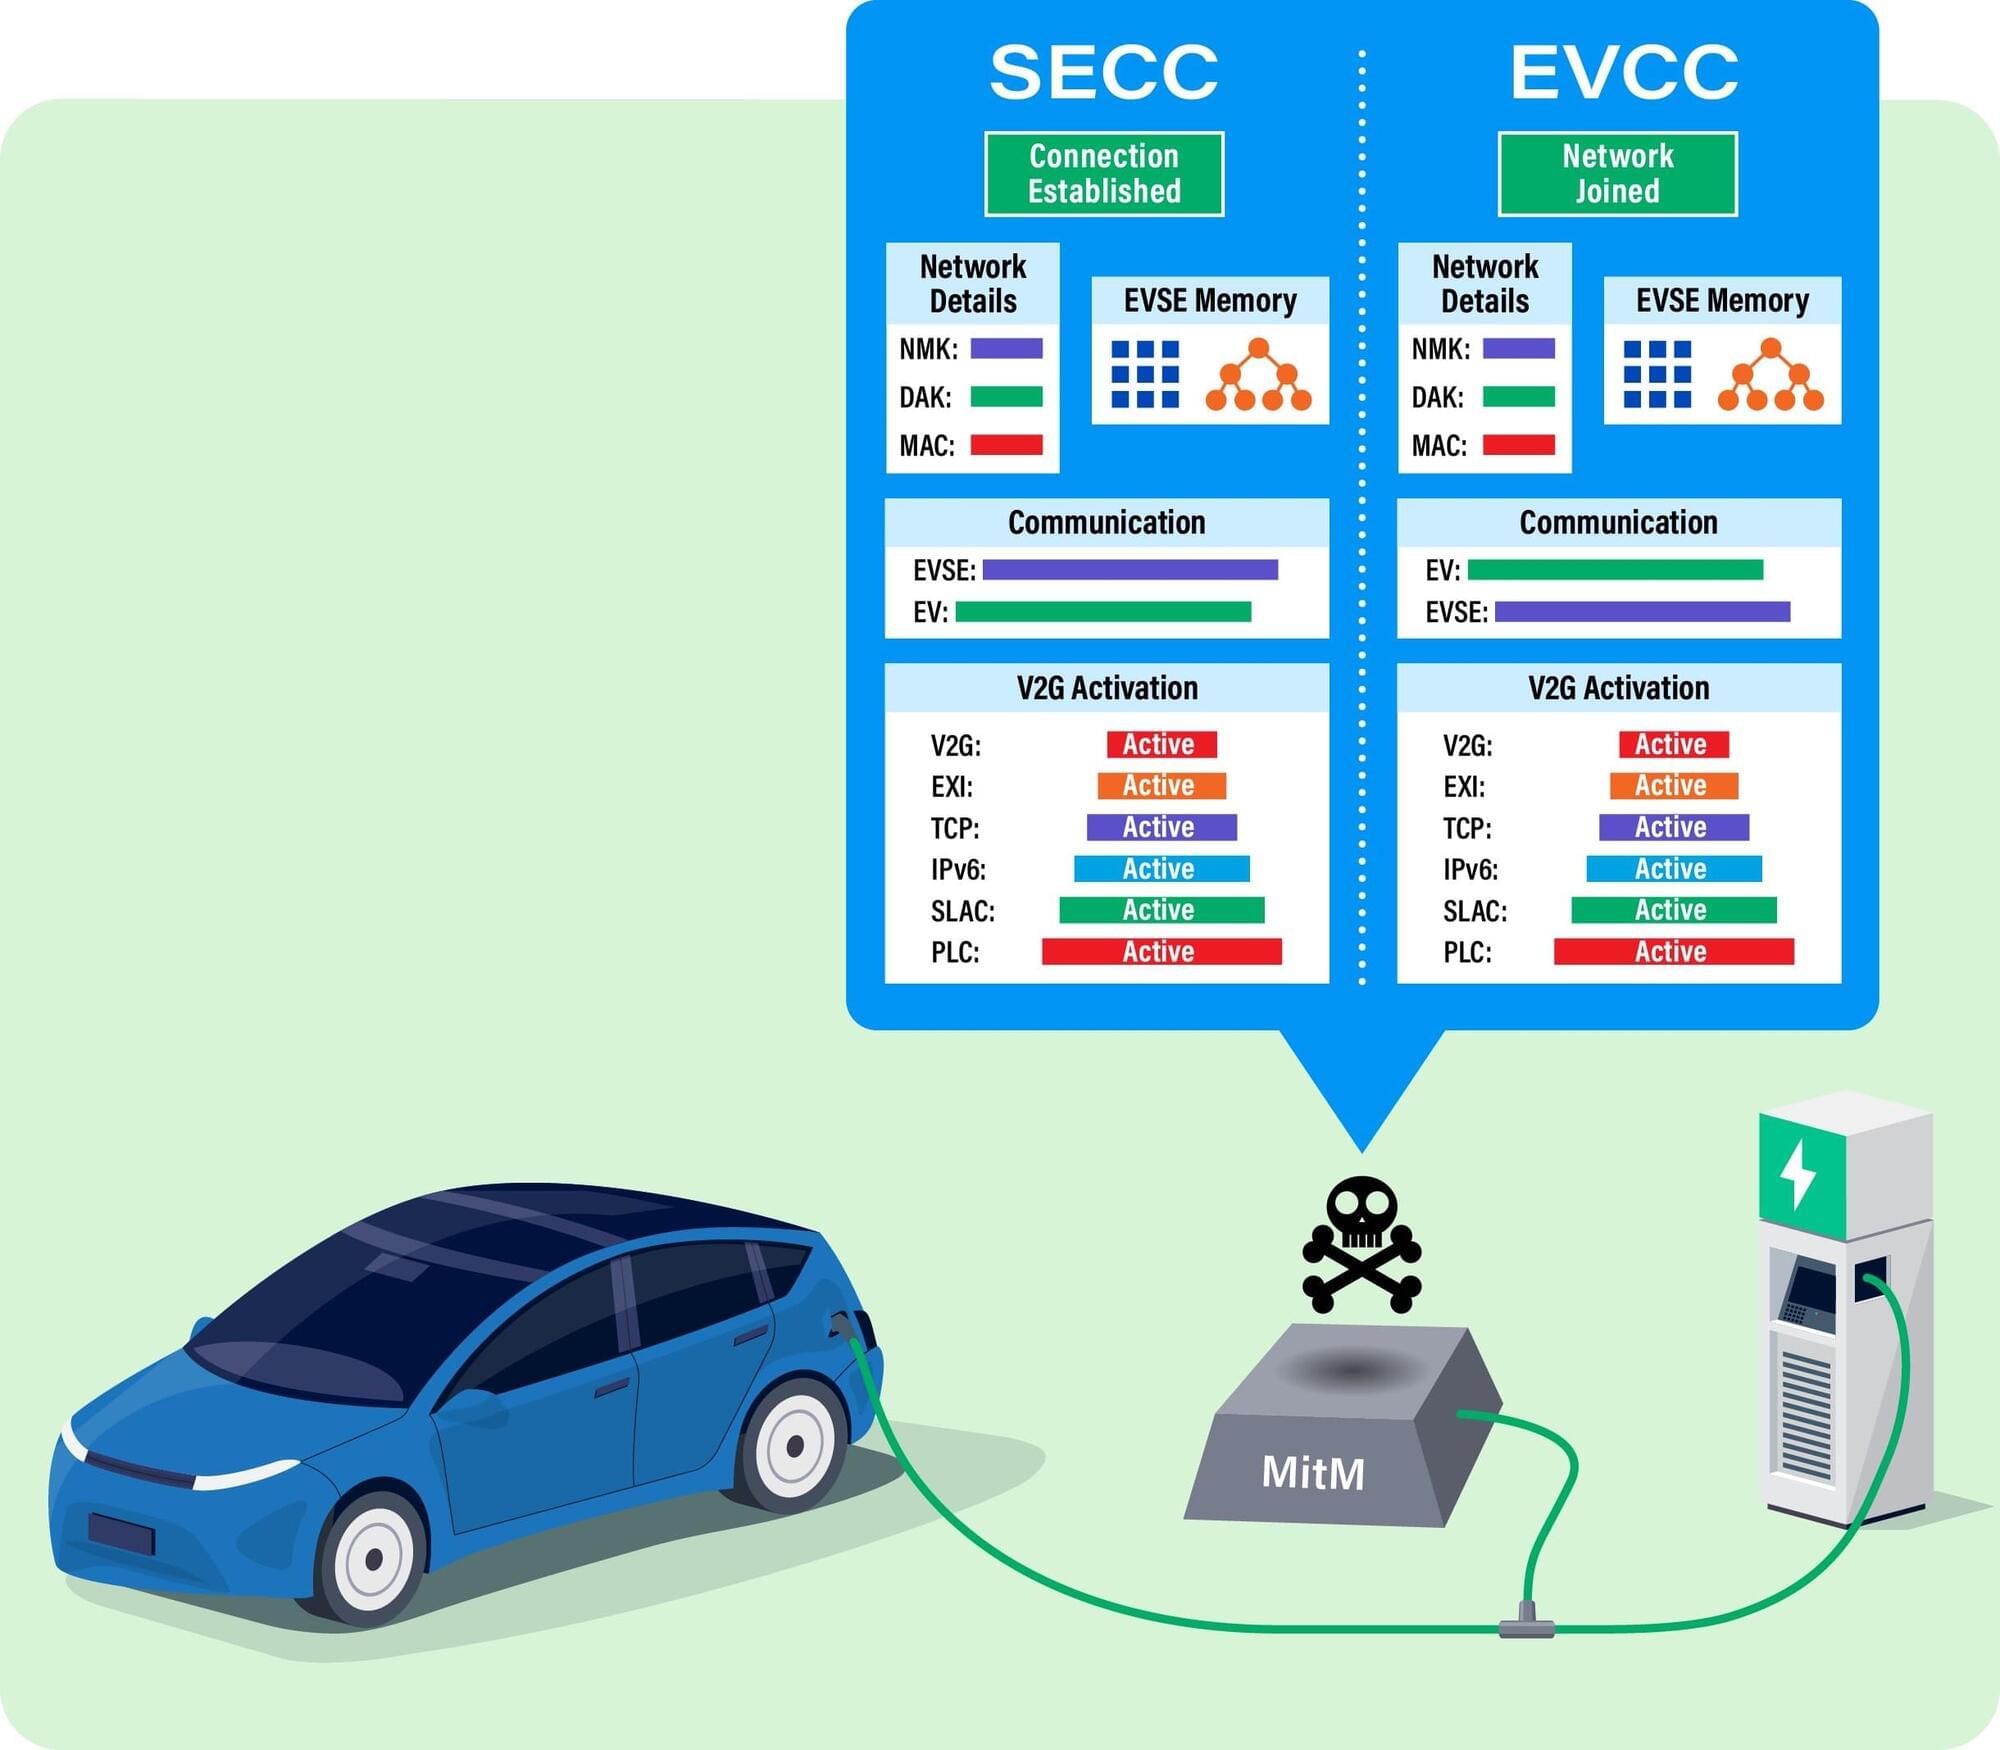
Southwest Research Institute identified a security vulnerability in a standard protocol governing communications between electric vehicles (EV) and EV charging equipment. The research prompted the Cybersecurity & Infrastructure Security Agency (CISA) to issue a security advisory related to the ISO 15118 vehicle-to-grid communications standard.
Category: cybercrime/malcode – Page 88

RondoDox Exploits Unpatched XWiki Servers to Pull More Devices Into Its Botnet
RondoDox targets unpatched XWiki servers via CVE-2025–24893, driving record exploitation surges in November.

Decades-old ‘Finger’ protocol abused in ClickFix malware attacks
The decades-old “finger” command is making a comeback„ with threat actors using the protocol to retrieve remote commands to execute on Windows devices.
In the past, people used the finger command to look up information about local and remote users on Unix and Linux systems via the Finger protocol, a command later added to Windows. While still supported, it’s rarely used today compared to its popularity decades ago.
When executed, the finger command returns basic information about a user, including their login name, name (if set in /etc/passwd), home directory, phone numbers, last seen, and other details.
Invasive Israeli-founded bloatware is harvesting data from Samsung users in WANA
IronSource Expands Samsung Partnership, Launching on Samsung Mobile Devices in MENA https://www.businesswire.com/news/home/20221103005106/en/iro…es-in-MENA
Across West Asia and North Africa (WANA), growing concerns about digital surveillance have placed Israeli cybersecurity firms and their software under intense scrutiny. Among the most alarming cases is AppCloud, a pre-installed application on Samsung’s A and M series smartphones.
The bloatware cannot be uninstalled easily because it runs on the device’s operating system. Uninstalling it requires root access (the highest level of control in a computer system) of the phone to remove the AppCloud package. Its privacy policy is nowhere to be found online and opting out is not always available.
But the real concern lies in who owns AppCloud. When investigating further, we discovered that AppCloud’s privacy policy can be traced back to the controversial Israeli-founded company ironSource (now owned by the American company Unity). ironSource is notorious for its questionable practices regarding user consent and data privacy.

Ransomware’s Fragmentation Reaches a Breaking Point While LockBit Returns
Ransomware hit record highs in Q3 2025 with 85 active groups and LockBit 5.0’s return.
North Korean Hackers Turn JSON Services into Covert Malware Delivery Channels
North Korean hackers exploit JSON storage services to deploy malware in Contagious Interview attacks.
Iranian Hackers Launch ‘SpearSpecter’ Spy Operation on Defense & Government Targets
Iran’s APT42 launches SpearSpecter campaign using TAMECAT malware, targeting defense and government officials.
Google backpedals on new Android developer registration rules
Google is backpedaling on its decision to introduce new identity verification rules for all developers, stating that it will also introduce accounts for limited app distribution and will allow users to install apps from unverified devs.
As announced in August, Google was planning to introduce what it called “Developer Verification” starting in 2026 to block malware spreading via sideloaded apps sourced from outside the official Google Play app store.
The new rules require that all apps must originate from developers with verified identities to be installed on certified Android devices; otherwise, their installation will be blocked.
Anthropic claims of Claude AI-automated cyberattacks met with doubt
Anthropic reports that a Chinese state-sponsored threat group, tracked as GTG-1002, carried out a cyber-espionage operation that was largely automated through the abuse of the company’s Claude Code AI model.
However, Anthropic’s claims immediately sparked widespread skepticism, with security researchers and AI practitioners calling the report “made up” or the company of overstating the incident.
“I agree with Jeremy Kirk’s assessment of the Anthropic’s GenAI report. It’s odd. Their prior one was, too,” cybersecurity expert Kevin Beaumont posted on Mastodon.
Logitech confirms data breach after Clop extortion attack
Hardware accessory giant Logitech has confirmed it suffered a data breach in a cyberattack claimed by the Clop extortion gang, which conducted Oracle E-Business Suite data theft attacks in July.
Logitech International S.A. is a Swiss multinational electronics company that sells hardware and software solutions, including computer peripherals, gaming, video collaboration, music, and smart home products.
Today, Logitech filed a Form 8-K with the U.S. Securities and Exchange Commission, confirming that data was stolen in a breach.