Artificial intelligence is not simply another chapter in the history of technology. It is becoming the cognitive infrastructure of modern civilization. Like electricity transformed the Industrial Age and the Internet transformed the Information Age, AI will define the Intelligence Age. Its true power will not come from replacing people, but from amplifying human ingenuity through the convergence of computing, cybersecurity, robotics, quantum science, biotechnology, and human creativity. The future will belong to societies that innovate boldly, secure wisely, govern responsibly, and never lose sight of the fact that technology should ultimately serve humanity—not the other way around.
Category: cybercrime/malcode – Page 22
The US Robot Import Ban Doesn’t Stop China — It Redirects It
The FCC just banned new foreign-made humanoid robots and robot dogs, citing cybersecurity risks. With China holding ~85% of the global humanoid market, this is effectively a China ban.
But the ban only closes the US market. Chinese manufacturers’ production capacity and export ambition remain intact. The real result is intensified sales pressure on Southeast Asia, Africa, and other open markets — with more aggressive pricing and Robot-as-a-Service deals.
For buyers outside the US, this creates short-term opportunities… and the same data-dependency risks US regulators just cited as the reason for the ban.
Full analysis: [ https://creedtec.online/the-us-robot-import-ban-doesnt-stop-…irects-it/](https://creedtec.online/the-us-robot-import-ban-doesnt-stop-…irects-it/)
#HumanoidRobots #IndustrialRobotics #China #TradePolicy
The US import ban on Chinese robots may reshape global markets, redirecting exports toward Africa and Southeast Asia instead of stopping them.
Computer scientists design a cyberattack to prevent cyberattacks
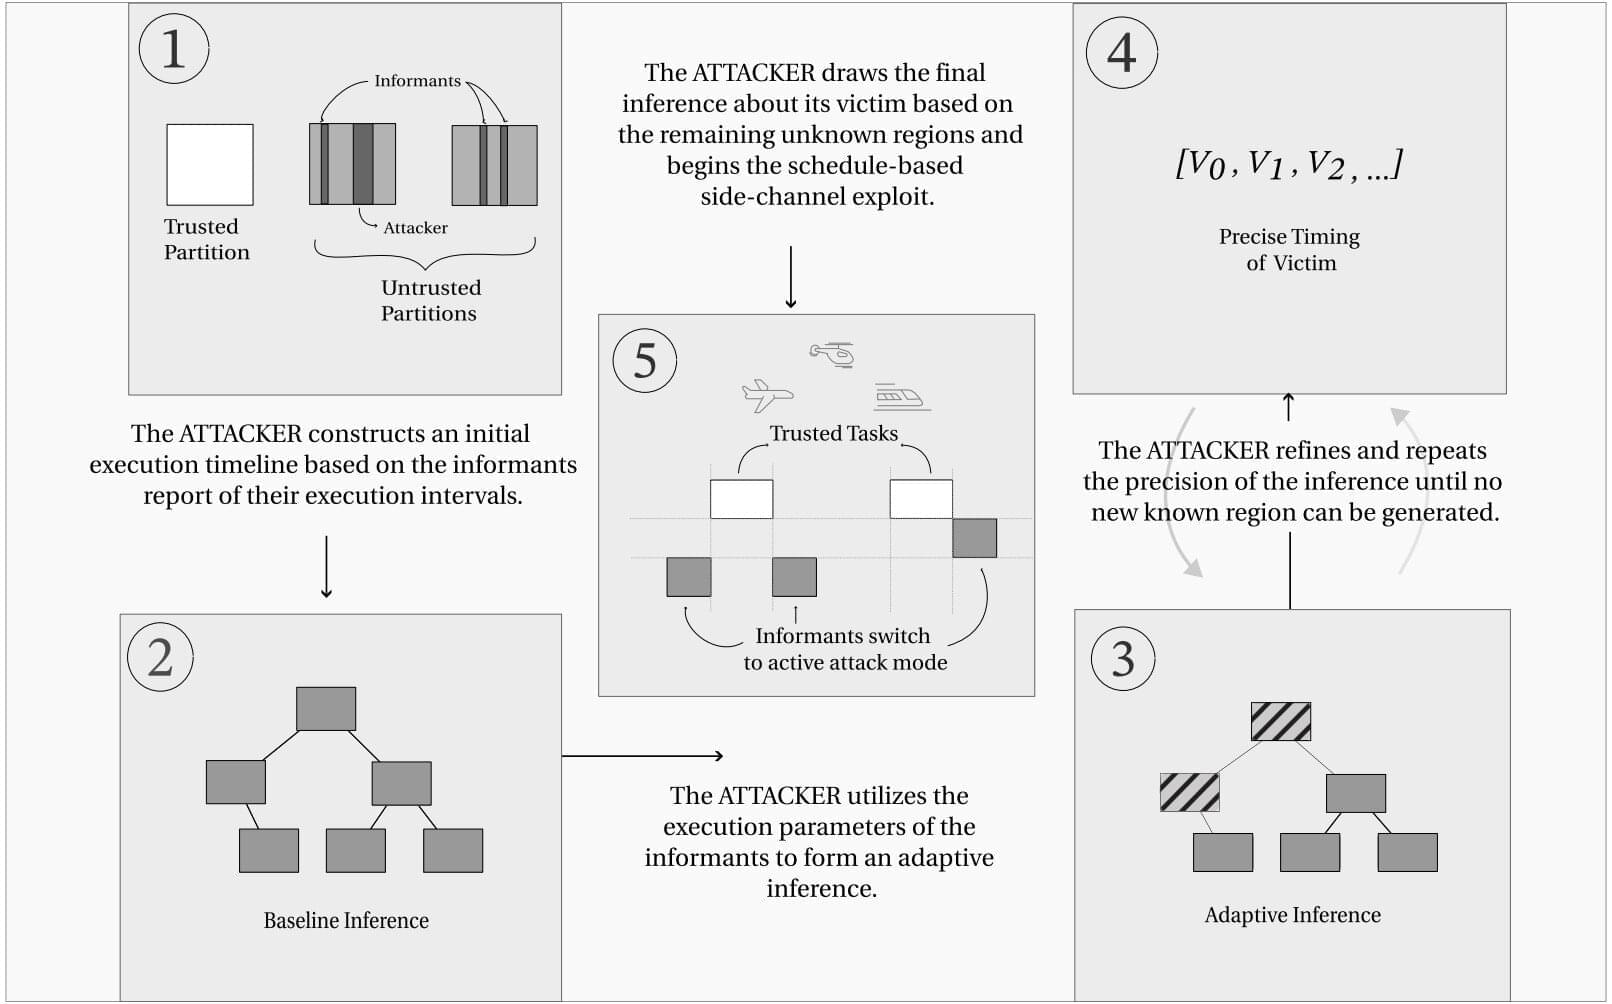
Protecting sensitive, precision-timed computing systems requires understanding the nature of cyberthreats. So researchers from Washington State University teamed up with experts at the University of Colorado Colorado Springs and Metro State University to design an attack—dubbed NosyNeighbor—that lurks on the sidelines of time- and safety-critical computer systems, “infers” what’s happening inside and adapts its malicious approach.
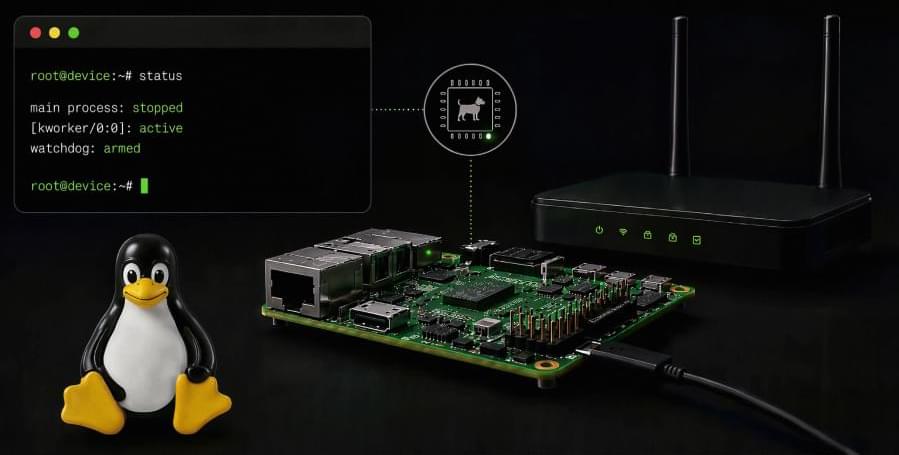
Tengu Botnet Reboots Compromised Linux Devices When Defenders Kill Its Process
Tengu abuses Linux hardware watchdogs to reboot devices after its main process is killed, letting other persistence mechanisms relaunch it.
Nimbus Manticore Deploys NightLedger and Turns Victim Systems Into Covert Relays
The Iranian state-backed hacking group tracked as Nimbus Manticore (aka GalaxyGato, Mirage Kitten, Smoke Sandstorm, Subtle Snail, and UNC1549) has been attributed to a fresh set of attacks targeting entities across the Middle East, Africa, and South Asia.
The intrusions involve the use of a previously undocumented Windows backdoor called NightLedger and two custom WebSocket tunnelers, BridgeHead and ArcBridge, with an aim to maintain covert access.
Targets of the campaign include Egypt, SMB and government environments in Jordan and Tanzania, aviation organizations in Pakistan, telecommunication companies in Ethiopia, and financial-sector entities in Burkina Faso, per Kaspersky.
CubePilot drone software dev hit by DNS hijacking to intercept traffic
CubePilot, an Australian firm that designs flight controllers for drones (UAVs), announced a severe operational disruption caused by a DNS hijacking attack.
Hijacking domain name system (DNS) records allows threat actors to redirect users to their infrastructure, diverting traffic intended for a legitimate service. This exposes users to dangerous scenarios such as sensitive data interception, malware delivery, and phishing.
According to a status update published on CubePilot’s website, an attacker gained control of the cubepilot[.]org domain DNS settings on July 24, allowing them to intercept traffic intended for internal systems.
Microsoft touts costsaving AI model for cybersecurity
Microsoft says that when integrated with OpenAI’s GPT-5.4, its new cybersecurity model can beat Anthropic’s new Mythos 5.
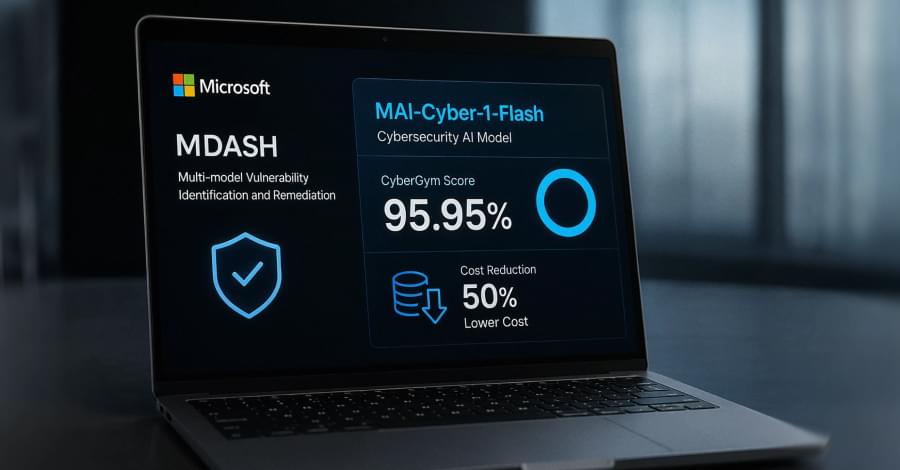
Microsoft Says New Cybersecurity AI Model Helps MDASH Hit 95.95% at Half the Cost
Microsoft has launched its first cybersecurity-specific model inside MDASH, its multi-model vulnerability identification and remediation harness.
The company says MDASH, using MAI-Cyber-1-Flash and GPT-5.4, scored 95.95% on CyberGym. It also claims the configuration costs 50% less than its current best MDASH combination of GPT-5.4, GPT-5.4 mini, and GPT-5.3 Codex. Access is limited to approved MDASH customers through an Azure AI Foundry private preview.
MAI-Cyber-1-Flash is designed to handle up to 90% of MDASH tasks, with GPT-5.4 reserved for the hardest 10%. It is available only inside MDASH, not as a standalone public model or general-purpose application programming interface.
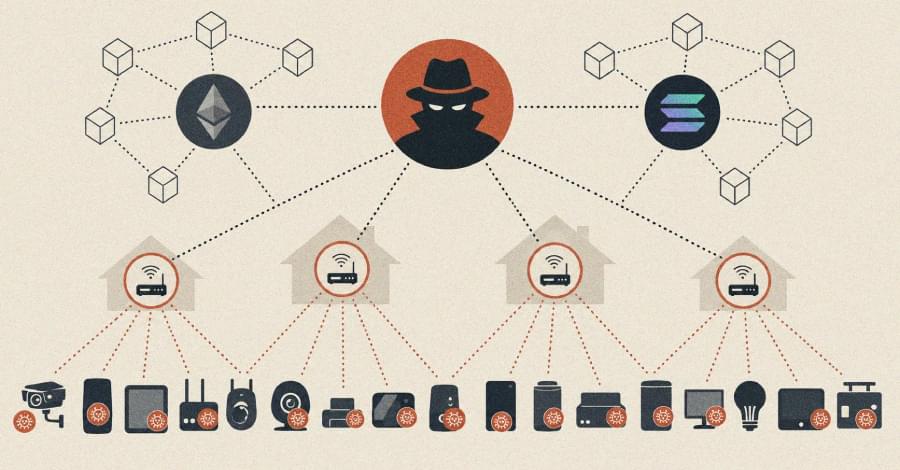
Dysphoria IoT Botnet Adds Blockchain C2 and Victim Relays After JackSkid Disruption
The lineage runs through JackSkid, one of four IoT botnets targeted in coordinated U.S., German, and Canadian law-enforcement actions on March 19. Court documents attributed more than 90,000 DDoS commands to JackSkid alone.
Within days, Nokia Deepfield and Comcast’s threat lab documented the operator falling back to an Ethereum Name Service (ENS) domain, m3rnbvs5d[.]eth, for command-and-control (C2). XLab’s Dysphoria timeline opens with a JackSkid sample captured on March 25, six days after the disruption, that resolves C2 through the same domain.
XLab found that the burrberry[.]eth record encodes distribution-node IPv4 addresses, while 24carnforth2merseyside[.]sol supplies other infrastructure records. The DDoS sample asks a distribution node over HTTP for a current server list, and the listed endpoints are infected machines relaying traffic to the real controllers. The design keeps those controllers one step removed from the addresses exposed to bots.
New Dysphoria DDoS botnet spreads to 200k devices worldwide
A botnet called Dysphoria has compromised around 200,000 devices across the world and is using them for distributed denial of service (DDoS) attacks and traffic relay operations.
According to QiAnXin XLab cybersecurity researchers, Dysphoria evolved from the ‘jackskid’ and ‘fbot’ malware by adding a covert blockchain-based command-and-control (C2) resolution mechanism.
Specifically, the botnet uses Ethereum ENS and Solana SNS domains to retrieve infrastructure information, while C2 addresses are concealed inside fake IPv6 strings and recovered using a custom byte-transformation algorithm.