Apache Roller CVE-2026–129448 is actively exploited, allowing unauthenticated remote code execution via XML-RPC. Upgrade to 6.1.6.
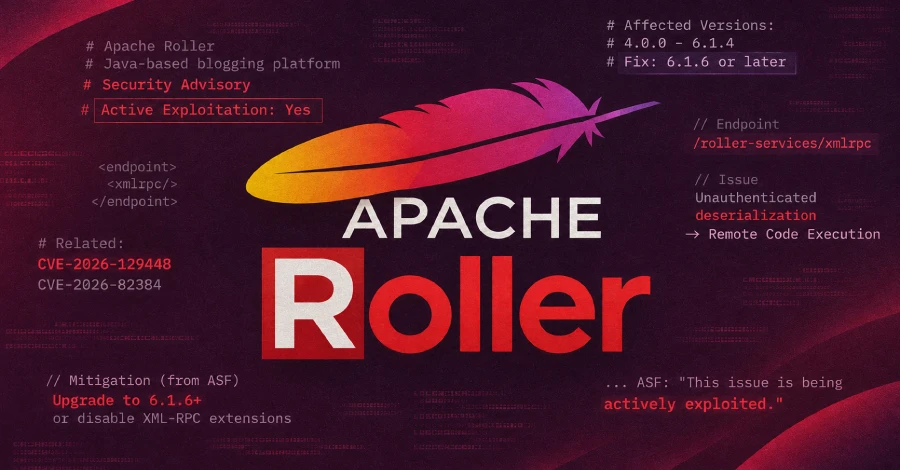
Apache Roller CVE-2026–129448 is actively exploited, allowing unauthenticated remote code execution via XML-RPC. Upgrade to 6.1.6.