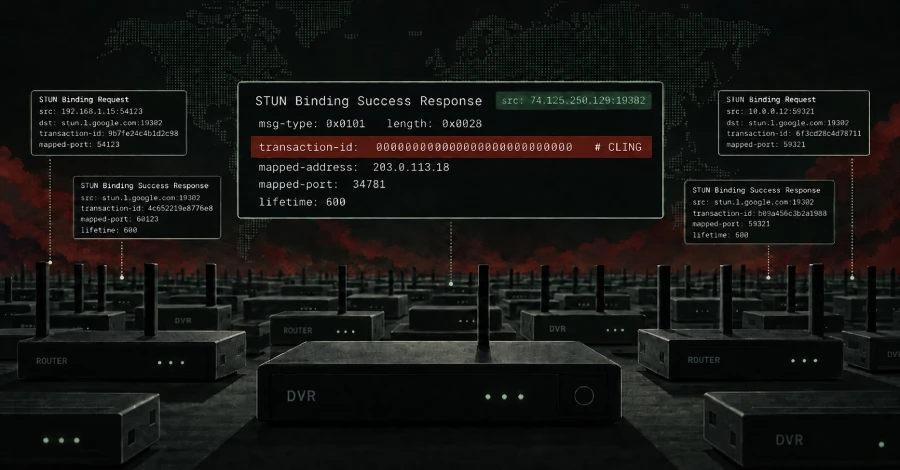
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling.
“Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel,” Nozomi Networks said in a report published last week. “The result is a botnet whose traffic can resemble legitimate NAT-traversal activity while still supporting propagation, proxying, tunneling and denial-of-service commands.”
The operational technology (OT) security company said it observed a spike in attempts to exploit CVE-2021–35394 (CVSS score: 9.8), a critical remote code execution (RCE) flaw in Realtek Jungle SDK starting around September 5, 2026, with a subset of the activity delivering Cling.