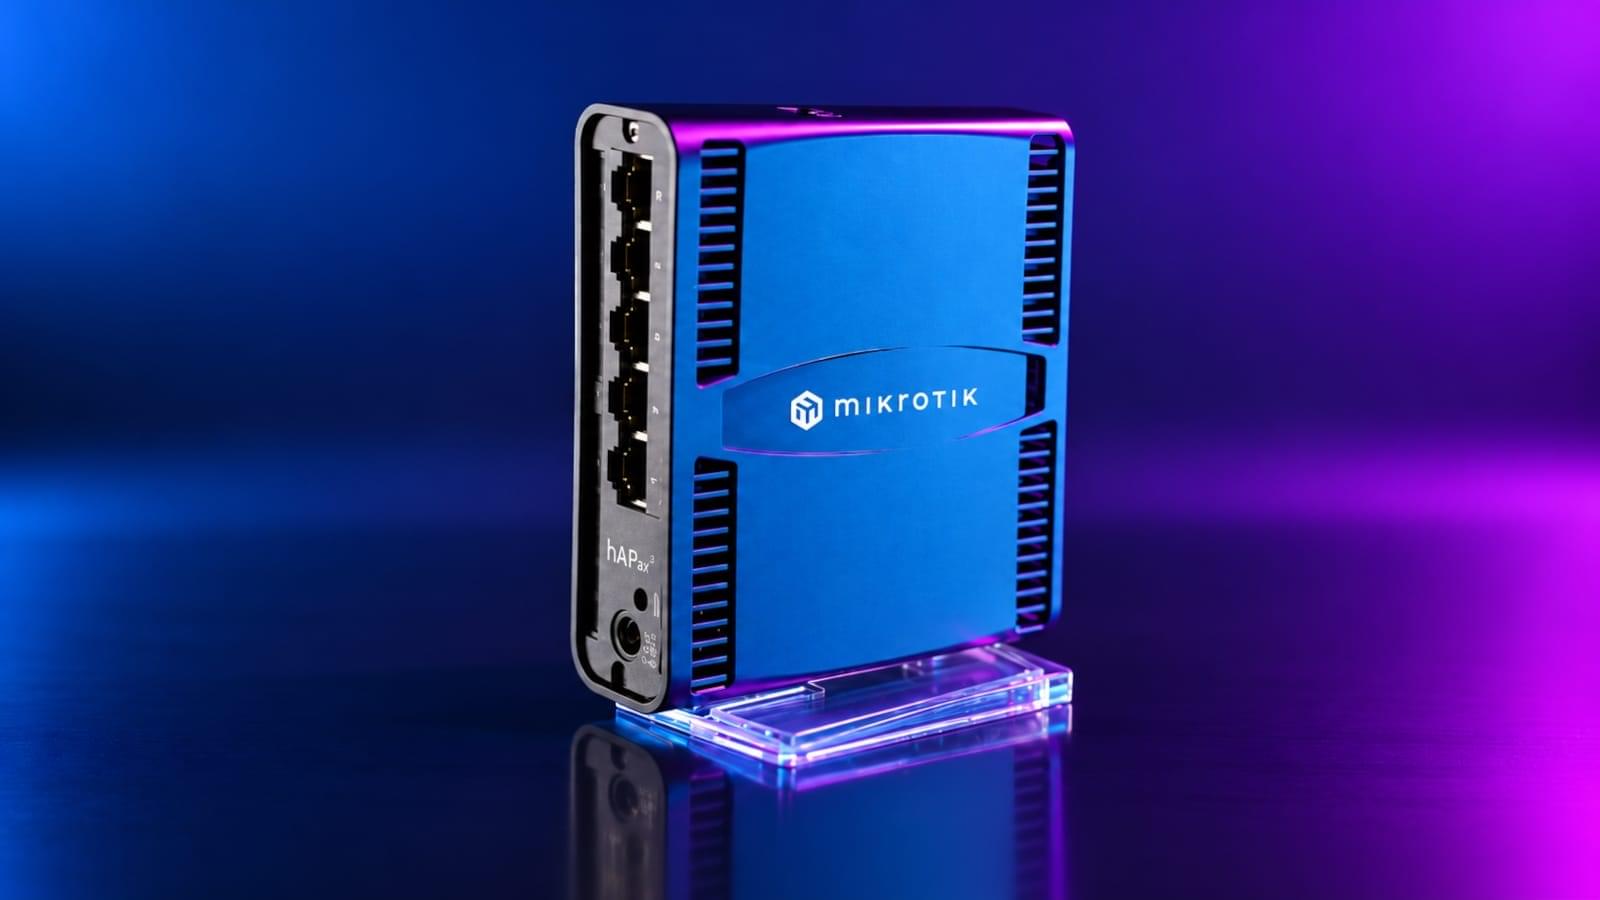
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning of a new critical vulnerability in MikroTik RouterOS that could lead to remote code execution or cause a denial-of-service condition.
Tracked as CVE-2026–84411, the security issue is a pre-authentication integer underflow in RouterOS’s web-management HTTP request handling.
CISA says that a single crafted request can produce code execution with root privileges or denial of service.