Handala Hack is linked to HEAVYGRAM, a Telegram-based backdoor that can steal passwords, messaging data, screenshots, and files.
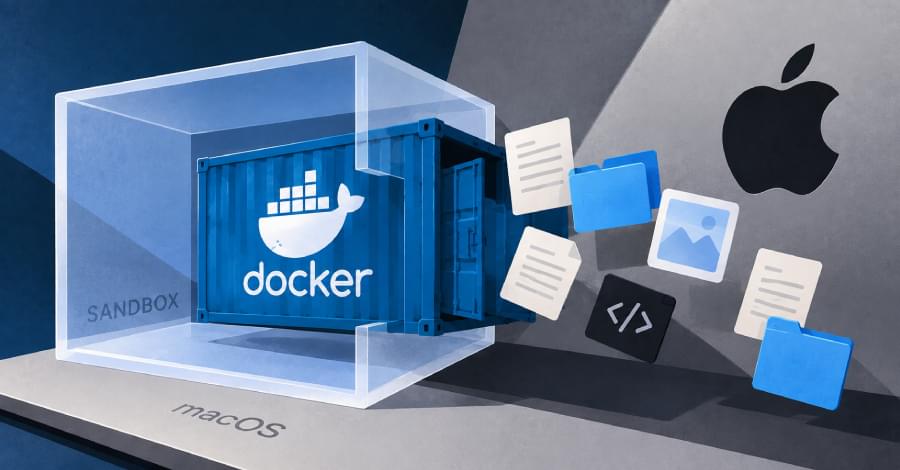
Docker Sandboxes runs each AI coding agent in its own small virtual machine with the project directory shared in. The code that could escape is whatever runs inside that machine, such as a coding agent that has been turned against its user, or anything malicious the agent installs and runs.
Docker has not reported any exploitation. CISA’s added assessment on the CVE record lists exploitation as none, and the flaw is not in CISA’s Known Exploited Vulnerabilities catalog as of the catalog version released on September 16.
The flaw needs malicious code inside the sandbox, and protecting the host from what an agent runs is what the sandbox is for. The agent installs packages and runs commands with sudo inside the virtual machine, and Docker’s isolation documentation says the hypervisor boundary “is the isolation control, not in-VM privilege separation.”
A new Android malware called RatHat has been discovered, targeting users with an AI-powered subsystem that helps operators remotely navigate compromised devices.
Zimperium zLabs researchers analyzed the malware and believe it is linked to threat actors from China after finding it using LLM prompts written in Chinese.
The researchers say the malware is distributed through malvertising, SMS, and phishing sites promoting APK downloads from outside Google Play.
Brevo confirmed that attackers stole a Cloudflare API key and used it to inject malicious ClickFix scripts into its websites and JavaScript files embedded on customer sites to distribute malware.
The customer relationship management and digital marketing company says the attackers used the API key to create a malicious Cloudflare Worker that modified content at the CDN edge for approximately five and a half hours on September 14.
The attack affected pages on brevo.com, sendinblue.com, login/account/my/onboarding.brevo.com, and sibforms.com. The Cloudflare worker also modified the Brevo forms script, Brevo Conversations widget, and the Brevo SDK loader scripts that customers embed on their websites.
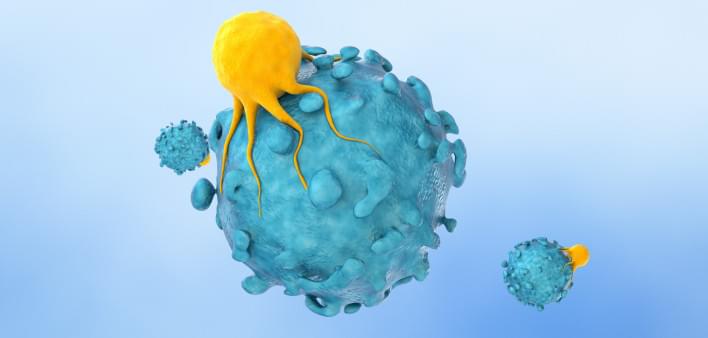
Post et al. develop a screening method to identify cell-penetrating peptides (CPPs) encoded by human gut microorganisms. They thereby discovered a peptide which preferentially enters cancer cell lines over healthy cell lines.
Abstract. Intracellular delivery of therapeutics remains a major challenge for modern medicine. To enhance intracellular uptake, therapeutics can be delivered with carrier proteins possessing an inherent cell-penetrating activity. There is an increasing need for new cell-penetrating carriers with diverse biophysical properties and mechanisms of action to transport a wide range of therapeutic cargo. As many cell-penetrating proteins and peptides derive from natural proteins, we sought to mine a previously unexplored community, the human gut microbiome, for cell-penetrating sequences. Here, we performed a high-throughput functional metagenomic screen to identify cell-penetrating protein fragments from the human gut microbiome. We identified protein fragments encoded within glycosidase enzymes from members of the Bacteroidetes phylum that mediate internalization into human cell lines when displayed on the surface of nonpathogenic, noninvasive Escherichia coli. We investigate one fragment, dubbed Gh_112, that adheres to human fibronectin, activates multiple endocytic pathways, and specifically promotes uptake of E. coli into multiple cancerous epithelial cell lines rather than healthy epithelial tissue in vitro. Overall, this work demonstrates that the human gut microbiome is a source of cell-penetrating sequences and expands the known repertoire of cell-penetrating carrier systems.
To bridge this gap, researchers have developed greCAPTCHA—a proctored testing system designed to measure an author’s “capacity to verify.” Instead of just checking who wrote the text, greCAPTCHA tests whether the authors possess the deep knowledge and critical reasoning required to understand and defend the core ideas in their manuscript.
School of Computer Science is at the forefront of all facets of computing research and education.
A highly publicized August 2026 pre-print paper led by researchers Peter Kirgis and Sayash Kapoor at Princeton University has delivered a decisive blow to one of Silicon Valley’s most cherished narratives: that artificial intelligence is on the verge of recursively improving itself into superintelligence. The study’s findings are unambiguous—current AI agents, despite their impressive coding abilities, fundamentally lack the creative scientific judgment required to conduct original machine learning research.
◆ Emerald Pages ◆ artificial intelligence How a New Princeton Study Disproves AI Self-Improvement Alarmism Emerald Book Publication September 16, 2026 7 min read A landmark Princeton study proves current AI models cannot recursively self-improve, exposing both the industry’s grand promises and its whistleblower panic as fundamentally disconnected from how the technology actually works. Photo: