Apple’s CVE-2026–65400 Screen Sharing flaw is under active exploitation on internet-exposed Macs to install a Monero miner.
Category: cryptocurrencies – Page 2
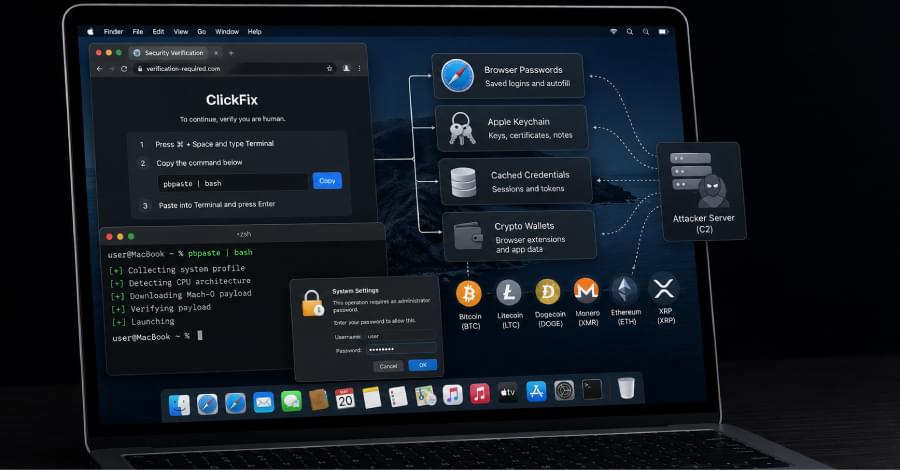
ClickFix Attacks Deliver macOS Stealer That Can Drain Crypto Wallets
ClickFix attacks deliver a Go-based macOS stealer that steals passwords and Keychain data and can drain part or all of cryptocurrency wallets.
Over 250 ClickFix Domains Use Browser Fingerprinting to Hide macOS Malware Lures
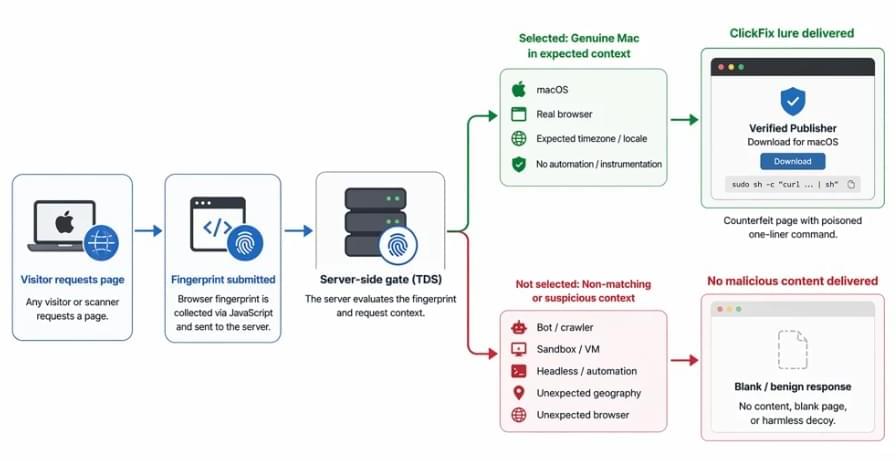
A macOS ClickFix operation spanning more than 250 front-end domains now fingerprints visitors before deciding whether to show them a malware lure, a change Microsoft Threat Intelligence tracked on infrastructure it had been watching for weeks.
The server-side gate hides the malicious page from crawlers and sandboxes while presenting selected Mac users with a fake software download. Microsoft said the wider cluster distributed MacSync and Atomic Stealer (AMOS); the chain it analyzed through the gate ended in AMOS.
The attack still requires the user to copy and run an obfuscated command in Terminal. That command retrieves scripts and launches an infostealer targeting credentials, browser data, authentication stores, cryptocurrency wallets, and sensitive files. Microsoft has not disclosed victim numbers, targeted sectors, or the identity of the operators.
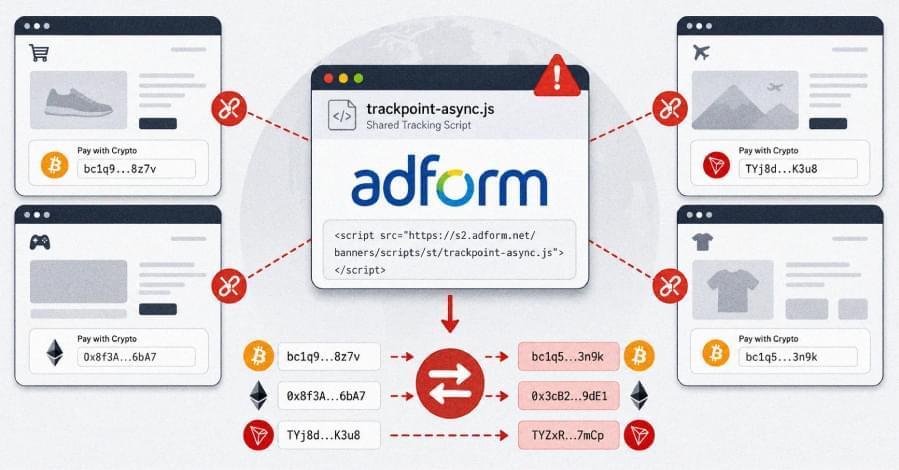
Hackers Poison Adform Script to Swap Crypto Wallet Addresses Across Customer Sites
Attackers altered Adform’s trackpoint-async.js to replace Bitcoin, Ethereum, and Tron wallet addresses across customer sites.
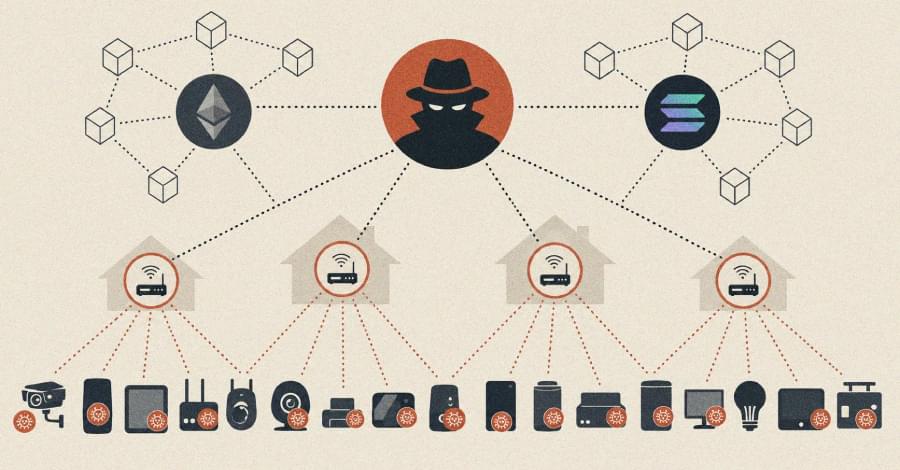
Dysphoria IoT Botnet Adds Blockchain C2 and Victim Relays After JackSkid Disruption
The lineage runs through JackSkid, one of four IoT botnets targeted in coordinated U.S., German, and Canadian law-enforcement actions on March 19. Court documents attributed more than 90,000 DDoS commands to JackSkid alone.
Within days, Nokia Deepfield and Comcast’s threat lab documented the operator falling back to an Ethereum Name Service (ENS) domain, m3rnbvs5d[.]eth, for command-and-control (C2). XLab’s Dysphoria timeline opens with a JackSkid sample captured on March 25, six days after the disruption, that resolves C2 through the same domain.
XLab found that the burrberry[.]eth record encodes distribution-node IPv4 addresses, while 24carnforth2merseyside[.]sol supplies other infrastructure records. The DDoS sample asks a distribution node over HTTP for a current server list, and the listed endpoints are infected machines relaying traffic to the real controllers. The design keeps those controllers one step removed from the addresses exposed to bots.
New Dysphoria DDoS botnet spreads to 200k devices worldwide
A botnet called Dysphoria has compromised around 200,000 devices across the world and is using them for distributed denial of service (DDoS) attacks and traffic relay operations.
According to QiAnXin XLab cybersecurity researchers, Dysphoria evolved from the ‘jackskid’ and ‘fbot’ malware by adding a covert blockchain-based command-and-control (C2) resolution mechanism.
Specifically, the botnet uses Ethereum ENS and Solana SNS domains to retrieve infrastructure information, while C2 addresses are concealed inside fake IPv6 strings and recovered using a custom byte-transformation algorithm.
New ClickLock macOS malware traps users into revealing login password
A new macOS information-stealing malware dubbed ClickLock terminates all visible processes to force users into entering their system login password.
The malware is designed to steal cryptocurrency assets, login credentials, password-manager data, browser information, and macOS authentication data, and it can also install a persistent backdoor for ongoing remote access to infected systems.
Researchers at Group-IB analyzed the ClickLock shell script after discovering the malware on VirusTotal, where it was first submitted on June 9. At the time of the report, it remained undetected by all security vendors available on the platform.
Scientists Keep Teaching Life to Play Doom, But Why?
Support this channel on Patreon to help me make this a full time job: / whatdamath (Unreleased videos, extra footage, DMs, no ads)
Alternatively, PayPal donations can be sent here: http://paypal.me/whatdamath.
Get a Wonderful Person Tee: https://teespring.com/stores/whatdamath.
More cool designs are on Amazon: https://amzn.to/3QFIrFX
Hello and welcome! My name is Anton and in this video, we will talk about why Doom is used in scientific experiments involving learning.
Links:
https://arxiv.org/pdf/2602.11632
https://corticallabs.com/cl1
• Rats in Doom.
https://theconversation.com/how-scien…
#doom #biology #learning.
0:00 Doom runs on everything.
1:03 Brain organoids and why they are used.
2:50 New breakthrough — a biological computer.
3:50 How cells learns to play Doom.
5:10 Rats and Doom.
6:20 Organoids and engineering problems.
7:00 Implications for biology and information sciences.
9:08 Conclusions.
Enjoy and please subscribe.
Bitcoin/Ethereum to spare? Donate them here to help this channel grow!
bc1qnkl3nk0zt7w0xzrgur9pnkcduj7a3xxllcn7d4
or ETH: 0x60f088B10b03115405d313f964BeA93eF0Bd3DbF
The hardware used to record these videos:
Nearly 300 GitHub repos pose as legit software to push malware
A threat actor has published hundreds of fake GitHub repositories impersonating legitimate software and security projects to distribute infostealer malware.
The campaign drew traffic from search results for security products, cryptocurrency services, financial tools, developer utilities, secure email providers, macOS utilities, and gaming software.
The malware collects data from more than 19 web browsers, steals info from 32 cryptocurrency wallets, and exfiltrates sensitive details from messaging and social media apps.
Attackers Exploit ‘Ill Bloom’ Vulnerability to Drain Over $5 Million From Cryptocurrency Wallets
Coinspect confirms over $5M stolen via the Ill Bloom flaw. Weak seed generation left older mobile and browser-extension wallets exposed.