Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Earth and Mars Were Formed in Fundamentally Different Ways, Study Finds

Earth and Mars may have formed through different mixtures of planetary building processes, despite developing side by side.

Earth and Mars formed near each other about 4.5 billion years ago, yet new research suggests they grew through very different processes.

“The most surprising result was that Earth and Mars appear to have formed in different ways. You might have expected that two planets formed side by side in the same solar system would share a more similar formation history,” says Professor Anders Johansen, who studies planet formation at the Globe Institute, University of Copenhagen. He co-led the new study with Assistant Professor Haiyang Wang.
Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users’ Mailboxes

The Windows maker said an authenticated attacker can exploit this flaw to gain unauthorized access to other users’ mailboxes within the same organization and read email messages and attachments. However, the vulnerability does not allow cross-tenant access.

Microsoft has already deployed a “related service-side fix” to Exchange Online to address the issue. As a result, Exchange Online customers are not required to take any action.

Realtek Jungle SDK Exploit Attempts Deliver Cling Botnet With STUN-Based C2

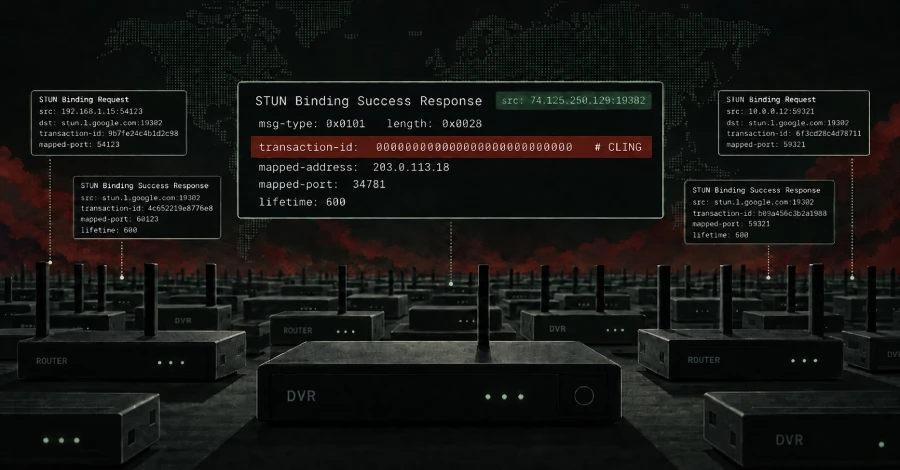
Threat actors have been observed attempting to exploit a now-patched critical security flaw impacting the Realtek Jungle software development kit (SDK) to deploy a botnet malware called Cling.

“Cling is notable not because it introduces a new propagation technique, but because it repurposes ordinary STUN behavior into a practical command-and-control channel,” Nozomi Networks said in a report published last week. “The result is a botnet whose traffic can resemble legitimate NAT-traversal activity while still supporting propagation, proxying, tunneling and denial-of-service commands.”

The operational technology (OT) security company said it observed a spike in attempts to exploit CVE-2021–35394 (CVSS score: 9.8), a critical remote code execution (RCE) flaw in Realtek Jungle SDK starting around September 5, 2026, with a subset of the activity delivering Cling.

Google halts open-source bug bounty program amid AI spam surge

Google has now suspended submissions to its Open Source Software Vulnerability Rewards Program (OSS VRP) after being flooded by AI-generated reports.

The company’s OSS VRP incentivizes security researchers to responsibly disclose security flaws across open-source projects maintained by Google, including Golang, Angular, Bazel, Protocol Buffers, Fuchsia, and critical third-party dependencies, as well as repository settings like GitHub actions, application configurations, and access control rules.

Google launched the OSS VRP in August 2022 with rewards ranging from $100 to $31,337, and noted that the program would focus on security flaws with the most significant impact on the software supply chain.

OpenAI is adding invisible watermarks to ChatGPT and Codex text in the EU

OpenAI is preparing to add invisible watermarks to text generated by ChatGPT and Codex in the European Union.

The watermark will not be visible when you read or copy the text. Instead, OpenAI says its new textGrain technology slightly changes the model’s word choices to create a statistical pattern that can later be detected.

“Over the coming weeks, we will add an invisible watermark to eligible ChatGPT and Codex text output in the European Union,” OpenAI explained.

Rejetto HFS servers now actively scanned for critical RCE flaw

Hackers are actively scanning for a Rejetto HFS weak signing key vulnerability, tracked as CVE-2026–61500, that allows session forgery, account takeover, and remote code execution (RCE).

VulnCheck VP of Security Research Caitlin Condon posted on LinkedIn over the weekend that the company’s Canary Intelligence honeypots had observed probes targeting CVE-2026–61500.

Condon said the observed activity appears to be small-scale reconnaissance from a single China Telecom IP address probing deployments in Japan and the United States.

New Dell System Update flaw lets hackers gain root privileges

Dell warned customers to patch a critical vulnerability in the System Update (DSU) command-line interface (CLI) deployment tool as soon as possible.

DSU lets enterprise IT administrators deploy BIOS, firmware, and software updates onto Linux and Windows systems on PowerEdge enterprise server infrastructure.

In a Thursday security advisory, the company said the flaw (tracked as CVE-2026–86360) allows threat actors to execute code with root privileges on unpatched devices by exploiting a path traversal weakness.

Microsoft: Windows KB5124010 update crashes some games and apps

Microsoft confirmed over the weekend that some games and applications using AC-3 (Dolby Digital) audio decoding will crash after installing the September 2026 KB5124010 Windows 11 preview update.

KB5124010 is an optional update that requires users to click the “Download and install” link, which should reduce the number of potentially affected Windows users. However, it installs automatically on devices running Windows 11 24H2, where the “Get the latest updates as soon as they’re available” option is toggled on.

“In some cases the application can fail to launch, or close without warning. In other cases the application will work normally until certain features are used, such as playing music,” Microsoft said in a Friday update to the Windows release health dashboard. “Affected applications may vary and can include games, media players, and certain productivity applications.”

/* */