Six Proto6 flaws in protobuf.js enable RCE and DoS attacks; patched in versions 7.5.6 and 8.0.2 to protect Node.js services.
Get the latest international news and world events from around the world.
Microsoft Restores Some GitHub Repos, Keeps Others Offline as Miasma Probe Continues
Microsoft confirms it temporarily removed GitHub repos after Miasma worm compromised 73 of its open-source projects to inject an information stealer.
WinRAR Flaw Exploited by Russia-Aligned Groups to Deploy Stealers in Ukraine
Two Russia-aligned cyber attack campaigns have continued to exploit a security flaw in WinRAR to target Ukrainian organisations, almost a year after patches for the vulnerability were released.
The activity has been attributed by Trend Micro to Earth Dahu (aka Gamaredon) and SHADOW-EARTH-066 (aka UAC-0226). It involves the exploitation of CVE-2025–8088, a path traversal flaw that allows an attacker to write files outside the extraction directory via NTFS Alternate Data Streams (ADS). It was patched by WinRAR in July 2025.
The findings show “how unmanaged software keeps an exploited entry point open long after the fix ships,” Trend Micro researchers Hiroyuki Kakara and Feike Hacquebord said in an analysis published Monday.
Chrome V8 Zero-Day CVE-2026–11645 Exploited in the Wild — Patch Now
Google has released security updates to address 74 vulnerabilities, including one that has come under active exploitation in the wild.
The high-severity vulnerability, tracked as CVE-2026–11645 (CVSS score: 8.8), has been described as an out-of-bounds memory access in V8, Chrome’s JavaScript and WebAssembly engine.
“Out-of-bounds read and write in V8 in Google Chrome prior to 149.0.7827.103 allowed a remote attacker to execute arbitrary code inside a sandbox via a crafted HTML page,” reads a description of the flaw in the NIST’s National Vulnerability Database (NVD).
Researchers Build Self-Replicating AI Worm That Operates Entirely on Local, Open-Weight Models
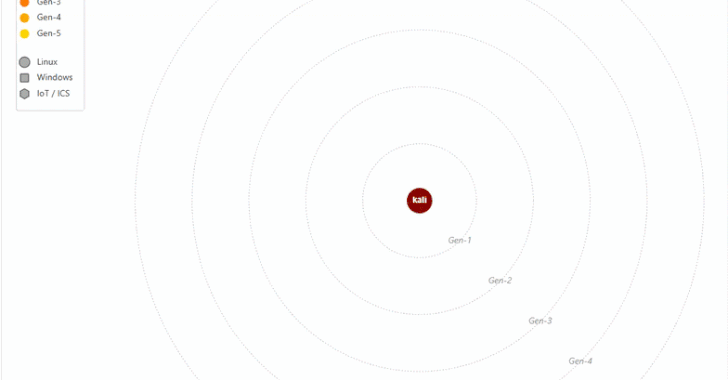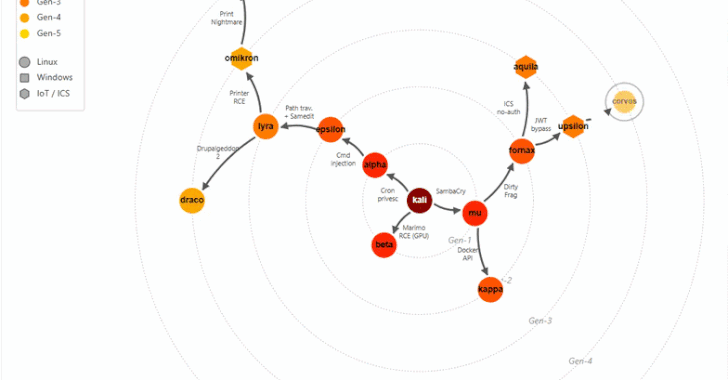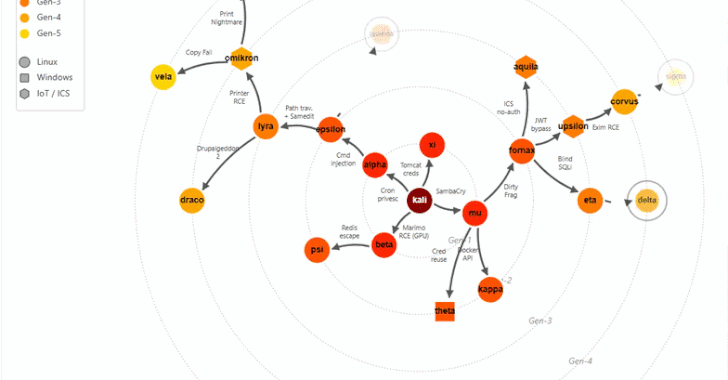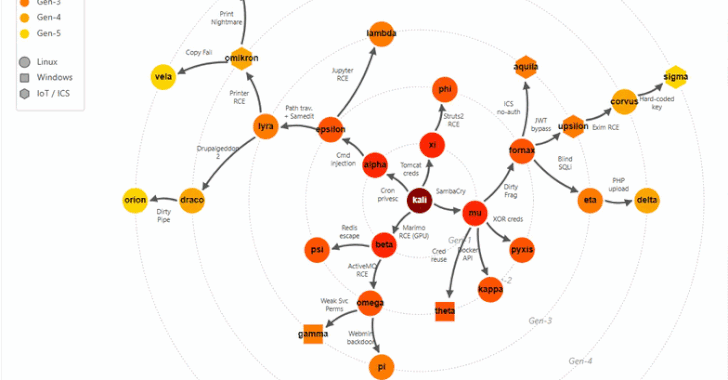
An AI-driven worm using a local open-weight LLM autonomously exploited and replicated across 62% of a 33-host test network in 7 days.
The Hidden Security Risk in Modern Networks: The Work Between Tools
Fragmented workflows slow network security response across hybrid environments, increasing MTTR, errors, and audit risk.
GitHub disables Microsoft repos pushing password-stealing malware
Microsoft removed 73 repositories across its Azure, microsoft, Azure-Samples, and MicrosoftDocs organizations on GitHub, disrupting continuous integration pipelines.
The incident occurred on June 5, and it was contained within just 105 seconds. The company told BleepingComputer that the repositories were removed due to concerns that they distributed “potential malicious content.”
Multiple researchers confirmed that the repos were pulled after a compromise during a Miasma/Shai-Hulud supply-chain campaign.
Microsoft Defender ‘RoguePlanet’ zero-day grants SYSTEM privileges
A security researcher has released a new Microsoft Defender zero-day exploit named “RoguePlanet” just hours after Microsoft fixed two previously disclosed flaws during June 2026 Patch Tuesday.
The researcher, known as Nightmare Eclipse, says the new vulnerability affects fully patched Windows 10 and Windows 11 devices, allowing attackers to spawn a command prompt with SYSTEM privileges via a Microsoft Defender race condition vulnerability.
The researcher shared a proof-of-concept exploit on Tuesday afternoon in a self-hosted Git repository after saying that GitHub and GitLab repositories hosting their exploits had previously been removed by Microsoft.
New Compound Blocks Nerve Cell Death in Alzheimer’s
Researchers created Compound 10 to block GRK2 enzyme aggregation and protect mitochondria in Alzheimer’s disease.
A brain-computer interface that works with—not against—the brain
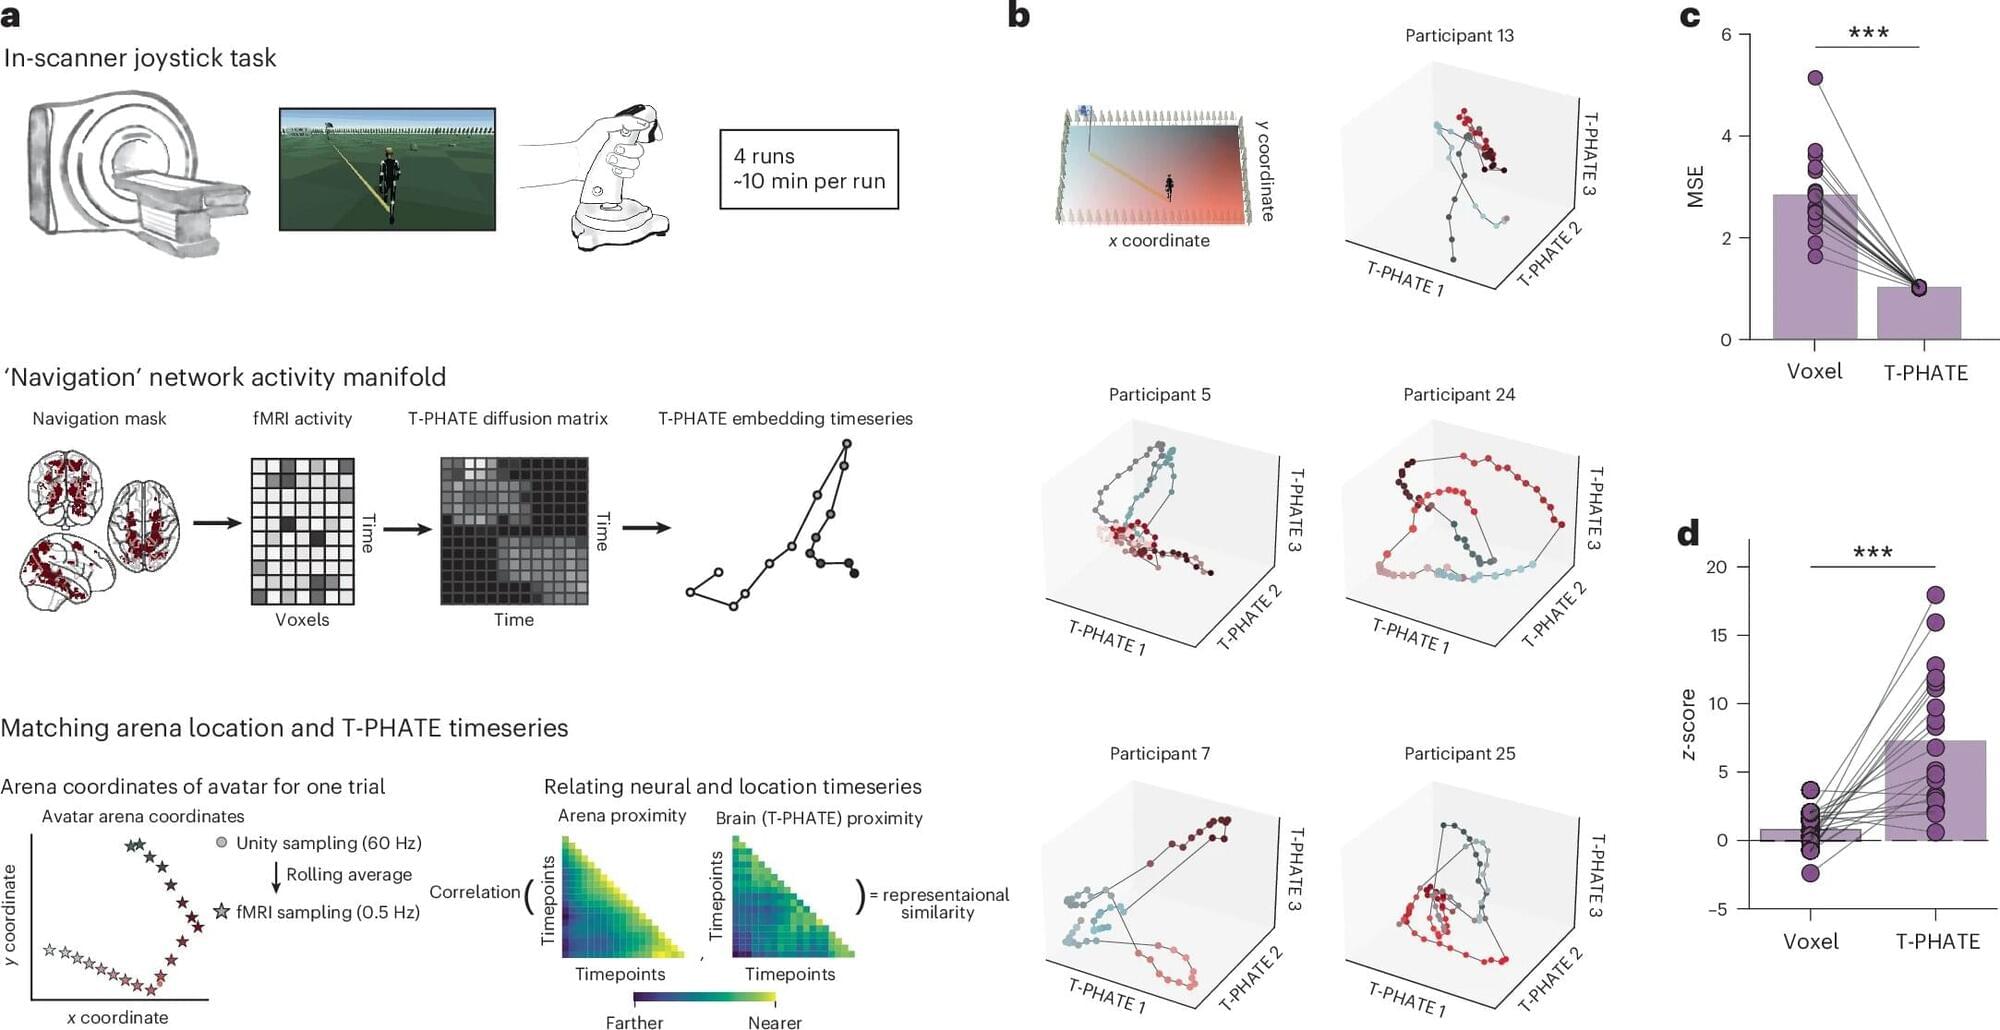
It might soon be “game over” for the video game controller. Yale researchers have developed a new kind of brain-computer interface (BCI) that lets humans play video games directly with their brains. Using real-time fMRI (functional MRI), they confirmed that the technology could help humans control a computer with their brain activity in a highly efficient way. The study appears in the journal Nature Neuroscience.
A BCI is technology that allows a human to control a computer with brain activity. Historically, they have not been effective. BCIs built using real-time neurofeedback from fMRI—a type of MRI scan showing which areas of the brain are most active over time—require up to 10 long training sessions per person, and even then the learning effects are modest. About a third of users never gain control, regardless of how many hours they practice.