China plans to finish a geological map of Mars by 2028, using data from the Zhurong rover and artificial intelligence.
Threat actors have been observed exploiting a critical pre-authentication command injection vulnerability in Citrix NetScaler ADC and NetScaler Gateway to drop web shells and attempt theft of configuration data.
LevelBlue’s Threat Hunt Operations & Research (THOR) team, which analyzed the exploitation activity across multiple customer environments, said it identified malicious NetScaler authentication events containing attacker-controlled usernames designed to weaponize CVE-2026–88771.
CVE-2026–88771 (CVSS score: 9.5) is an improper input validation vulnerability that could allow an unauthenticated attacker to execute arbitrary commands.
Attackers are exploiting a new critical zero-day flaw in Cisco Catalyst SD-WAN Manager, the system companies use to manage their Cisco SD-WAN networks, Cisco said in an advisory on September 30.
The flaw, CVE-2026–76504, could allow a remote attacker with no login access to use the Manager’s API as the admin user. Fixed releases are available, and there is no workaround. It carries a CVSS score of 9.8 out of 10. It sits in the part of the Manager’s API that handles login sessions.
The Manager mishandles URI encoding in an HTTP request. A crafted request can therefore bypass an authentication rule intended to restrict access to a single API endpoint.
The Russian state actor Star Blizzard has been using a new malware installation tactic dubbed “RedFlick” to deploy its signature CosmicPulse backdoor.
Although the tactic is not a new cybersecurity technique, it is a new delivery approach for the threat actor, allowing it to further automate attacks and reduce victim interaction.
Microsoft researchers say that Star Blizzard expanded its phishing operations and streamlined malware delivery in 2026.
More than 543,000 credentials exposed in public GitHub repositories were still valid in July despite the platform’s security measures to prevent accidental leaks of sensitive data.
Data pulled from scanning 224 million repositories and more than 58 billion files show that the median time a unique credential remained publicly accessible was 784 days.
The research was conducted by Truffle Security, which found that about 10% of the working credentials were older than 6.3 years and the oldest one dated from 2009.
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) is warning of a new critical vulnerability in MikroTik RouterOS that could lead to remote code execution or cause a denial-of-service condition.
Tracked as CVE-2026–84411, the security issue is a pre-authentication integer underflow in RouterOS’s web-management HTTP request handling.
CISA says that a single crafted request can produce code execution with root privileges or denial of service.
Microsoft has reminded customers that the Entra ID identity and access management (IAM) solution will get better protection against external script injection attacks starting next month.
The company first revealed plans to secure Entra ID sign-ins from script injection attacks in a November 2025 announcement.
According to a Monday message center update seen by BleepingComputer, Microsoft will begin enforcing additional Content Security Policy (CSP) defenses that will only allow scripts from trusted Microsoft content delivery network (CDN) domains during Entra ID sign-ins.
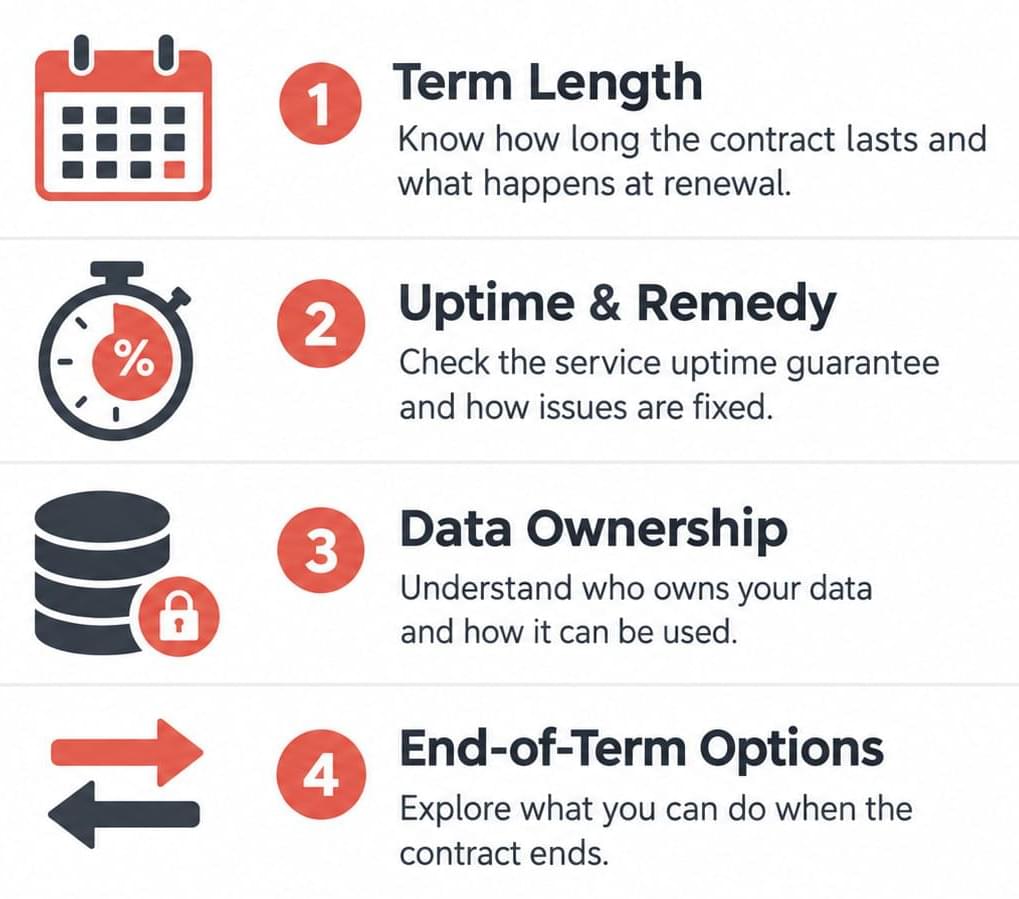
Robotics-as-a-Service removes the big upfront purchase. The vendor keeps ownership and bundles maintenance into a monthly subscription.
That structure only beats buying if four specific clauses are negotiated properly: 1. Minimum term length — long lock-in kills the flexibility RaaS is supposed to deliver. 2. Uptime with named remedies — a 99.5% SLA still permits ~44 hours of downtime a year, and most measure the robot hardware, not your actual throughput. 3. Data ownership — performance history is the asset that gives you leverage at renewal. Don’t leave it with the vendor by default. 4. End-of-term options — buyout path, disclosed renewal rates, or a clean transition to another provider.
Get these wrong and a low monthly rate with a long lock-in can quietly cost more than purchasing the robot outright.
Before signing, answer one question: if the robots miss a shipment during a defined failure, what credit do you receive, and who owns the data proving it happened?
Full analysis:
#IndustrialRobotics #RaaS #RobotProcurement #Automation
What if the future of cancer treatment isn’t about killing the last cancer cell… but finding the first one?
For more than 40 years, renowned oncologist Dr. Azra Raza has pursued this radical idea.
This Wednesday on No Time But Now, Dr. Raza, a Columbia University Irving Medical Center physician and professor, joins William Shatner and Melanie Shatner Gretsch for a powerful conversation about the future of cancer detection, the technology that could transform medicine, and the deeply human realities of grief, hope, mortality, and making every moment count.
Presented by LifeWave Corporate.
Don’t miss this conversation.
🎙️ NO TIME BUT NOW New episode drops Wednesday.