Toggle light / dark theme

Get the latest international news and world events from around the world.

Log in for authorized contributors

Forgotten Material From the 1960s Is Hiding Something Unexpected

A long-overlooked material has revealed a hidden atomic pattern that challenges conventional expectations about magnetism.

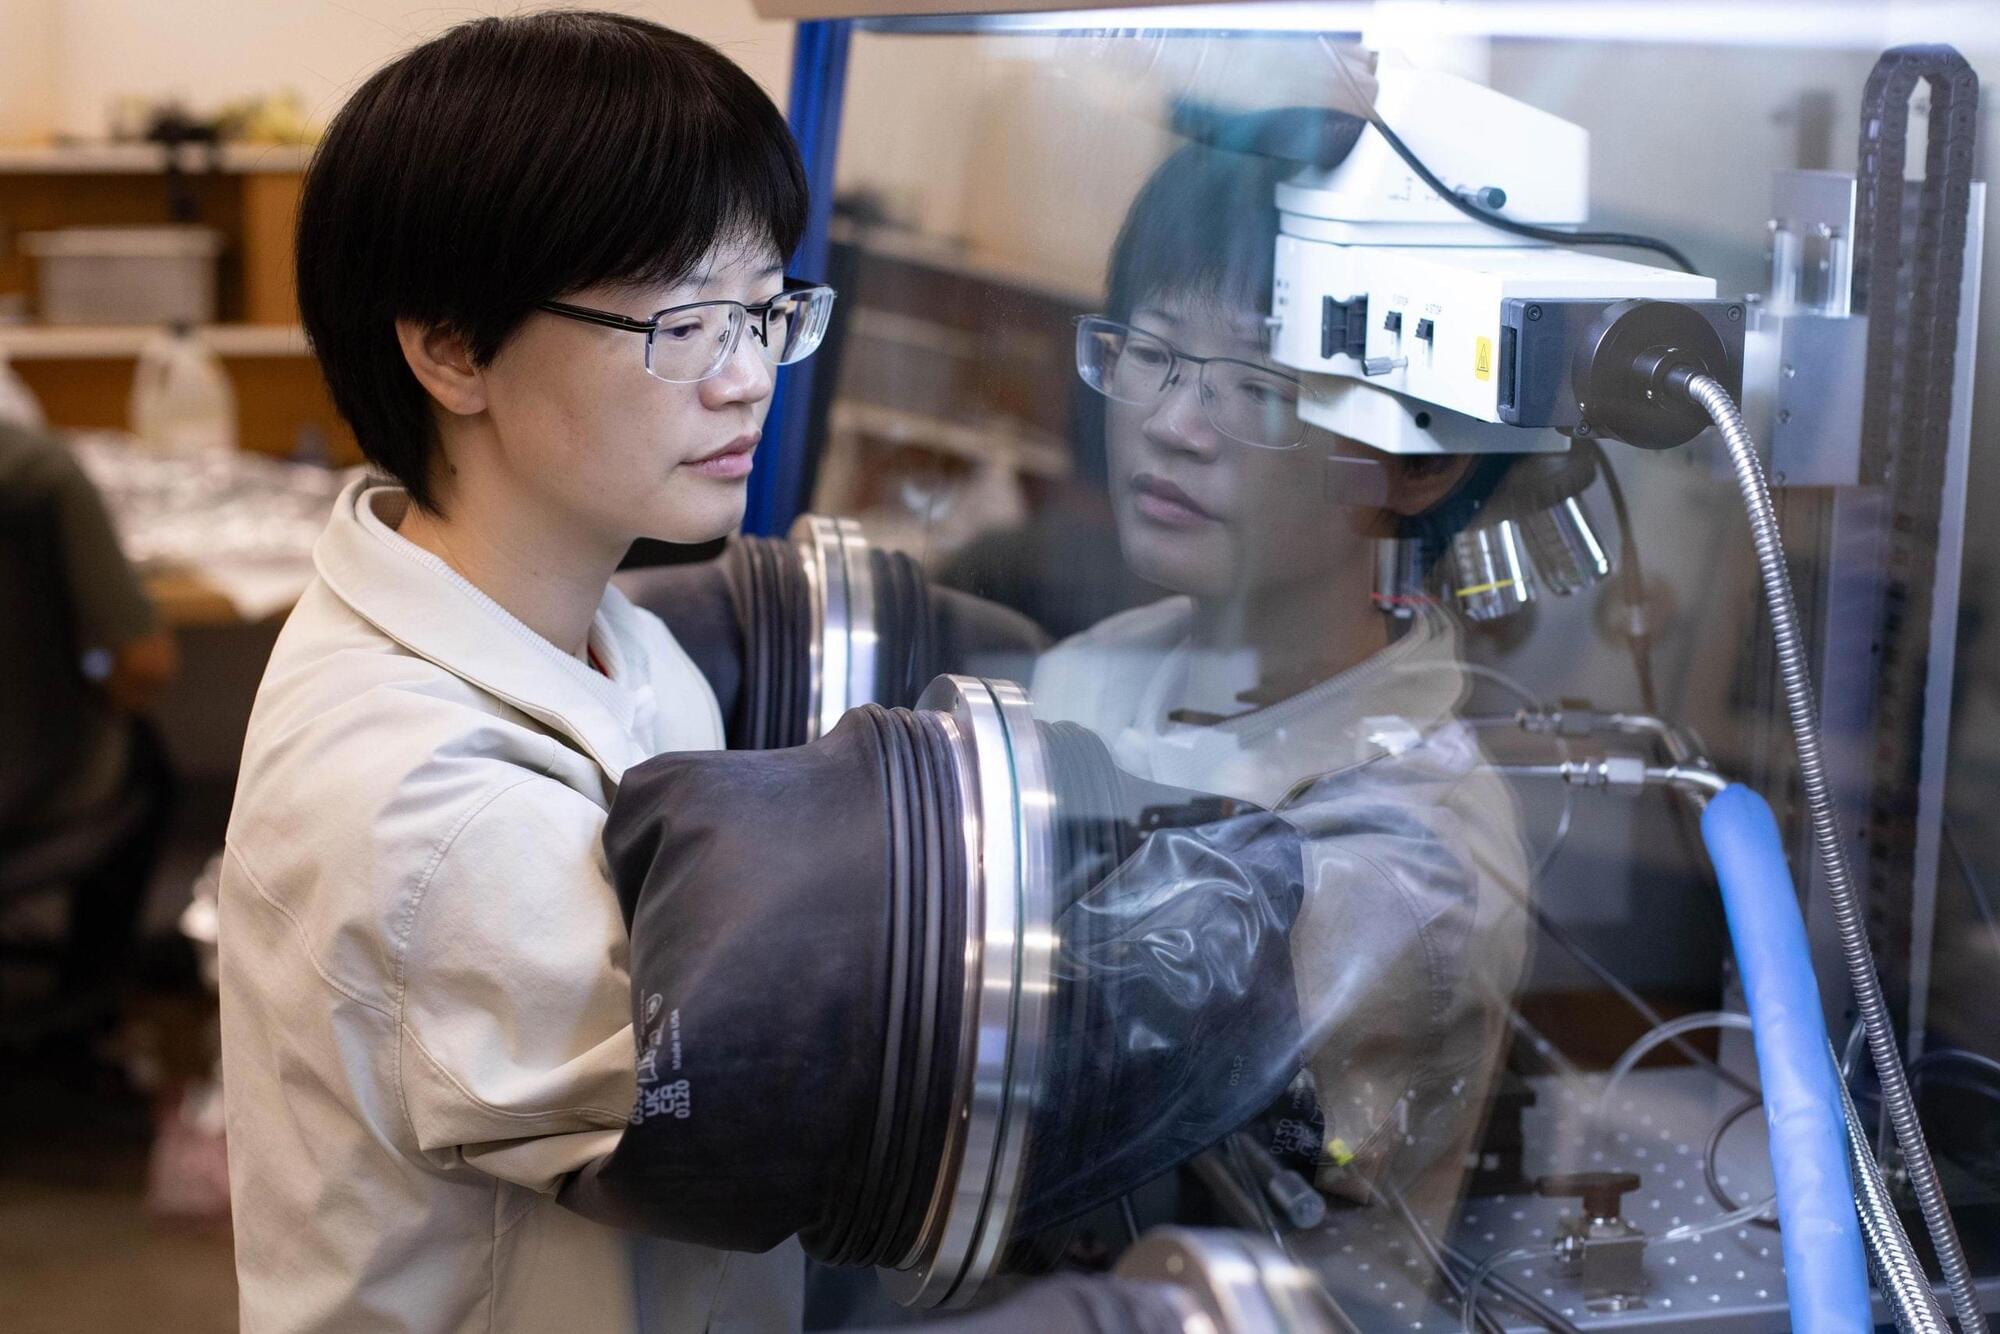
A uranium compound that has received little scientific attention for decades has been found to contain a previously unknown atomic structure with unusual magnetic properties. The discovery could help researchers identify materials capable of supporting faster, more resilient computer memory.

Scientists discovered a repeating, twisted arrangement of atoms known as a chiral superlattice inside uranium oxytelluride (UOTe). The structure appears to play a central role in how electrons move through the crystal, which exhibits an uncommon combination of two different types of magnetism. The findings were published online October 7 in Nature.
Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks

Attackers are exploiting a zero-day SQL injection flaw in Arista’s VeloCloud Orchestrator (VCO), the central management system for VeloCloud SD-WAN networks, the company said in an advisory on October 22.

The flaw lets anyone who can log in to the orchestrator, even with a read-only customer account, gain operator privileges, the top level of control over it.

For on-premises orchestrators, the fix is in VCO 5.2.3.18, 6.1.3.10, and 6.4.2.12, while Hosted and Dedicated orchestrators have already been patched.

Meta Ordered to Pay $25 Billion After Court Finds 43 Million Privacy Violations

Social media giant Meta was ordered to pay 25 billion in penalties by a New Mexico court on Wednesday as part of a data privacy lawsuit that sprang from the company’s Cambridge Analytica data scandal, which came to light in 2018.

According to multiple reports from the Associated Press, the New York Times, Reuters, and the Wall Street Journal, state District Court Judge Francis J. Mathew called out Meta and Facebook for making misleading statements about the privacy of consumers in the state.

“Facebook promised users that they (the users) controlled their data,” Mathew wrote in his ruling. “This was false.”

Capcom confirms data breach affecting 11.7 million accounts

Japanese gaming giant Capcom has confirmed that hackers breached its membership service, CAPCOM ID, exposing more than 11.7 million customer email addresses and associated information.

Apart from emails, exposed data includes account creation date, last login timestamp, number of logins, and the IP address used at the last login.

Capcom found that for a small subset of 43 accounts, dates of birth, gender, nicknames, and countries were also exposed.

Arista patches new VeloCloud Orchestrator zero-day exploited in attacks

Arista Networks released security updates to patch an actively exploited zero-day vulnerability affecting VeloCloud Orchestrator (VCO) On-Prem deployments.

VCO is a web-based management portal that helps administrators configure, monitor, and manage VeloCloud SD-WANs (Software-Defined Wide Area Networks) and associated edge devices.

Tracked as CVE-2026–114625, this critical-severity flaw can allow attackers with basic privileges, access to the VCO web interface, and a valid authenticated session to escalate privileges through low-complexity SQL injection attacks that don’t require user interaction.

LiteLLM release pipeline hacked to distribute info-stealer malware

Hackers compromised the LiteLLM project’s PyPI package and published malicious Docker images with a payload that steals credentials, secrets, and environment variables.

The supply-chain attack affected all PyPI wheels (.whl installation packages) for LiteLLM version 1.107.0, impacting Windows, Linux, and macOS systems.

LiteLLM is an open-source Python SDK and AI gateway that enables applications to access AI models from different providers through a common API.

Machine speed attacks require machine speed detection and response

Attackers can steal credentials and begin exfiltrating data within minutes, often before security teams can respond. Exaforce examines real-world attacks involving stolen GitHub tokens, malicious AI installers, and MFA phishing, explaining why faster detection and automated containment are critical.