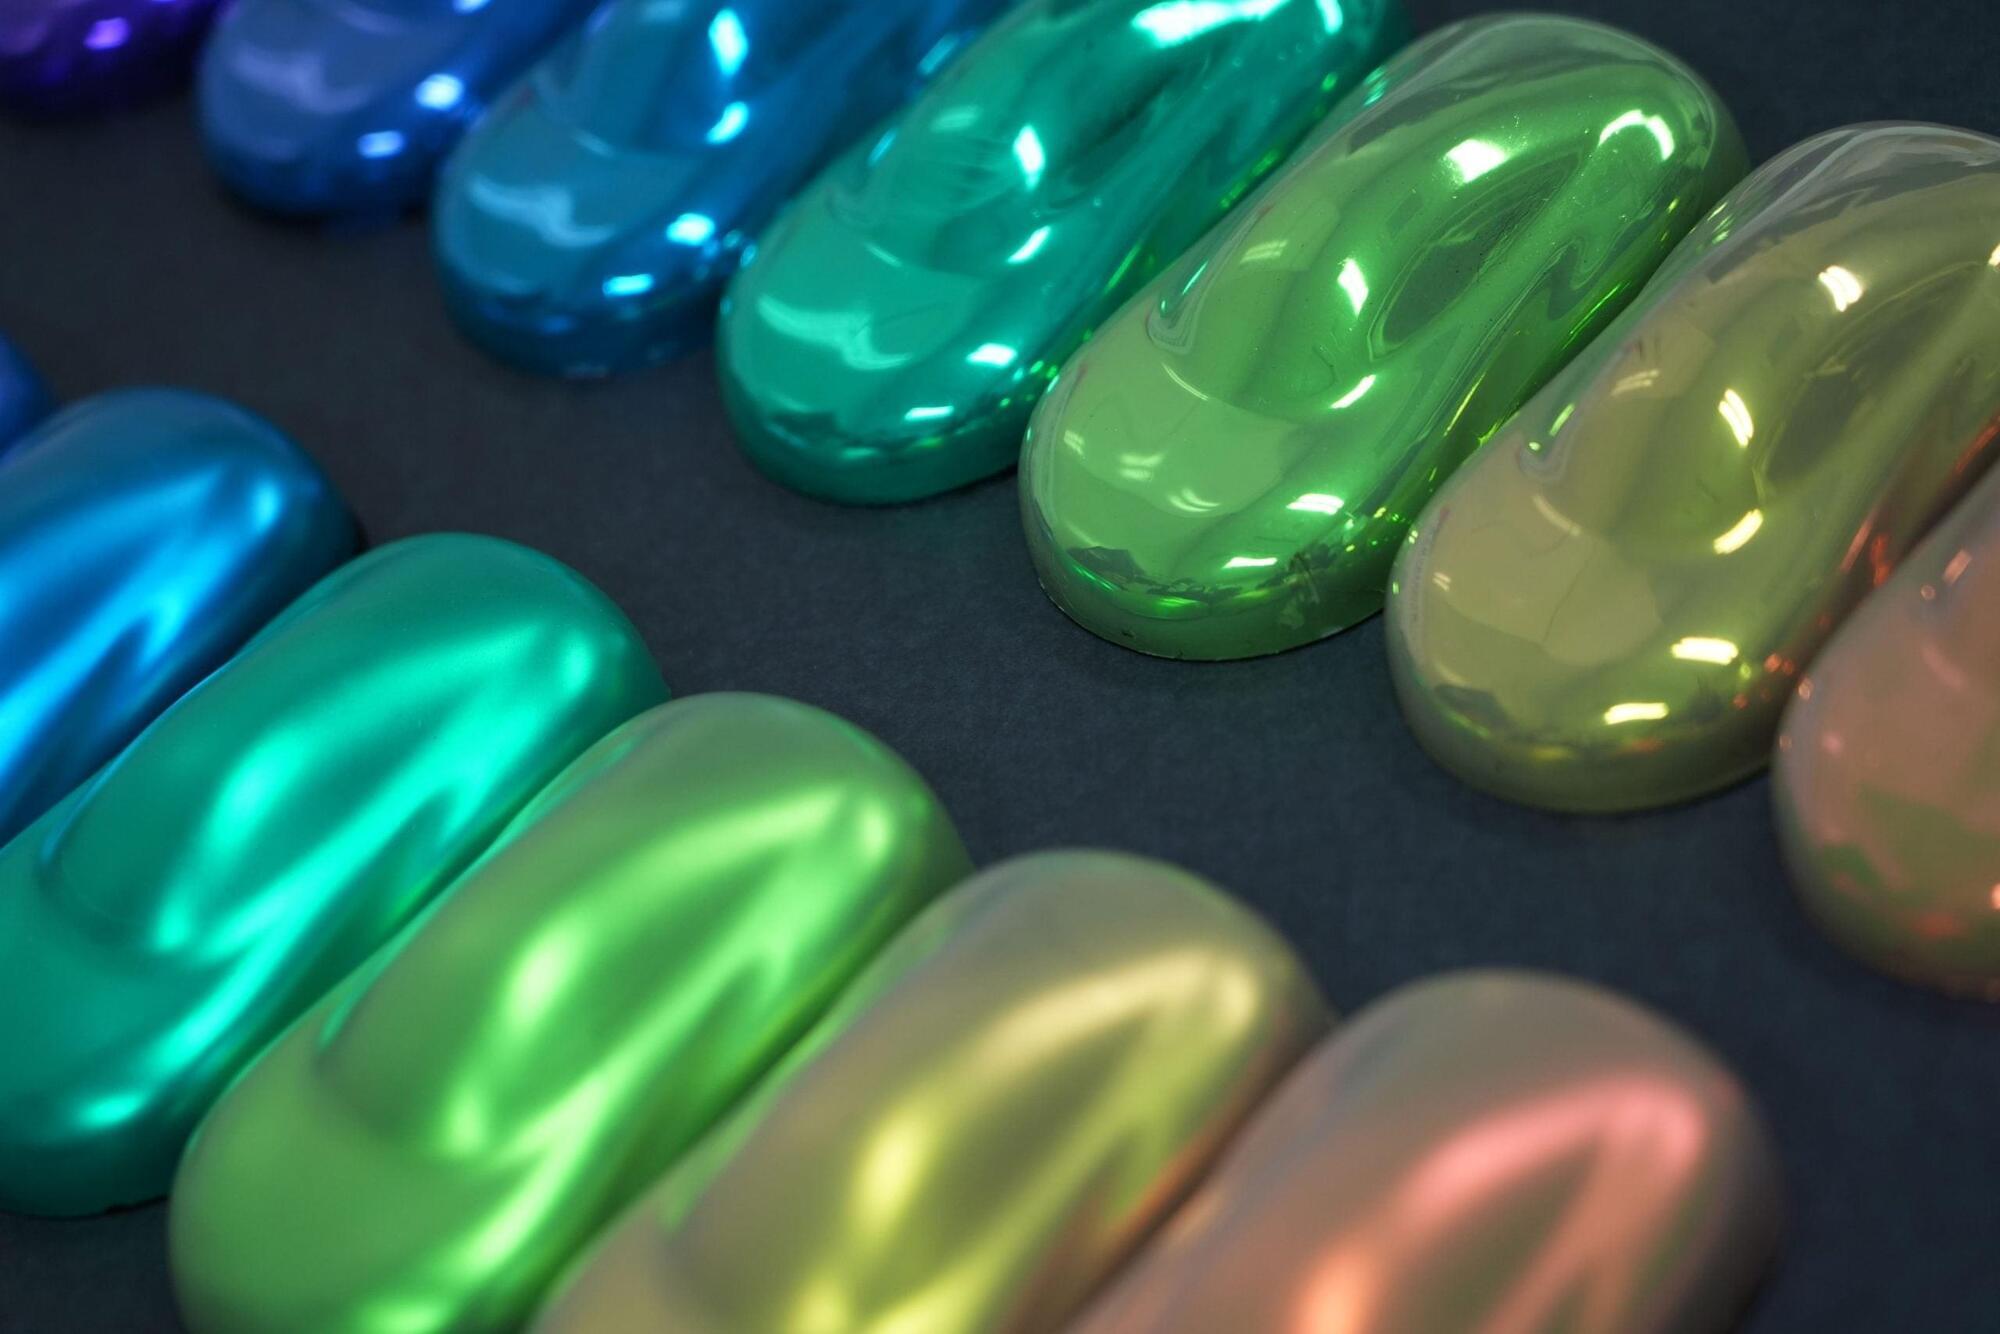
A new silicon-based coating could dramatically reduce the weight and environmental impact of conventional paints.
Get the latest international news and world events from around the world.
TeamViewer Flaw Lets Remote Computers Attack Users Who Connect to Control Them
15.83 fixes CVE-2026–111585, which lets malicious hosts crash remote viewers and may enable code execution on some platforms.
WordPress RCE Flaw Draws Nearly 63,000 Attack Attempts in Just 24 Hours
Attackers target a WordPress Core RCE flaw during upgrades, with Wordfence blocking 62,969 attempts in 24 hours. Patch available in 7.1.4.
Trezor Warns of Suspected Hardware Implant in One of Its Wallets Sold by CryptoBilis
Trezor warns CryptoBilis buyers to replace wallet recovery phrases after a customer reported a Safe 5 implant that transmits them over cellular.
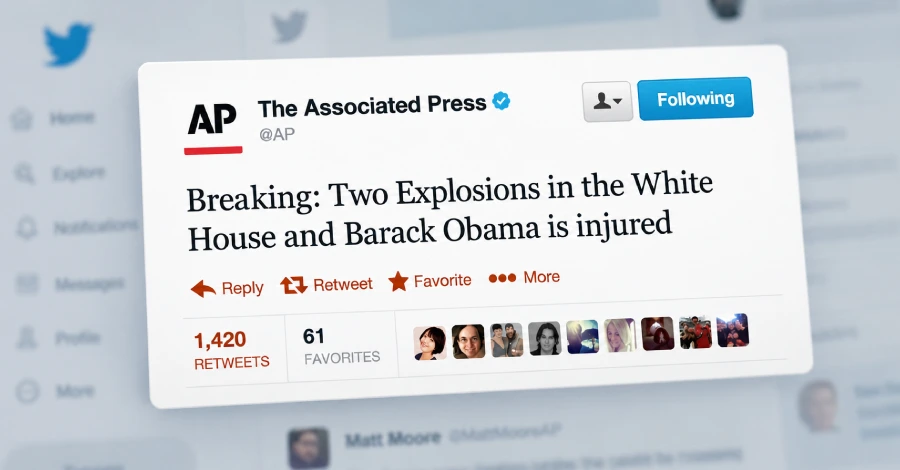
Syrian Hacker Behind Fake Tweet That Triggered $136 Billion Market Drop Gets 42 Months in Prison
Ahmad Umar Agha, a Syrian Electronic Army hacker known online as “Th3Pr0,” has been sentenced by a U.S. federal court to 42 months in prison for his role in a hacking conspiracy that targeted Western news outlets.
The conspiracy was organized and led by members of former Syrian President Bashar al-Assad’s inner circle, including the commander of Syria’s General Intelligence Directorate, the U.S. Justice Department said on October 29.
The pro-Assad Syrian Electronic Army began its attacks in 2011. Its members sent phishing emails to steal employees’ passwords, then used those passwords to deface websites, redirect web traffic, and hijack social media accounts, according to a 2014 FBI affidavit.
CISA Adds Actively Exploited GitLab RCE and Cisco Firewall DoS Flaws to KEV
CISA adds GitLab code execution and Cisco firewall DoS flaws to its KEV catalog, citing exploitation evidence and an Alpine Linux attack attempt.
Critical Linux kernel flaw allows remote root attacks on MPTCP servers
Security researchers at Anthropic have developed an exploit for a critical Linux kernel vulnerability that allows unauthenticated attackers to remotely execute commands as root on servers running Multipath TCP (MPTCP) listeners.
The flaw, tracked as CVE-2026–98432, also affects ordinary TCP connections, although remote code execution has not been publicly demonstrated on servers without an MPTCP listener.
Multipath TCP (MPTCP) is a TCP feature that lets a single connection use multiple network paths at the same time to improve performance and reliability. It is commonly used in environments where devices have multiple network connections, such as Wi-Fi and cellular networks.
Trezor warns of suspected crypto-theft implant in hardware wallet
Hardware wallet device maker Trezor has received credible reports about a suspected hardware crypto-theft implant in a Trezor Safe 5 sold by its reseller CryptoBilis in Southeast Asia.
Although the company has not yet received the device to examine it and confirm whether there is a malicious implant, it has warned potentially affected users to move their private keys and digital assets to known safe wallets.
Trezor wallets are physical devices that store cryptocurrency private keys and authorize transactions. Safe 5 is one of its latest models and is currently available for purchase from the official store.
Malicious Claude Code extension on Cursor planted SSH backdoors
A malicious version of Anthropic’s Claude Code VS Code extension was distributed through Cursor’s extension marketplace for approximately 11 hours on October 29, exposing up to 5,000 developers to malware designed to install persistent SSH backdoors.
The extension used the version number 2.1.313 and was distributed between 2:27 a.m. and 1:35 p.m. Pacific Time.
Cursor is an AI-powered code editor built from Microsoft’s open-source Visual Studio Code (VS Code), with support for VS Code extensions. Anthropic’s Claude Code extension brings its AI coding assistant directly into compatible editors, helping developers write and debug code using natural-language instructions.
CISA says max severity GitLab flaw now exploited in the wild
Attackers have started exploiting a maximum-severity GitLab vulnerability patched earlier this month, according to the US Cybersecurity and Infrastructure Security Agency (CISA).
Tracked as CVE-2026–97229, this critical security flaw was discovered by a security researcher using the ‘joaxcar’ handle in the CI/CD Regular Expression Compiler, which parses, compiles, and evaluates regular expressions in pipeline configuration files.
CVE-2026–97229 stems from an integer overflow weakness and could let remote attackers run arbitrary code on targeted instances via a maliciously crafted regular expression in a CI/CD configuration, due to insufficient expression validation.