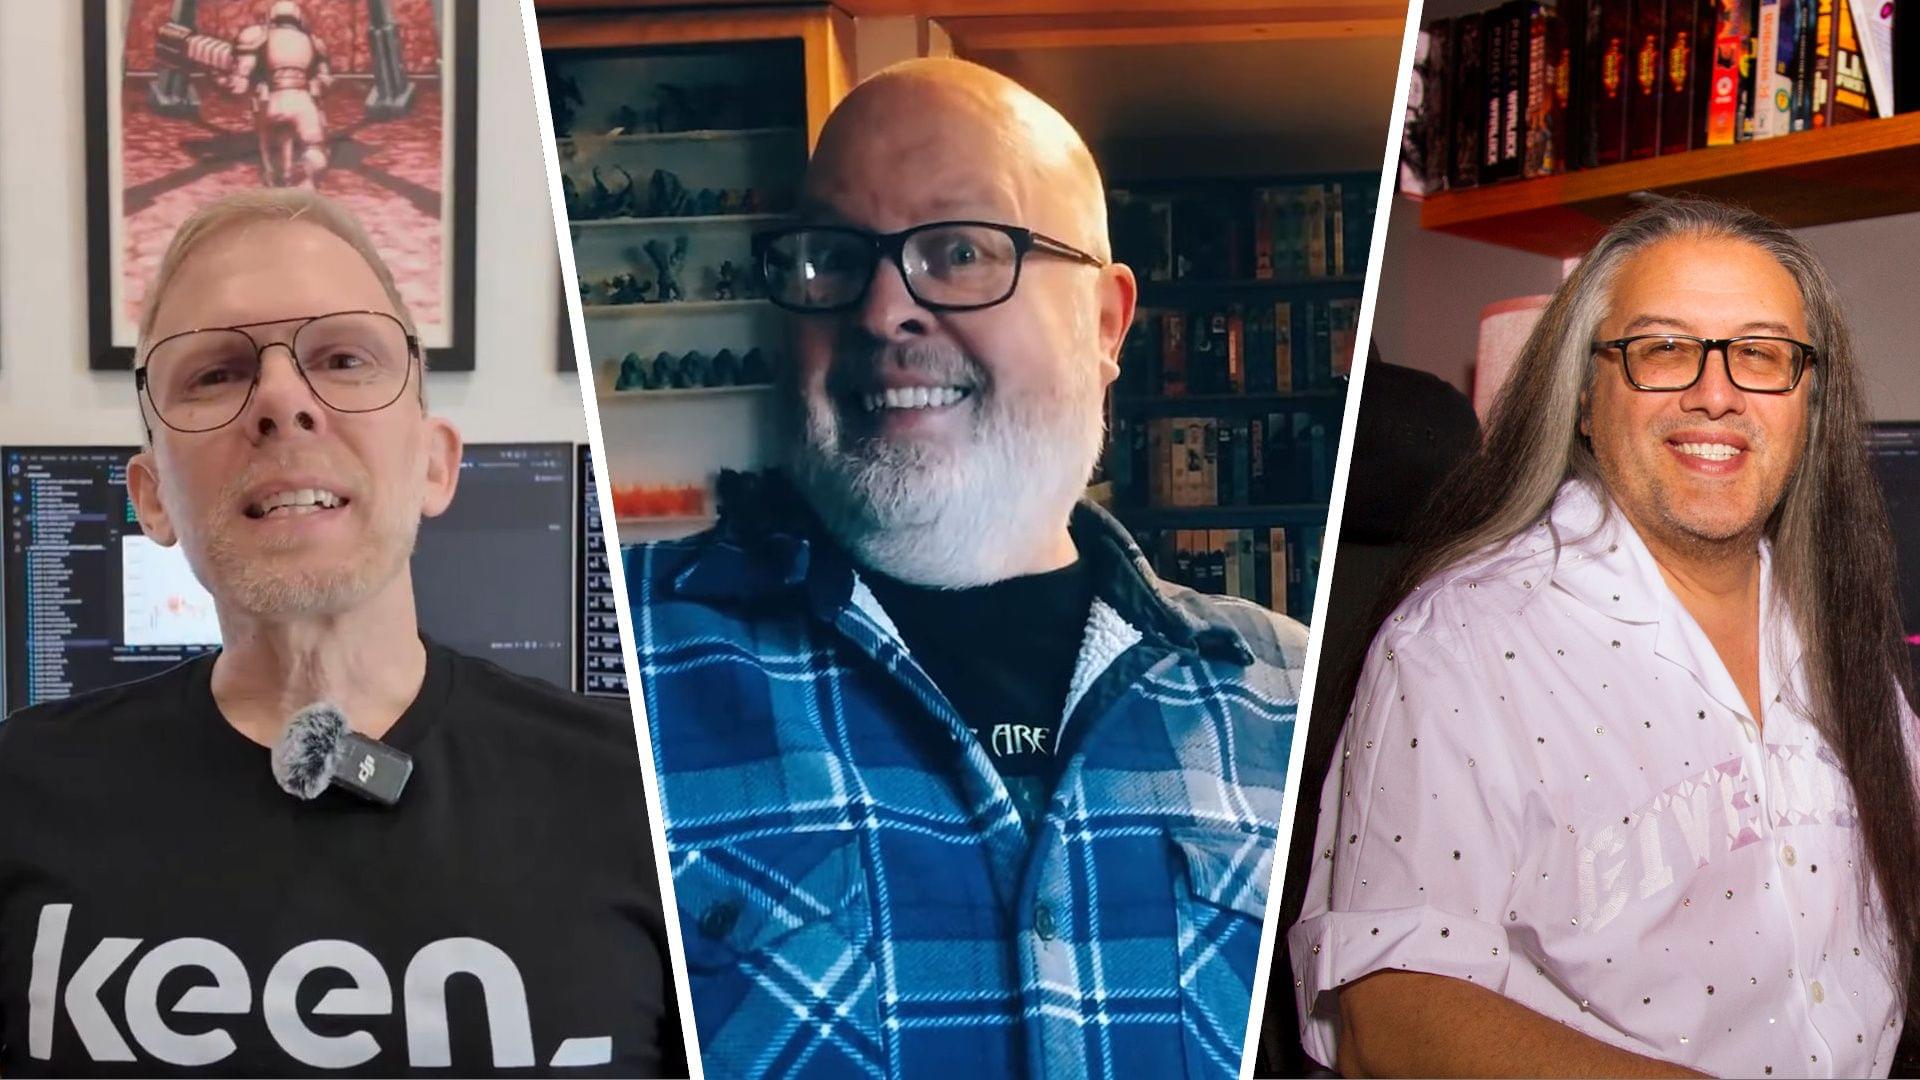
Three of the principals from the early days of id Software shared some faintly maudlin but ultimately uplifting reminiscences from those long-ago days.
Category: futurism – Page 61

Room-temperature laser hits record stability with 68-cm optical cavity
Scientists at NPL have demonstrated the best-reported laser frequency stability achieved with an optical reference cavity operating at room temperature, marking a major advance in ultrastable laser technology. The team’s results have been published in Optica.
Ultrastable lasers produce light of exceptional spectral purity and are a critical enabling technology for optical atomic clocks. These are the next generation of atomic clocks based on atomic transitions in the optical domain. These clocks underpin the most precise timekeeping ever achieved and are central to future technologies ranging from advanced navigation to fundamental physics.
The NPL team measured a fractional frequency instability of 4 × 10⁻¹⁷, achieved for the first time using a room-temperature optical reference cavity. Until now, comparable performance had only been realized internationally using complex cryogenic systems.

Scientists Found a Wordle Trick That Solves 99% of Puzzles
Researchers turned a classic theory of information into a near-perfect Wordle strategy that solves 99% of puzzles.

Cordyceps CI/CD Flaws Expose 300+ GitHub Repositories to Supply-Chain Attacks
Researchers found Cordyceps CI/CD flaws affecting 300+ repositories, enabling code execution, credential theft, and supply chain risks.

Cisco Catalyst SD-WAN Zero-Day CVE-2026–20245 Exploited to Gain Root Access
Mandiant says CVE-2026–20245 was exploited as a Cisco SD-WAN zero-day to escalate admin access to root on a provider network.

CISA Warns Critical Lantronix EDS5000 Flaw Is Being Actively Exploited
CISA says CVE-2025–67038 in Lantronix EDS5000 devices is under active exploitation and urges federal agencies to patch by June 26, 2026.
Mandiant reveals how Cisco SD-WAN zero-day attacks gained root access
New details have been revealed on how hackers exploited a Cisco Catalyst SD-WAN vulnerability tracked as CVE-2026–20245 in zero-day attacks to create rogue root accounts on targeted devices.
The CVE-2026–20245 vulnerability is a high-severity command injection flaw in Cisco Catalyst SD-WAN Manager (vManage), Controller (vSmart), and Validator (vBond) that allows authenticated attackers to execute arbitrary commands as root by uploading a crafted file.
Cisco said the vulnerability stemmed from insufficient validation of user-supplied input and could be exploited by authenticated attackers with local access to affected devices.

FortiBleed Targeted FortiGate Firewalls in 110 Million-Credential Harvesting Operation
FortiBleed targeted 430,000 FortiGate firewalls with sniffers and brute-force pipelines that identified over 110 million credentials.

GitHub Updates actions/checkout to Block Common Pwn Request Attack Patterns
GitHub’s actions/checkout v7 now blocks risky fork PR checkouts in privileged workflows to reduce common pwn request attacks.

Roundup of Interesting Research Papers #15
My fifteenth installment of interesting research papers that I have read over the past few weeks and would like to share with my community.